



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An email recipient is unable to open a message encrypted through PKI that was sent from another organization. Which of the following does the recipient need to decrypt the message?
(Multiple Choice)
4.8/5  (66)
(66) An organization discovers that unauthorized applications have been installed on company-provided mobile phones. The organization issues these devices, but some users have managed to bypass the security controls. Which of the following is the MOST likely issue, and how can the organization BEST prevent this from happening?
(Multiple Choice)
4.8/5 (87)
(87) Employees receive a benefits enrollment email from the company's human resources department at the beginning of each year. Several users have reported receiving the email but are unable to log in to the website with their usernames and passwords. Users who enter the URL for the human resources website can log in without issue. Which of the following security issues is occurring?
(Multiple Choice)
4.9/5 (83)
(83) A security administrator has been tasked with improving the overall security posture related to desktop machines on the network. An auditor has recently that several machines with confidential customer information displayed in the screens are left unattended during the course of the day. Which of the following could the security administrator implement to reduce the risk associated with the finding?
(Multiple Choice)
4.7/5 (78)
(78) A network administrator is creating a new network for an office. For security purposes, each department should have its resources isolated from every other department but be able to communicate back to central servers. Which of the following architecture concepts would BEST accomplish this?
(Multiple Choice)
4.9/5 (84)
(84) Which of the following is the GREATEST risk to a company by allowing employees to physically bring their personal smartphones to work?
(Multiple Choice)
4.8/5 (76)
(76) Which of the following access management concepts is MOST closely associated with the use of a password or PIN??
(Multiple Choice)
4.8/5 (80)
(80) A security technician has been receiving alerts from several servers that indicate load balancers have had a significant increase in traffic. The technician initiates a system scan. The scan results illustrate that the disk space on several servers has reached capacity. The scan also indicates that incoming internet traffic to the servers has increased. Which of the following is the MOST likely cause of the decreased disk space?
(Multiple Choice)
4.8/5 (81)
(81) An organization handling highly confidential information needs to update its systems. Which of the following is the BEST method to prevent data compromise?
(Multiple Choice)
4.7/5 (84)
(84) A supervisor in your organization was demoted on Friday afternoon. The supervisor had the ability to modify the contents of a confidential database, as well as other managerial permissions. On Monday morning, the database administrator reported that log files indicated that several records were missing from the database. Which of the following risk mitigation strategies should have been implemented when the supervisor was demoted?
(Multiple Choice)
5.0/5 (74)
(74) Joe notices there are several user accounts on the local network generating spam with embedded malicious code. Which of the following technical control should Joe put in place to BEST reduce these incidents?
(Multiple Choice)
4.9/5 (78)
(78) A security analyst has received the following alert snippet from the HIDS appliance: 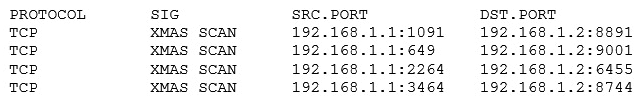 Given the above logs, which of the following is the cause of the attack?
 (Multiple Choice)
5.0/5 (73)
(73) A company is deploying smartphones for its mobile salesforce. These devices are for personal and business use but are owned by the company. Sales personnel will save new customer data via a custom application developed for the company. This application will integrate with the contact information stored in the smartphones and will populate new customer records onto it. The customer application's data is encrypted at rest, and the application's connection to the back office system is considered secure. The Chief Information Security Officer (CISO) has concerns that customer contact information may be accidentally leaked due to the limited security capabilities of the devices and the planned controls. Which of the following will be the MOST efficient security control to implement to lower this risk?
(Multiple Choice)
4.8/5 (84)
(84) An analyst is currently looking at the following output: 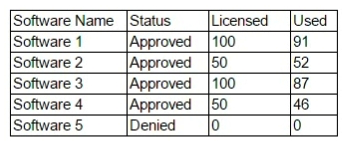 Which of the following security issues has been discovered based on the output?
 (Multiple Choice)
4.9/5 (85)
(85) A company is terminating an employee for misbehavior. Which of the following steps is MOST important in the process of disengagement from this employee?
(Multiple Choice)
4.8/5 (78)
(78) Which of the following metrics are used to calculate the SLE? (Choose two.)
(Multiple Choice)
4.9/5 (73)
(73) A chief Financial Officer (CFO) has asked the Chief Information Officer (CISO) to provide responses to a recent audit report detailing deficiencies in the organization security controls. The CFO would like to know ways in which the organization can improve its authorization controls. Given the request by the CFO, which of the following controls should the CISO focus on in the report? (Select Three)
(Multiple Choice)
4.7/5 (70)
(70) A malicious system continuously sends an extremely large number of SYN packets to a server. Which of the following BEST describes the resulting effect?
(Multiple Choice)
4.8/5 (83)
(83) The security administrator receives an email on a non-company account from a coworker stating that some reports are not exporting correctly. Attached to the email was an example report file with several customers' names and credit card numbers with the PIN. Which of the following is the BEST technical controls that will help mitigate this risk of disclosing sensitive data?
(Multiple Choice)
4.8/5 (78)
(78) A security analyst wishes to increase the security of an FTP server. Currently, all traffic to the FTP server is unencrypted. Users connecting to the FTP server use a variety of modern FTP client software. The security analyst wants to keep the same port and protocol, while also still allowing unencrypted connections. Which of the following would BEST accomplish these goals?
(Multiple Choice)
4.8/5 (91)
(91) Showing 1121 - 1140 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)