



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An organization's internal auditor discovers that large sums of money have recently been paid to a vendor that management does not recognize. The IT security department is asked to investigate the organizations the organization's ERP system to determine how the accounts payable module has been used to make these vendor payments. The IT security department finds the following security configuration for the accounts payable module: New Vendor Entry - Required Role: Accounts Payable Clerk New Vendor Approval - Required Role: Accounts Payable Clerk Vendor Payment Entry - Required Role: Accounts Payable Clerk Vendor Payment Approval - Required Role: Accounts Payable Manager Which of the following changes to the security configuration of the accounts payable module would BEST mitigate the risk?
(Multiple Choice)
4.9/5  (78)
(78) Joe, a security administrator, needs to extend the organization's remote access functionality to be used by staff while travelling. Joe needs to maintain separate access control functionalities for internal, external, and VOIP services. Which of the following represents the BEST access technology for Joe to use?
(Multiple Choice)
4.8/5 (85)
(85) An auditor requiring an organization to perform real-time validation of SSL certificates. Which of the following should the organization implement?
(Multiple Choice)
5.0/5 (77)
(77) The Chief Security Officer (CSO) at a major hospital wants to implement SSO to help improve security in the environment and protect patient data, particularly at shared terminals. The Chief Risk Officer (CRO) is concerned that training and guidance have not been provided to frontline staff, and a risk analysis has not been performed. Which of the following is the MOST likely cause of the CRO's concerns?
(Multiple Choice)
4.8/5 (74)
(74) An organization has hired a new remote workforce. Many new employees are reporting that they are unable to access the shared network resources while traveling. They need to be able to travel to and from different locations on a weekly basis. Shared offices are retained at the headquarters location. The remote workforce will have identical file and system access requirements, and must also be able to log in to the headquarters location remotely. Which of the following BEST represent how the remote employees should have been set up initially? (Choose two.)
(Multiple Choice)
4.7/5 (78)
(78) A security administrator wants to determine if a company's web servers have the latest operating system and application patches installed. Which of the following types of vulnerability scans should be conducted?
(Multiple Choice)
4.9/5 (90)
(90) A software development company needs to augment staff by hiring consultants for a high-stakes project. The project has the following requirements: Consultants will have access to highly confidential, proprietary data. Consultants will not be provided with company-owned assets. Work needs to start immediately. Consultants will be provided with internal email addresses for communications. Which of the following solutions is the BEST method for controlling data exfiltration during this project?
(Multiple Choice)
4.8/5 (89)
(89) Ann, a user, states that her machine has been behaving erratically over the past week. She has experienced slowness and input lag and found text files that appear to contain pieces of her emails or online conversations with coworkers. The technician runs a standard virus scan but detects nothing. Which of the following types of malware has infected the machine?
(Multiple Choice)
4.8/5 (75)
(75) A company occupies the third floor of a leased building that has other tenants. The path from the demarcation point to the company's controlled space runs through unsecured areas managed by other companies. Which of the following could be used to protect the company's cabling as it passes through uncontrolled spaces?
(Multiple Choice)
4.7/5 (73)
(73) A third-party penetration testing company was able to successfully use an ARP cache poison technique to gain root access on a server. The tester successfully moved to another server that was not in the original network. Which of the following is the MOST likely method used to gain access to the other host?
(Multiple Choice)
4.8/5 (72)
(72) Joe recently assumed the role of data custodian for this organization. While cleaning out an unused storage safe, he discovers several hard drives that are labeled "unclassified" and awaiting destruction. The hard drives are obsolete and cannot be installed in any of his current computing equipment. Which of the following is the BEST method for disposing of the hard drives?
(Multiple Choice)
4.8/5 (82)
(82) A security analyst is securing smartphones and laptops for a highly mobile workforce. Priorities include: Remote wipe capabilities Geolocation services Patch management and reporting Mandatory screen locks Ability to require passcodes and pins Ability to require encryption Which of the following would BEST meet these requirements?
(Multiple Choice)
4.9/5 (60)
(60) After being alerted to potential anomalous activity related to trivial DNS lookups, a security analyst looks at the following output of implemented firewall rules: 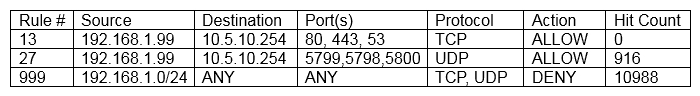 The analyst notices that the expected policy has no hit count for the day. Which of the following MOST likely occurred?
 (Multiple Choice)
4.8/5 (69)
(69) An employee uses RDP to connect back to the office network. If RDP is misconfigured, which of the following security exposures would this lead to?
(Multiple Choice)
4.9/5 (87)
(87) A security team has completed the installation of a new server. The OS and applications have been patched and tested, and the server is ready to be deployed. Which of the following actions should be taken before deploying the new server?
(Multiple Choice)
4.9/5 (76)
(76) Despite having implemented password policies, users continue to set the same weak passwords and reuse old passwords. Which of the following technical controls would help prevent these policy violations? (Select two.)
(Multiple Choice)
4.9/5 (80)
(80) A security administrator is diagnosing a server where the CPU utilization is at 100% for 24 hours. The main culprit of CPU utilization is the antivirus program. Which of the following issue could occur if left unresolved? (Select TWO)
(Multiple Choice)
4.9/5 (89)
(89) A new Chief Information Officer (CIO) has been reviewing the badging procedures and decides to write a policy that all employees must have their badges rekeyed at least annually. Which of the following controls BEST describes this policy?
(Multiple Choice)
4.9/5 (85)
(85) A security analyst is reviewing the password policy for a service account that is used for a critical network service. The password policy for this account is as follows: 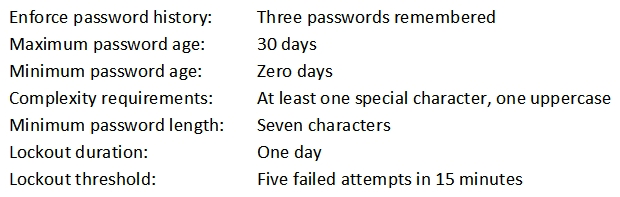 Which of the following adjustments would be the MOST appropriate for the service account?
 (Multiple Choice)
4.8/5 (77)
(77) Showing 601 - 620 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)