



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A black hat hacker is enumerating a network and wants to remain covert during the process. The hacker initiates a vulnerability scan. Given the task at hand the requirement of being covert, which of the following statements BEST indicates that the vulnerability scan meets these requirements?
(Multiple Choice)
4.8/5  (72)
(72) Which of the following is a random value appended to a credential that makes the credential less susceptible to compromise when hashed?
(Multiple Choice)
4.9/5 (80)
(80) A security analyst is hardening a large-scale wireless network. The primary requirements are the following: Must use authentication through EAP-TLS certificates Must use an AAA server Must use the most secure encryption protocol Given these requirements, which of the following should the analyst implement and recommend? (Select TWO.)
(Multiple Choice)
5.0/5 (76)
(76) A company hired a firm to test the security posture of its database servers and determine if any vulnerabilities can be exploited. The company provided limited information pertaining to the infrastructure and database server. Which of the following forms of testing does this BEST describe?
(Multiple Choice)
4.7/5 (74)
(74) Which of the following occurs when the security of a web application relies on JavaScript for input validation?
(Multiple Choice)
4.9/5 (75)
(75) An employee in the finance department receives an email, which appears to come from the Chief Financial Officer (CFO), instructing the employee to immediately wire a large sum of money to a vendor. Which of the following BEST describes the principles of social engineering used? (Choose two.)
(Multiple Choice)
4.8/5 (85)
(85) A security analyst observes the following events in the logs of an employee workstation: 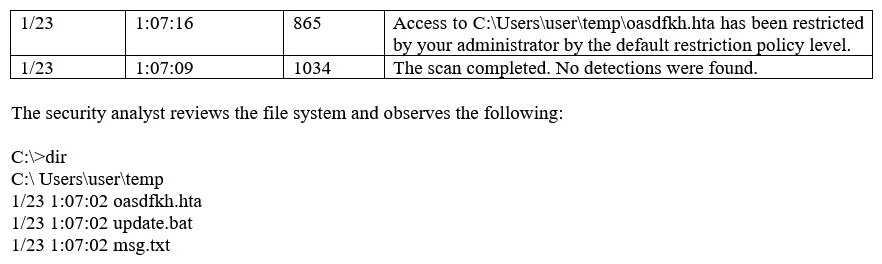 Given the information provided, which of the following MOST likely occurred on the workstation?
 (Multiple Choice)
4.9/5 (81)
(81) A security technician is configuring an access management system to track and record user actions. Which of the following functions should the technician configure?
(Multiple Choice)
4.9/5 (64)
(64) A user from the financial aid office is having trouble interacting with the finaid directory on the university's ERP system. The systems administrator who took the call ran a command and received the following output: 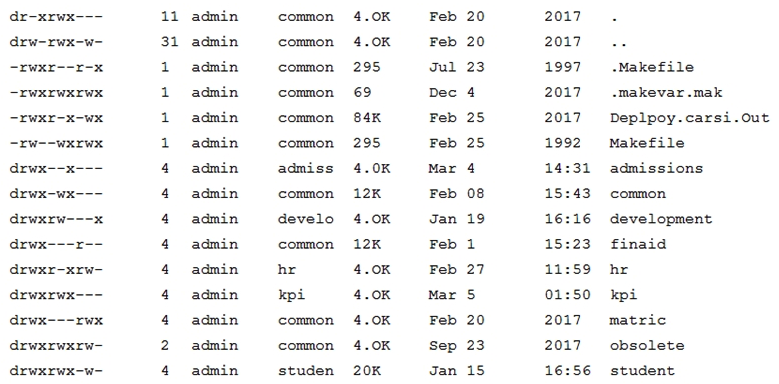 Subsequently, the systems administrator has also confirmed the user is a member of the finaid group on the ERP system. Which of the following is the MOST likely reason for the issue?
 (Multiple Choice)
4.9/5 (72)
(72) A technician is investigating a potentially compromised device with the following symptoms: Browser slowness Frequent browser crashes Hourglass stuck New search toolbar Increased memory consumption Which of the following types of malware has infected the system?
(Multiple Choice)
4.7/5 (93)
(93) In determining when it may be necessary to perform a credentialed scan against a system instead of a non-credentialed scan, which of the following requirements is MOST likely to influence this decision?
(Multiple Choice)
4.9/5 (79)
(79) A company wants to ensure confidential data from storage media is sanitized in such a way that the drive cannot be reused. Which of the following method should the technician use?
(Multiple Choice)
4.7/5 (82)
(82) Which of the following is the MOST significant difference between intrusive and non-intrusive vulnerability scanning?
(Multiple Choice)
5.0/5 (82)
(82) Which of the following types of penetration test will allow the tester to have access only to password hashes prior to the penetration test?
(Multiple Choice)
4.8/5 (84)
(84) A network administrator at a small office wants to simplify the configuration of mobile clients connecting to an encrypted wireless network. Which of the following should be implemented in the administrator does not want to provide the wireless password or he certificate to the employees?
(Multiple Choice)
4.9/5 (83)
(83) Ann, a college professor, was recently reprimanded for posting disparaging remarks re-grading her coworkers on a web site. Ann stated that she was not aware that the public was able to view her remakes. Which of the following security-related trainings could have made Ann aware of the repercussions of her actions?
(Multiple Choice)
4.8/5 (72)
(72) A security administrator needs to conduct a full inventory of all encryption protocols and cipher suites. Which of the following tools will the security administrator use to conduct this inventory MOST efficiently?
(Multiple Choice)
4.9/5 (84)
(84) After a systems administrator installed and configured Kerberos services, several users experienced authentication issues. Which of the following should be installed to resolve these issues?
(Multiple Choice)
4.8/5 (87)
(87) A security auditor is performing a vulnerability scan to find out if mobile applications used in the organization are secure. The auditor discovers that one application has been accessed remotely with no legitimate account credentials. After investigating, it seems the application has allowed some users to bypass authentication of that application. Which of the following types of malware allow such a compromise to take place? (Choose two.)
(Multiple Choice)
4.7/5 (82)
(82) Showing 121 - 140 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)