



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A security technician would like to obscure sensitive data within a file so that it can be transferred without causing suspicion. Which of the following technologies would BEST be suited to accomplish this?
(Multiple Choice)
4.9/5  (77)
(77) A development team has adopted a new approach to projects in which feedback is iterative and multiple iterations of deployments are provided within an application's full life cycle. Which of the following software development methodologies is the development team using?
(Multiple Choice)
4.7/5 (83)
(83) An application developer is designing an application involving secure transports from one service to another that will pass over port 80 for a request. Which of the following secure protocols is the developer MOST likely to use?
(Multiple Choice)
4.8/5 (81)
(81) A company exchanges information with a business partner. An annual audit of the business partner is conducted against the SLA in order to verify:
(Multiple Choice)
4.7/5 (76)
(76) A security analyst is checking log files and finds the following entries: 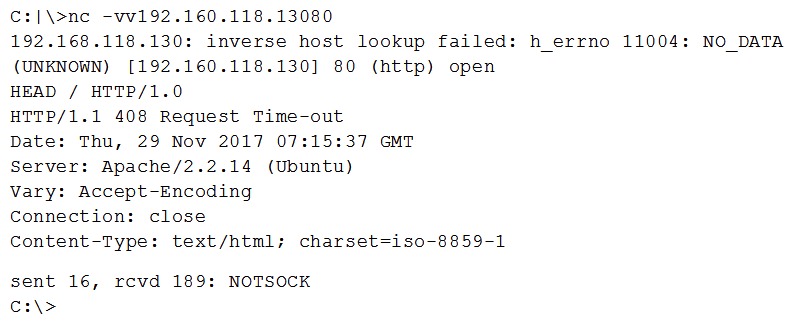 Which of the following is MOST likely happening?
 (Multiple Choice)
4.9/5 (76)
(76) An accountant is attempting to log in to the internal accounting system and receives a message that the website's certificate is fraudulent. The accountant finds instructions for manually installing the new trusted root onto the local machine. Which of the following would be the company's BEST option for this situation in the future?
(Multiple Choice)
4.9/5 (78)
(78) A government organization recently contacted three different vendors to obtain cost quotes for a desktop PC refresh. The quote from one of the vendors was significantly lower than the other two and was selected for the purchase. When the PCs arrived, a technician determined some NICs had been tampered with. Which of the following MOST accurately describes the security risk presented in this situation?
(Multiple Choice)
5.0/5 (66)
(66) A security analyst accesses corporate web pages and inputs random data in the forms. The response received includes the type of database used and SQL commands that the database accepts. Which of the following should the security analyst use to prevent this vulnerability?
(Multiple Choice)
4.9/5 (89)
(89) An audit found that an organization needs to implement job rotation to be compliant with regulatory requirements. To prevent unauthorized access to systems after an individual changes roles or departments, which of the following should the organization implement?
(Multiple Choice)
4.8/5 (84)
(84) Which of the following can be used to control specific commands that can be executed on a network infrastructure device?
(Multiple Choice)
5.0/5 (92)
(92) A technician has installed new vulnerability scanner software on a server that is joined to the company domain. The vulnerability scanner is able to provide visibility over the patch posture of all company's clients. Which of the following is being used?
(Multiple Choice)
4.9/5 (86)
(86) A new firewall has been places into service at an organization. However, a configuration has not been entered on the firewall. Employees on the network segment covered by the new firewall report they are unable to access the network. Which of the following steps should be completed to BEST resolve the issue?
(Multiple Choice)
4.8/5 (70)
(70) After a security incident, management is meeting with involved employees to document the incident and its aftermath. Which of the following BEST describes this phase of the incident response process?
(Multiple Choice)
4.8/5 (85)
(85) Which of the following explains why vendors publish MD5 values when they provide software patches for their customers to download over the Internet?
(Multiple Choice)
4.9/5 (58)
(58) After running an online password cracking tool, an attacker recovers the following password: gh ;j SKSTOi;618& Based on the above information, which of the following technical controls have been implemented? (Choose two.)
(Multiple Choice)
4.8/5 (67)
(67) Which of the following represents a multifactor authentication system?
(Multiple Choice)
4.7/5 (89)
(89) A consultant has been tasked to assess a client's network. The client reports frequent network outages. Upon viewing the spanning tree configuration, the consultant notices that an old and law performing edge switch on the network has been elected to be the root bridge. Which of the following explains this scenario?
(Multiple Choice)
4.9/5 (91)
(91) A security administrator learns that PII, which was gathered by the organization, has been found in an open forum. As a result, several C-level executives found their identities were compromised, and they were victims of a recent whaling attack. Which of the following would prevent these problems in the future? (Choose two.)
(Multiple Choice)
4.8/5 (85)
(85) A security analyst is attempting to identify vulnerabilities in a customer's web application without impacting the system or its data. Which of the following BEST describes the vulnerability scanning concept performed?
(Multiple Choice)
4.9/5 (79)
(79) A government agency with sensitive information wants to virtualize its infrastructure. Which of the following cloud deployment models BEST fits the agency's needs?
(Multiple Choice)
4.8/5 (83)
(83) Showing 901 - 920 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)