



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


Two users need to securely share encrypted files via email. Company policy prohibits users from sharing credentials or exchanging encryption keys. Which of the following can be implemented to enable users to share encrypted data while abiding by company policies?
(Multiple Choice)
4.9/5  (78)
(78) An organization has an account management policy that defines parameters around each type of account. The policy specifies different security attributes, such as longevity, usage auditing, password complexity, and identity proofing. The goal of the account management policy is to ensure the highest level of security while providing the greatest availability without compromising data integrity for users. Which of the following account types should the policy specify for service technicians from corporate partners?
(Multiple Choice)
4.8/5 (86)
(86) The security administrator has noticed cars parking just outside of the building fence line. Which of the following security measures can the administrator use to help protect the company's WiFi network against war driving? (Select TWO)
(Multiple Choice)
4.7/5 (67)
(67) A Chief Information Officer (CIO) drafts an agreement between the organization and its employees. The agreement outlines ramifications for releasing information without consent and/or approvals. Which of the following BEST describes this type of agreement?
(Multiple Choice)
4.8/5 (78)
(78) A company is experiencing an increasing number of systems that are locking up on Windows startup. The security analyst clones a machine, enters into safe mode, and discovers a file in the startup process that runs Wstart.bat. @echo off :asdhbawdhbasdhbawdhb start notepad.exe start calculator.exe goto asdhbawdhbasdhbawdhb Given the file contents and the system's issues, which of the following types of malware is present?
(Multiple Choice)
4.8/5 (71)
(71) A systems administrator wants to replace the process of using a CRL to verify certificate validity. Frequent downloads are becoming problematic. Which of the following would BEST suit the administrator's needs?
(Multiple Choice)
4.9/5 (86)
(86) A workstation puts out a network request to locate another system. Joe, a hacker on the network, responds before the real system does, and he tricks the workstation into communicating with him. Which of the following BEST describes what occurred?
(Multiple Choice)
4.7/5 (82)
(82) A company's loss control department identifies theft as a recurring loss type over the past year. Based on the department's report, the Chief Information Officer (CIO) wants to detect theft of datacenter equipment. Which of the following controls should be implemented?
(Multiple Choice)
4.8/5 (79)
(79) A company is performing an analysis of the corporate enterprise network with the intent of identifying any one system, person, function, or service that, when neutralized, will cause or cascade disproportionate damage to the company's revenue, referrals, and reputation. Which of the following an element of the BIA that this action is addressing?
(Multiple Choice)
4.9/5 (75)
(75) Which of the following outcomes is a result of proper error-handling procedures in secure code?
(Multiple Choice)
4.9/5 (76)
(76) A company wants to provide centralized authentication for its wireless system. The wireless authentication system must integrate with the directory back end. Which of the following is a AAA solution that will provide the required wireless authentication?
(Multiple Choice)
4.9/5 (73)
(73) A security analyst reviews the following output: 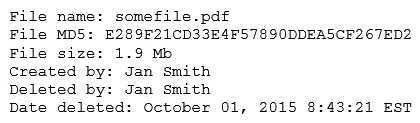 The analyst loads the hash into the SIEM to discover if this hash is seen in other parts of the network. After inspecting a large number of files, the security analyst reports the following:
 Which of the following is the MOST likely cause of the hash being found in other areas?
The analyst loads the hash into the SIEM to discover if this hash is seen in other parts of the network. After inspecting a large number of files, the security analyst reports the following: Which of the following is the MOST likely cause of the hash being found in other areas? (Multiple Choice)
4.9/5 (77)
(77) Which of the following best describes routine in which semicolons, dashes, quotes, and commas are removed from a string?
(Multiple Choice)
4.8/5 (80)
(80) Which of the following encryption methods does PKI typically use to securely protect keys?
(Multiple Choice)
4.9/5 (89)
(89) An organization has a policy in place that states the person who approves firewall controls/changes cannot be the one implementing the changes. Which of the following is this an example of?
(Multiple Choice)
4.9/5 (91)
(91) A security analyst is assessing a small company's internal servers against recommended security practices. Which of the following should the analyst do to conduct the assessment? (Choose two.)
(Multiple Choice)
4.8/5 (60)
(60) Which of the following encryption algorithms require one encryption key? (Choose two.)
(Multiple Choice)
4.9/5 (83)
(83) An administrator has concerns regarding the traveling sales team who works primarily from smart phones. Given the sensitive nature of their work, which of the following would BEST prevent access to the data in case of loss or theft?
(Multiple Choice)
4.8/5 (78)
(78) A company is performing an analysis of the corporate enterprise network with the intent of identifying what will cause losses in revenue, referrals, and/or reputation when out of commission. Which of the following is an element of a BIA that is being addressed?
(Multiple Choice)
4.9/5 (86)
(86) A system administrator is reviewing the following information from a compromised server. 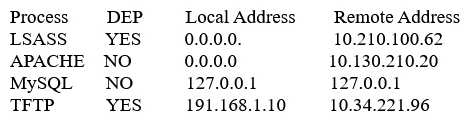 Given the above information, which of the following processes was MOST likely exploited via remote buffer overflow attack?
 (Multiple Choice)
4.9/5 (77)
(77) Showing 741 - 760 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)