



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


Which of the following is the LEAST secure hashing algorithm?
(Multiple Choice)
4.9/5  (75)
(75) An organization's employees currently use three different sets of credentials to access multiple internal resources. Management wants to make this process less complex. Which of the following would be the BEST option to meet this goal?
(Multiple Choice)
5.0/5 (77)
(77) A small enterprise decides to implement a warm site to be available for business continuity in case of a disaster. Which of the following BEST meets its requirements?
(Multiple Choice)
4.9/5 (76)
(76) A security administrator is performing a risk assessment on a legacy WAP with a WEP-enabled wireless infrastructure. Which of the following should be implemented to harden the infrastructure without upgrading the WAP?
(Multiple Choice)
4.7/5 (78)
(78) A director of IR is reviewing a report regarding several recent breaches. The director compiles the following statistic's -Initial IR engagement time frame -Length of time before an executive management notice went out -Average IR phase completion The director wants to use the data to shorten the response time. Which of the following would accomplish this?
(Multiple Choice)
5.0/5 (74)
(74) A security analyst observes the following events in the logs of an employee workstation: 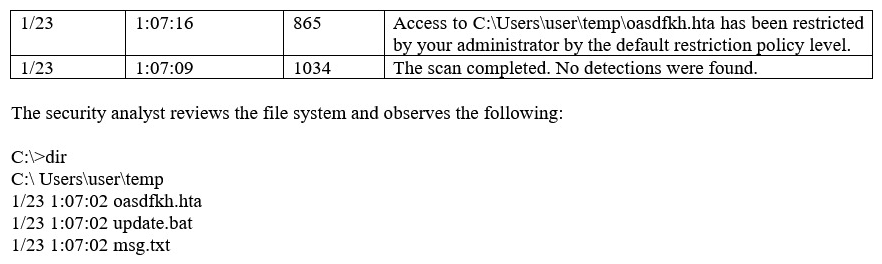 Given the information provided, which of the following MOST likely occurred on the workstation?
 (Multiple Choice)
4.9/5 (82)
(82) A help desk is troubleshooting user reports that the corporate website is presenting untrusted certificate errors to employees and customers when they visit the website. Which of the following is the MOST likely cause of this error, provided the certificate has not expired?
(Multiple Choice)
4.9/5 (80)
(80) A network administrator was concerned during an audit that users were able to use the same passwords the day after a password change policy took effect. The following settings are in place: Users must change their passwords every 30 days. Users cannot reuse the last 10 passwords. Which of the following settings would prevent users from being able to immediately reuse the same passwords?
(Multiple Choice)
4.9/5 (79)
(79) The SSID broadcast for a wireless router has been disabled but a network administrator notices that unauthorized users are accessing the wireless network. The administer has determined that attackers are still able to detect the presence of the wireless network despite the fact the SSID has been disabled. Which of the following would further obscure the presence of the wireless network?
(Multiple Choice)
4.9/5 (67)
(67) A datacenter engineer wants to ensure an organization's servers have high speed and high redundancy and can sustain the loss of two physical disks in an array. Which of the following RAID configurations should the engineer implement to deliver this functionality?
(Multiple Choice)
4.7/5 (79)
(79) A security engineer is configuring a system that requires the X.509 certificate information to be pasted into a form field in Base64 encoded format to import it into the system. Which of the following certificate formats should the engineer use to obtain the information in the required format?
(Multiple Choice)
4.8/5 (83)
(83) Which of the following are MOST susceptible to birthday attacks?
(Multiple Choice)
4.8/5 (84)
(84) A first responder needs to collect digital evidence from a compromised headless virtual host. Which of the following should the first responder collect FIRST?
(Multiple Choice)
4.9/5 (85)
(85) An administrator is configuring access to information located on a network file server named "Bowman". The files are located in a folder named "BalkFiles". The files are only for use by the "Matthews" division and should be read-only. The security policy requires permissions for shares to be managed at the file system layer and also requires those permissions to be set according to a least privilege model. Security policy for this data type also dictates that administrator-level accounts on the system have full access to the files. The administrator configures the file share according to the following table: 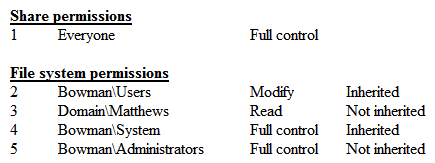 Which of the following rows has been misconfigured?
 (Multiple Choice)
4.9/5 (86)
(86) An attachment that was emailed to finance employees contained an embedded message. The security administrator investigates and finds the intent was to conceal the embedded information from public view. Which of the following BEST describes this type of message?
(Multiple Choice)
4.8/5 (72)
(72) A cybersecurity analyst is looking into the payload of a random packet capture file that was selected for analysis. The analyst notices that an internal host had a socket established with another internal host over a non-standard port. Upon investigation, the origin host that initiated the socket shows this output: 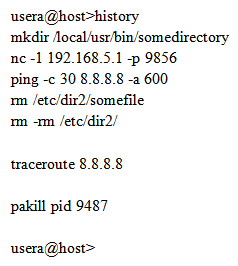 Given the above output, which of the following commands would have established the questionable socket?
 (Multiple Choice)
4.8/5 (85)
(85) Which of the following scenarios BEST describes an implementation of non-repudiation?
(Multiple Choice)
4.9/5 (84)
(84) A technician is required to configure updates on a guest operating system while maintaining the ability to quickly revert the changes that were made while testing the updates. Which of the following should the technician implement?
(Multiple Choice)
4.8/5 (82)
(82) A botnet has hit a popular website with a massive number of GRE-encapsulated packets to perform a DDoS attack. News outlets discover a certain type of refrigerator was exploited and used to send outbound packets to the website that crashed. To which of the following categories does the refrigerator belong?
(Multiple Choice)
4.9/5 (79)
(79) A network administrator is attempting to troubleshoot an issue regarding certificates on a secure website. During the troubleshooting process, the network administrator notices that the web gateway proxy on the local network has signed all of the certificates on the local machine. Which of the following describes the type of attack the proxy has been legitimately programmed to perform?
(Multiple Choice)
4.8/5 (84)
(84) Showing 401 - 420 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)