



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


When generating a request for a new x.509 certificate for securing a website, which of the following is the MOST appropriate hashing algorithm?
(Multiple Choice)
4.9/5  (75)
(75) Joe, an employee, wants to show his colleagues how much he knows about smartphones. Joe demonstrates a free movie application that he installed from a third party on his corporate smartphone. Joe's colleagues were unable to find the application in the app stores. Which of the following allowed Joe to install the application? (Choose two.)
(Multiple Choice)
4.8/5 (69)
(69) An auditor is reviewing the following output from a password-cracking tool: 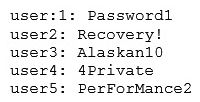 Which of the following methods did the author MOST likely use?
 (Multiple Choice)
4.8/5 (80)
(80) A security analyst is reviewing the following packet capture of an attack directed at a company's server located in the DMZ: 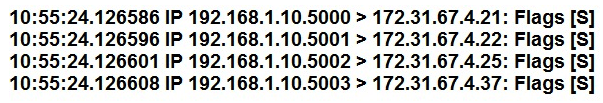 Which of the following ACLs provides the BEST protection against the above attack and any further attacks from the same IP, while minimizing service interruption?
 (Multiple Choice)
4.8/5 (90)
(90) Which of the following controls is implemented in lieu of the primary security controls?
(Multiple Choice)
4.9/5 (86)
(86) An attacker is attempting to harvest user credentials on a client's website. A security analyst notices multiple attempts of random usernames and passwords. When the analyst types in a random username and password, the logon screen displays the following message:  Which of the following should the analyst recommend be enabled?
 (Multiple Choice)
4.8/5 (73)
(73) An auditor wants to test the security posture of an organization by running a tool that will display the following: 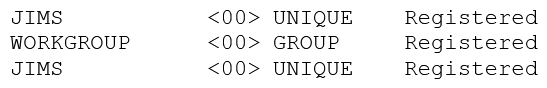 Which of the following commands should be used?
 (Multiple Choice)
4.8/5 (77)
(77) A company is deploying a file-sharing protocol access a network and needs to select a protocol for authenticating clients. Management requests that the service be configured in the most secure way possible. The protocol must also be capable of mutual authentication, and support SSO and smart card logons. Which of the following would BEST accomplish this task?
(Multiple Choice)
4.9/5 (84)
(84) A security administrator must implement a system to ensure that invalid certificates are not used by a custom developed application. The system must be able to check the validity of certificates even when internet access is unavailable. Which of the following MUST be implemented to support this requirement?
(Multiple Choice)
4.7/5 (95)
(95) An incident response analyst at a large corporation is reviewing proxy log data. The analyst believes a malware infection may have occurred. Upon further review, the analyst determines the computer responsible for the suspicious network traffic is used by the Chief Executive Officer (CEO). Which of the following is the best NEXT step for the analyst to take?
(Multiple Choice)
4.8/5 (83)
(83) While testing a new application, a developer discovers that the inclusion of an apostrophe in a username causes the application to crash. Which of the following secure coding techniques would be MOST useful to avoid this problem?
(Multiple Choice)
5.0/5 (80)
(80) A new security administrator ran a vulnerability scanner for the first time and caused a system outage. Which of the following types of scans MOST likely caused the outage?
(Multiple Choice)
4.9/5 (73)
(73) Which of the following would provide additional security by adding another factor to a smart card?
(Multiple Choice)
4.7/5 (73)
(73) A new mobile application is being developed in-house. Security reviews did not pick up any major flaws, however vulnerability scanning results show fundamental issues at the very end of the project cycle. Which of the following security activities should also have been performed to discover vulnerabilities earlier in the lifecycle?
(Multiple Choice)
4.8/5 (82)
(82) An organization is moving its human resources system to a cloud services provider. The company plans to continue using internal usernames and passwords with the service provider, but the security manager does not want the service provider to have a company of the passwords. Which of the following options meets all of these requirements?
(Multiple Choice)
4.9/5 (91)
(91) Multiple organizations operating in the same vertical wants to provide seamless wireless access for their employees as they visit the other organizations. Which of the following should be implemented if all the organizations use the native 802.1x client on their mobile devices?
(Multiple Choice)
5.0/5 (84)
(84) A security analyst has been asked to perform a review of an organization's software development lifecycle. The analyst reports that the lifecycle does not contain a phase in which team members evaluate and provide critical feedback of another developer's code. Which of the following assessment techniques is BEST described in the analyst's report?
(Multiple Choice)
4.9/5 (87)
(87) A wireless network has the following design requirements: Authentication must not be dependent on enterprise directory service It must allow background reconnection for mobile users It must not depend on user certificates Which of the following should be used in the design to meet the requirements? (Choose two.)
(Multiple Choice)
4.8/5 (72)
(72) A security administrator needs an external vendor to correct an urgent issue with an organization's physical access control system (PACS). The PACS does not currently have internet access because it is running a legacy operation system. Which of the following methods should the security administrator select the best balances security and efficiency?
(Multiple Choice)
4.8/5 (94)
(94) Showing 801 - 820 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)