



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A security administrator returning from a short vacation receives an account lock-out message when attempting to log into the computer. After getting the account unlocked the security administrator immediately notices a large amount of emails alerts pertaining to several different user accounts being locked out during the past three days. The security administrator uses system logs to determine that the lock-outs were due to a brute force attack on all accounts that has been previously logged into that machine. Which of the following can be implemented to reduce the likelihood of this attack going undetected?
(Multiple Choice)
4.7/5  (92)
(92) An organization wishes to provide better security for its name resolution services. Which of the following technologies BEST supports the deployment of DNSSEC at the organization?
(Multiple Choice)
5.0/5 (85)
(85) A vice president at a manufacturing organization is concerned about desktops being connected to the network. Employees need to log onto the desktops' local account to verify that a product is being created within specifications; otherwise, the desktops should be as isolated as possible. Which of the following is the BEST way to accomplish this?
(Multiple Choice)
4.9/5 (86)
(86) Which of the following can occur when a scanning tool cannot authenticate to a server and has to rely on limited information obtained from service banners?
(Multiple Choice)
4.9/5 (67)
(67) When attackers use a compromised host as a platform for launching attacks deeper into a company's network, it is said that they are:
(Multiple Choice)
4.8/5 (65)
(65) A security analyst is reviewing patches on servers. One of the servers is reporting the following error message in the WSUS management console: The computer has not reported status in 30 days. Given this scenario, which of the following statements BEST represents the issue with the output above?
(Multiple Choice)
4.9/5 (90)
(90) An information security analyst needs to work with an employee who can answer questions about how data for a specific system is used in the business. The analyst should seek out an employee who has the role of:
(Multiple Choice)
5.0/5 (88)
(88) A company is deploying a wireless network. It is a requirement that client devices must use X.509 certifications to mutually authenticate before connecting to the wireless network. Which of the following protocols would be required to accomplish this?
(Multiple Choice)
4.8/5 (85)
(85) A Chief Information Security Officer (CISO) for a school district wants to enable SSL to protect all of the public-facing servers in the domain. Which of the following is a secure solution that is the MOST cost effective?
(Multiple Choice)
4.7/5 (75)
(75) A company has purchased a new SaaS application and is in the process of configuring it to meet the company's needs. The director of security has requested that the SaaS application be integrated into the company's IAM processes. Which of the following configurations should the security administrator set up in order to complete this request?
(Multiple Choice)
5.0/5 (77)
(77) A Chief Executive Officer (CEO) suspects someone in the lab testing environment is stealing confidential information after working hours when no one else is around. Which of the following actions can help to prevent this specific threat?
(Multiple Choice)
4.9/5 (72)
(72) A company would like to transition its directory service from an OpenLDAP solution to Active Directory. The main goal for this project is security. All authentications to the domain controllers must be as secure as possible. Which of the following should the company use to achieve this goal?
(Multiple Choice)
4.7/5 (78)
(78) When systems, hardware, or software are not supported by the original vendor, it is a vulnerability known as:
(Multiple Choice)
4.9/5 (85)
(85) Phishing emails frequently take advantage of high-profile catastrophes reported in the news. Which of the following principles BEST describes the weakness being exploited?
(Multiple Choice)
4.9/5 (91)
(91) A system administrator is configuring a site-to-site VPN tunnel. Which of the following should be configured on the VPN concentrator during the IKE phase?
(Multiple Choice)
4.9/5 (68)
(68) Upon learning about a user who has reused the same password for the past several years, a security specialist reviews the logs. The following is an extraction of the report after the most recent password change requirement: 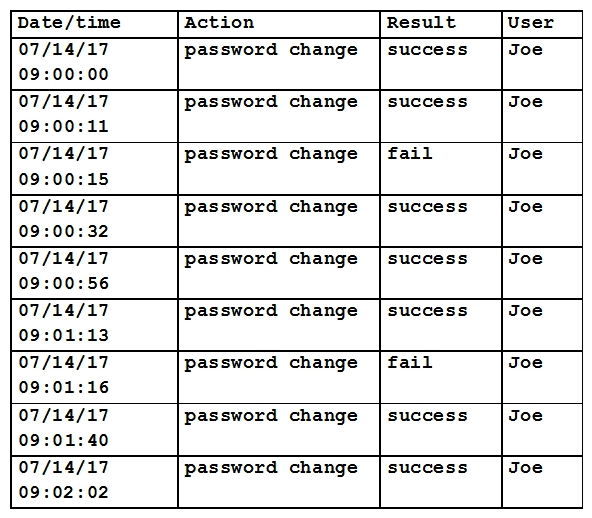 Which of the following security controls is the user's behavior targeting?
 (Multiple Choice)
4.7/5 (72)
(72) A security engineer implements multiple technical measures to secure an enterprise network. The engineer also works with the Chief Information Officer (CIO) to implement policies to govern user behavior. Which of the following strategies is the security engineer executing?
(Multiple Choice)
4.8/5 (79)
(79) Which of the following types of keys is found in a key escrow?
(Multiple Choice)
4.8/5 (86)
(86) A Chief Information Officer (CIO) wants to eliminate the number of calls the help desk is receiving for password resets when users log on to internal portals. Which of the following is the BEST solution?
(Multiple Choice)
4.8/5 (90)
(90) Which of the following types of security testing is the MOST cost-effective approach used to analyze existing code and identity areas that require patching?
(Multiple Choice)
4.8/5 (79)
(79) Showing 721 - 740 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)