



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An attack that is using interference as its main attack to impede network traffic is which of the following?
(Multiple Choice)
4.9/5  (80)
(80) Many employees are receiving email messages similar to the one shown below: From IT department To employee Subject email quota exceeded Pease click on the following link http:www.website.info/email.php?quota=1Gb and provide your username and password to increase your email quota. Upon reviewing other similar emails, the security administrator realized that all the phishing URLs have the following common elements; they all use HTTP, they all come from .info domains, and they all contain the same URI. Which of the following should the security administrator configure on the corporate content filter to prevent users from accessing the phishing URL, while at the same time minimizing false positives?
(Multiple Choice)
4.9/5 (76)
(76) Which of the following must be intact for evidence to be admissible in court?
(Multiple Choice)
4.7/5 (85)
(85) A security administrator is investigating a possible account compromise. The administrator logs onto a desktop computer, executes the command notepad.exe c:\Temp\qkakforlkgfkja.1og , and reviews the following: Lee,\rI have completed the task that was assigned to me\rrespectfully\rJohn\r https://www.portal.com \rjohnuser\rilovemycat2 Given the above output, which of the following is the MOST likely cause of this compromise?
(Multiple Choice)
4.7/5 (90)
(90) Which of the following is the MAIN disadvantage of using SSO?
(Multiple Choice)
4.9/5 (80)
(80) A technician wants to configure a wireless router at a small office that manages a family-owned dry cleaning business. The router will support five laptops, personal smartphones, a wireless printer, and occasional guests. Which of the following wireless configurations is BEST implemented in this scenario?
(Multiple Choice)
4.9/5 (84)
(84) An organization is working with a cloud services provider to transition critical business applications to a hybrid cloud environment. The organization retains sensitive customer data and wants to ensure the provider has sufficient administrative and logical controls in place to protect its data. In which of the following documents would this concern MOST likely be addressed?
(Multiple Choice)
5.0/5 (77)
(77) Joe, an employee, wants to show his colleagues how much he knows about smartphones. Joe demonstrates a free movie application that he installed from a third party on his corporate smartphone. Joe's colleagues were unable to find the application in the app stores. Which of the following allowed Joe to install the application? (Select two.)
(Multiple Choice)
4.9/5 (95)
(95) After discovering the /etc/shadow file had been rewritten, a security administrator noticed an application insecurely creating files in / tmp . Which of the following vulnerabilities has MOST likely been exploited?
(Multiple Choice)
4.9/5 (84)
(84) A security administrator wants to implement a company-wide policy to empower data owners to manage and enforce access control rules on various resources. Which of the following should be implemented?
(Multiple Choice)
5.0/5 (69)
(69) A Chief Executive Officer (CEO) is staying at a hotel during a business trip. The hotel's wireless network does not show a lock symbol. Which of the following precautions should the CEO take? (Choose two.)
(Multiple Choice)
4.8/5 (81)
(81) A security administrator has found a hash in the environment known to belong to malware. The administrator then finds this file to be in in the preupdate area of the OS, which indicates it was pushed from the central patch system. File: winx86_adobe_flash_upgrade.exe Hash: 99ac28bede43ab869b853ba62c4ea243 The administrator pulls a report from the patch management system with the following output:  Given the above outputs, which of the following MOST likely happened?
 (Multiple Choice)
4.9/5 (91)
(91) A security administrator is analyzing a user report in which the computer exhibits odd network-related outages. The administrator, however, does not see any suspicious processes running. A prior technician's notes indicate the machine has been remediated twice, but the system still exhibits odd behavior. Files were deleted from the system recently. Which of the following is the MOST likely cause of this behavior?
(Multiple Choice)
4.9/5 (88)
(88) Two users need to send each other emails over unsecured channels. The system should support the principle of non-repudiation. Which of the following should be used to sign the user's certificates?
(Multiple Choice)
4.9/5 (74)
(74) A systems administrator is attempting to recover from a catastrophic failure in the datacenter. To recover the domain controller, the systems administrator needs to provide the domain administrator credentials. Which of the following account types is the systems administrator using?
(Multiple Choice)
4.7/5 (79)
(79) A datacenter manager has been asked to prioritize critical system recovery priorities. Which of the following is the MOST critical for immediate recovery?
(Multiple Choice)
4.8/5 (82)
(82) A company is having issues with intellectual property being sent to a competitor from its system. The information being sent is not random but has an identifiable pattern. Which of the following should be implemented in the system to stop the content from being sent?
(Multiple Choice)
4.8/5 (67)
(67) A security technician has been assigned data destruction duties. The hard drives that are being disposed of contain highly sensitive information. Which of the following data destruction techniques is MOST appropriate?
(Multiple Choice)
4.7/5 (88)
(88) A technician has discovered a crypto-virus infection on a workstation that has access to sensitive remote resources. Which of the following is the immediate NEXT step the technician should take?
(Multiple Choice)
4.8/5 (79)
(79) A network administrator was provided the following output from a vulnerability scan: 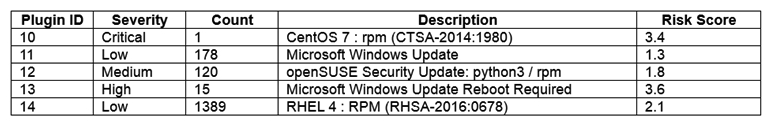 The network administrator has been instructed to prioritize remediation efforts based on overall risk to the enterprise. Which of the following plugin IDs should be remediated FIRST?
 (Multiple Choice)
4.9/5 (69)
(69) Showing 701 - 720 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)