



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


Which of the following identity access methods creates a cookie on the first login to a central authority to allow logins to subsequent applications without re-entering credentials?
(Multiple Choice)
4.8/5  (86)
(86) A system's administrator has finished configuring firewall ACL to allow access to a new web answer. 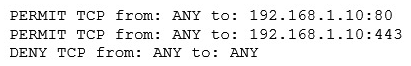 The security administrator confirms form the following packet capture that there is network traffic from the internet to the web server:
 The company's internal auditor issues a security finding and requests that immediate action be taken. With which of the following is the auditor MOST concerned?
The security administrator confirms form the following packet capture that there is network traffic from the internet to the web server: The company's internal auditor issues a security finding and requests that immediate action be taken. With which of the following is the auditor MOST concerned? (Multiple Choice)
4.9/5 (79)
(79) Which of the following methods minimizes the system interaction when gathering information to conduct a vulnerability assessment of a router?
(Multiple Choice)
4.9/5 (78)
(78) A security analyst needs to be proactive in understanding the types of attacks that could potentially target the company's executives. Which of the following intelligence sources should the security analyst review?
(Multiple Choice)
4.9/5 (90)
(90) Which of the following characteristics differentiate a rainbow table attack from a brute force attack? (Select two.)
(Multiple Choice)
4.9/5 (76)
(76) A web application is configured to target browsers and allow access to bank accounts to siphon money to a foreign account. This is an example of which of the following attacks?
(Multiple Choice)
4.8/5 (82)
(82) An external auditor visits the human resources department and performs a physical security assessment. The auditor observed documents on printers that are unclaimed. A closer look at these documents reveals employee names, addresses, ages, and types of medical and dental coverage options each employee has selected. Which of the following is the MOST appropriate actions to take?
(Multiple Choice)
4.8/5 (72)
(72) Which of the following is a document that contains detailed information about actions that include how something will be done, when the actions will be performed, and penalties for failure?
(Multiple Choice)
4.8/5 (70)
(70) A company is planning to utilize its legacy desktop systems by converting them into dummy terminals and moving all heavy applications and storage to a centralized server that hosts all of the company's required desktop applications. Which of the following describes the BEST deployment method to meet these requirements?
(Multiple Choice)
4.9/5 (74)
(74) The firewall administrator is adding a new certificate for the company's remote access solution. The solution requires that the uploaded file contain the entire certificate chain for the certificate to load properly. The administrator loads the company certificate and the root CA certificate into the file. The file upload is rejected. Which of the following is required to complete the certificate chain?
(Multiple Choice)
4.9/5 (87)
(87) A security engineer is configuring a wireless network that must support mutual authentication of the wireless client and the authentication server before users provide credentials. The wireless network must also support authentication with usernames and passwords. Which of the following authentication protocols MUST the security engineer select?
(Multiple Choice)
4.7/5 (79)
(79) An organization is comparing and contrasting migration from its standard desktop configuration to the newest version of the platform. Before this can happen, the Chief Information Security Officer (CISO) voices the need to evaluate the functionality of the newer desktop platform to ensure interoperability with existing software in use by the organization. In which of the following principles of architecture and design is the CISO engaging?
(Multiple Choice)
4.8/5 (77)
(77) Using a one-time code that has been texted to a smartphone is an example of:
(Multiple Choice)
4.9/5 (89)
(89) A Chief Security Office's (CSO's) key priorities are to improve preparation, response, and recovery practices to minimize system downtime and enhance organizational resilience to ransomware attacks. Which of the following would BEST meet the CSO's objectives?
(Multiple Choice)
4.9/5 (59)
(59) A group of developers is collaborating to write software for a company. The developers need to work in subgroups and control who has access to their modules. Which of the following access control methods is considered user-centric?
(Multiple Choice)
4.8/5 (62)
(62) A computer on a company network was infected with a zero-day exploit after an employee accidently opened an email that contained malicious content. The employee recognized the email as malicious and was attempting to delete it, but accidently opened it. Which of the following should be done to prevent this scenario from occurring again in the future?
(Multiple Choice)
4.9/5 (70)
(70) An employee receives an email, which appears to be from the Chief Executive Officer (CEO), asking for a report of security credentials for all users. Which of the following types of attack is MOST likely occurring?
(Multiple Choice)
5.0/5 (78)
(78) A security team wants to establish an Incident Response plan. The team has never experienced an incident. Which of the following would BEST help them establish plans and procedures?
(Multiple Choice)
4.8/5 (80)
(80) A threat actor motivated by political goals that is active for a short period of time but has virtually unlimited resources is BEST categorized as a:
(Multiple Choice)
4.8/5 (88)
(88) Which of the following is the proper use of a Faraday cage?
(Multiple Choice)
4.8/5 (65)
(65) Showing 61 - 80 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)