



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An analyst is reviewing the following web-server log after receiving an alert from the DLP system about multiple PII records being transmitted in cleartext: 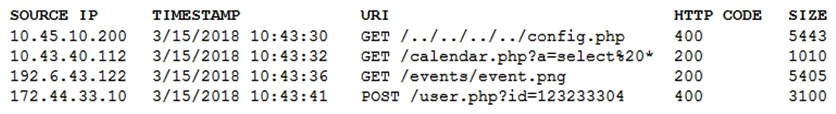 Which of the following IP addresses is MOST likely involved in the data leakage attempt?
 (Multiple Choice)
4.9/5  (74)
(74) A company is implementing a tool to mask all PII when moving data from a production server to a testing server. Which of the following security techniques is the company applying?
(Multiple Choice)
4.9/5 (71)
(71) Which of the following technologies employ the use of SAML? (Choose two.)
(Multiple Choice)
4.8/5 (72)
(72) The application team within a company is asking the security team to investigate why its application is slow after an upgrade. The source of the team's application is 10.13.136.9, and the destination IP is 10.17.36.5. The security analyst pulls the logs from the endpoint security software but sees nothing is being blocked. The analyst then looks at the UTM firewall logs and sees the following: 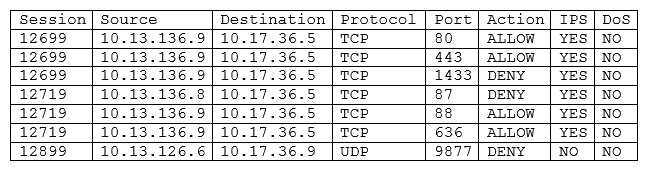 Which of the following should the security analyst request NEXT based on the UTM firewall analysis?
 (Multiple Choice)
4.8/5 (78)
(78) In which of the following ways does phishing and smishing differ?
(Multiple Choice)
4.7/5 (83)
(83) A security analyst needs to generate a server certificate to be used for 802.1X and secure RDP connections. The analyst is unsure what is required to perform the task and solicits help from a senior colleague. Which of the following is the FIRST step the senior colleague will most likely tell the analyst to perform to accomplish this task?
(Multiple Choice)
4.9/5 (82)
(82) In highly secure environments where the risk of malicious actors attempting to steal data is high, which of the following is the BEST reason to deploy Faraday cages?
(Multiple Choice)
4.9/5 (85)
(85) A systems administrator found a suspicious file in the root of the file system. The file contains URLs, usernames, passwords, and text from other documents being edited on the system. Which of the following types of malware would generate such a file?
(Multiple Choice)
4.9/5 (79)
(79) A company has a data classification system with definitions for "Private" and "Public". The company's security policy outlines how data should be protected based on type. The company recently added the data type "Proprietary". Which of the following is the MOST likely reason the company added this data type?
(Multiple Choice)
4.8/5 (76)
(76) A company wants to ensure users are only logging into the system from their laptops when they are on site. Which of the following would assist with this?
(Multiple Choice)
4.8/5 (73)
(73) A recent audit uncovered a key finding regarding the use of a specific encryption standard in a web application that is used to communicate with business customers. Due to the technical limitations of its customers, the company is unable to upgrade the encryption standard. Which of the following types of controls should be used to reduce the risk created by this scenario?
(Multiple Choice)
4.9/5 (80)
(80) An organization plans to implement multifactor authentication techniques within the enterprise network architecture. Each authentication factor is expected to be a unique control. Which of the following BEST describes the proper employment of multifactor authentication?
(Multiple Choice)
4.9/5 (78)
(78) A company wants to host a publicity available server that performs the following functions: Evaluates MX record lookup Can perform authenticated requests for A and AAA records Uses RRSIG Which of the following should the company use to fulfill the above requirements?
(Multiple Choice)
4.9/5 (79)
(79) A user clicked an email link that led to a website than infected the workstation with a virus. The virus encrypted all the network shares to which the user had access. The virus was not deleted or blocked by the company's email filter, website filter, or antivirus. Which of the following describes what occurred?
(Multiple Choice)
4.8/5 (95)
(95) A water utility company has seen a dramatic increase in the number of water pumps burning out. A malicious actor was attacking the company and is responsible for the increase. Which of the following systems has the attacker compromised?
(Multiple Choice)
4.9/5 (74)
(74) Which of the following BEST describes the concept of perfect forward secrecy?
(Multiple Choice)
4.9/5 (87)
(87) While checking logs, a security engineer notices a number of end users suddenly downloading files with the .tar.gz extension. Closer examination of the files reveals they are PE32 files. The end users state they did not initiate any of the downloads. Further investigation reveals the end users all clicked on an external email containing an infected MHT file with an href link a week prior. Which of the following is MOST likely occurring?
(Multiple Choice)
4.8/5 (67)
(67) A company recently experienced data exfiltration via the corporate network. In response to the breach, a security analyst recommends deploying an out-of-band IDS solution. The analyst says the solution can be implemented without purchasing any additional network hardware. Which of the following solutions will be used to deploy the IDS?
(Multiple Choice)
4.9/5 (84)
(84) Six months into development, the core team assigned to implement a new internal piece of software must convene to discuss a new requirement with the stake holders. A stakeholder identified a missing feature critical to the organization, which must be implemented. The team needs to validate the feasibility of the newly introduced requirement and ensure it does not introduce new vulnerabilities to the software and other applications that will integrate with it. Which of the following BEST describes what the company?
(Multiple Choice)
4.8/5 (82)
(82) Which of the following BEST explains how the use of configuration templates reduces organization risk?
(Multiple Choice)
4.8/5 (85)
(85) Showing 281 - 300 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)