



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A systems administrator wants to enforce the use of HTTPS on a new website. Which of the following should the systems administrator do NEXT after generating the CSR?
(Multiple Choice)
4.8/5  (75)
(75) A security analyst is testing both Windows and Linux systems for unauthorized DNS zone transfers within a LAN on comptia.org from example.org. Which of the following commands should the security analyst use? (Choose two.)
(Multiple Choice)
4.8/5 (85)
(85) A local coffee shop runs a small WiFi hotspot for its customers that utilizes WPA2-PSK. The coffee shop would like to stay current with security trends and wants to implement WPA3 to make its WiFi even more secure. Which of the following technologies should the coffee shop use in place of PSK?
(Multiple Choice)
4.7/5 (86)
(86) A user suspects someone has been accessing a home network without permission by spoofing the MAC address of an authorized system. While attempting to determine if an authorized user is logged into the home network, the user reviews the wireless router, which shows the following table for systems that are currently on the home network. 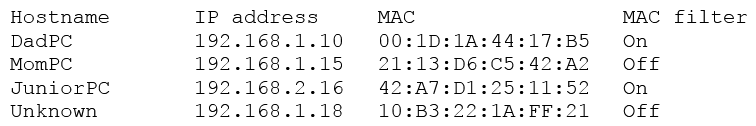 Which of the following should be the NEXT step to determine if there is an unauthorized user on the network?
 (Multiple Choice)
4.7/5 (79)
(79) Joe, a contractor, is hired by a firm to perform a penetration test against the firm's infrastructure. When conducting the scan, he receives only the network diagram and the network list to scan against the network. Which of the following scan types is Joe performing?
(Multiple Choice)
4.7/5 (69)
(69) A security analyst is implementing PKI-based functionality to a web application that has the following requirements: File contains certificate information Certificate chains Root authority certificates Private key All of these components will be part of one file and cryptographically protected with a password. Given this scenario, which of the following certificate types should the analyst implement to BEST meet these requirements?
(Multiple Choice)
4.8/5 (67)
(67) A company recently experienced a security breach. The security staff determined that the intrusion was due to an out-of-date proprietary software program running on a non-compliant server. The server was imaged and copied onto a hardened VM, with the previous connections re-established. Which of the following is the NEXT step in the incident response process?
(Multiple Choice)
4.9/5 (74)
(74) Joe, an employee, asks a coworker how long ago Ann started working at the help desk. The coworker expresses surprise since nobody named Ann works at the help desk. Joe mentions that Ann called several people in the customer service department to help reset their passwords over the phone due to unspecified "server issues". Which of the following has occurred?
(Multiple Choice)
4.9/5 (82)
(82) A systems engineer is configuring a wireless network. The network must not require installation of third-party software. Mutual authentication of the client and the server must be used. The company has an internal PKI. Which of the following configurations should the engineer choose?
(Multiple Choice)
4.7/5 (64)
(64) A manager makes an unannounced visit to the marketing department and performs a walk-through of the office. The manager observes unclaimed documents on printers. A closer look at these documents reveals employee names, addresses, ages, birth dates, marital/dependent statuses, and favorite ice cream flavors. The manager brings this to the attention of the marketing department head. The manager believes this information to be PII, but the marketing head does not agree. Having reached a stalemate, which of the following is the MOST appropriate action to take NEXT?
(Multiple Choice)
4.9/5 (70)
(70) An organization would like to set up a more robust network access system. The network administrator suggests the organization move to a certificate-based authentication setup in which a client-side certificate is used while connecting. Which of the following EAP types should be used to meet these criteria?
(Multiple Choice)
4.9/5 (86)
(86) A security analyst conducts a manual scan on a known hardened host that identifies many non-compliant configuration items. Which of the following BEST describe why this has occurred? (Choose two.)
(Multiple Choice)
5.0/5 (81)
(81) A technician is designing a solution that will be required to process sensitive information, including classified government data. The system needs to be common criteria certified. Which of the following should the technician select?
(Multiple Choice)
4.9/5 (86)
(86) The chief security officer (CS0) has issued a new policy that requires that all internal websites be configured for HTTPS traffic only. The network administrator has been tasked to update all internal sites without incurring additional costs. Which of the following is the best solution for the network administrator to secure each internal website?
(Multiple Choice)
5.0/5 (84)
(84) While reviewing the security controls in place for a web-based application, a security controls assessor notices that there are no password strength requirements in place. Because of this vulnerability, passwords might be easily discovered using a brute force attack. Which of the following password requirements will MOST effectively improve the security posture of the application against these attacks? (Select two)
(Multiple Choice)
4.8/5 (84)
(84) A security administrator has been asked to implement a VPN that will support remote access over IPSEC. Which of the following is an encryption algorithm that would meet this requirement?
(Multiple Choice)
4.9/5 (79)
(79) A penetration testing is preparing for a client engagement in which the tester must provide data that proves and validates the scanning tools' results. Which of the following is the best method for collecting this information?
(Multiple Choice)
4.9/5 (71)
(71) The IT department's on-site developer has been with the team for many years. Each time an application is released, the security team is able to identify multiple vulnerabilities. Which of the following would BEST help the team ensure the application is ready to be released to production?
(Multiple Choice)
4.8/5 (77)
(77) Systems administrator and key support staff come together to simulate a hypothetical interruption of service. The team updates the disaster recovery processes and documentation after meeting. Which of the following describes the team's efforts?
(Multiple Choice)
4.9/5 (93)
(93) An organization has determined it can tolerate a maximum of three hours of downtime. Which of the following has been specified?
(Multiple Choice)
4.9/5 (82)
(82) Showing 661 - 680 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)