



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


The chief Security Officer (CSO) has reported a rise in data loss but no break ins have occurred. By doing which of the following is the CSO most likely to reduce the number of incidents?
(Multiple Choice)
4.8/5  (81)
(81) A company has critical systems that are hosted on an end-of-life OS. To maintain operations and mitigate potential vulnerabilities, which of the following BEST accomplishes this objective?
(Multiple Choice)
4.9/5 (84)
(84) A recent internal audit is forcing a company to review each internal business unit's VMs because the cluster they are installed on is in danger of running out of computer resources. Which of the following vulnerabilities exists?
(Multiple Choice)
4.8/5 (93)
(93) Which of the following types of attack is being used when an attacker responds by sending the MAC address of the attacking machine to resolve the MAC to IP address of a valid server?
(Multiple Choice)
4.9/5 (79)
(79) A critical enterprise component whose loss or destruction would significantly impede business operations or have an outsized impact on corporate revenue is known as:
(Multiple Choice)
4.8/5 (95)
(95) A remote intruder wants to take inventory of a network so exploits can be researched. The intruder is looking for information about software versions on the network. Which of the following techniques is the intruder using?
(Multiple Choice)
4.9/5 (73)
(73) Which of the following BEST explains "likelihood of occurrence"?
(Multiple Choice)
4.9/5 (78)
(78) Ann, a security administrator, wants to ensure credentials are encrypted in transit when implementing a RADIUS server for SSO. Which of the following are needed given these requirements? (Choose two.)
(Multiple Choice)
4.8/5 (79)
(79) Which of the following cloud models is used to share resources and information with business partners and like businesses without allowing everyone else access?
(Multiple Choice)
4.7/5 (92)
(92) Given the information below: MD5HASH document.doc 049eab40fd36caadlfab10b3cdf4a883 MD5HASH image. jpg 049eab40fd36caadlfab10b3cdf4a883 Which of the following concepts are described above? (Choose two.)
(Multiple Choice)
4.9/5 (84)
(84) A hospital has received reports from multiple patients that their PHI was stolen after completing forms on the hospital's website. Upon investigation, the hospital finds a packet analyzer was used to steal data. Which of the following protocols would prevent this attack from reoccurring?
(Multiple Choice)
4.8/5 (72)
(72) After a merger, it was determined that several individuals could perform the tasks of a network administrator in the merged organization. Which of the following should have been performed to ensure that employees have proper access?
(Multiple Choice)
4.7/5 (83)
(83) An organization is drafting an IRP and needs to determine which employees have the authority to take systems offline during an emergency situation. Which of the following is being outlined?
(Multiple Choice)
4.9/5 (76)
(76) A company wants to implement an access management solution that allows employees to use the same usernames and passwords for multiple applications without having to keep multiple credentials synchronized. Which of the following solutions would BEST meet these requirements?
(Multiple Choice)
4.8/5 (94)
(94) A security administrator wishes to implement a secure a method of file transfer when communicating with outside organizations. Which of the following protocols would BEST facilitate secure file transfers? (Select TWO)
(Multiple Choice)
4.9/5 (79)
(79) An organization's policy requires users to create passwords with an uppercase letter, lowercase letter, number, and symbol. This policy is enforced with technical controls, which also prevents users from using any of their previous 12 passwords. The quantization does not use single sign-on, nor does it centralize storage of passwords. The incident response team recently discovered that passwords for one system were compromised. Passwords for a completely separate system have NOT been compromised, but unusual login activity has been detected for that separate system. Account login has been detected for users who are on vacation. Which of the following BEST describes what is happening?
(Multiple Choice)
5.0/5 (82)
(82) A systems administrator needs to integrate multiple IoT and small embedded devices into the company's wireless network securely. Which of the following should the administrator implement to ensure low-power and legacy devices can connect to the wireless network?
(Multiple Choice)
4.8/5 (89)
(89) A corporation is concerned that, if a mobile device is lost, any sensitive information on the device could be accessed by third parties. Which of the following would BEST prevent this from happening?
(Multiple Choice)
4.9/5 (74)
(74) A security administrator receives alerts from the perimeter UTM. Upon checking the logs, the administrator finds the following output: Time: 12/25 0300 From Zone: Untrust To Zone: DMZ Attacker: externalip.com Victim: 172.16.0.20 To Port: 80 Action: Alert Severity: Critical When examining the PCAP associated with the event, the security administrator finds the following information: <script> alert ("Click here for important information regarding your account! http://externalip.com/account.php "); </script> Which of the following actions should the security administrator take?
(Multiple Choice)
4.9/5 (82)
(82) An organization requires secure configuration baselines for all platforms and technologies that are used. If any system cannot conform to the secure baseline, the organization must process a risk acceptance and receive approval before the system is placed into production. It may have non-conforming systems in its lower environments (development and staging) without risk acceptance, but must receive risk approval before the system is placed in production. Weekly scan reports identify systems that do not conform to any secure baseline. The application team receives a report with the following results: 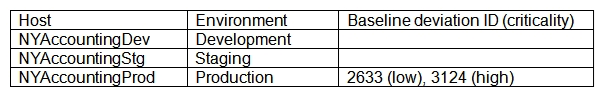 There are currently no risk acceptances for baseline deviations. This is a mission-critical application, and the organization cannot operate if the application is not running. The application fully functions in the development and staging environments. Which of the following actions should the application team take?
 (Multiple Choice)
4.9/5 (73)
(73) Showing 981 - 1000 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)