



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A CSIRT has completed restoration procedures related to a breach of sensitive data is creating documentation used to improve the organization's security posture. The team has been specifically tasked to address logical controls in their suggestions. Which of the following would be MOST beneficial to include in lessons learned documentation? (Choose two.)
(Multiple Choice)
4.9/5  (69)
(69) Which of the following precautions MINIMIZES the risk from network attacks directed at multifunction printers, as well as the impact on functionality at the same time?
(Multiple Choice)
4.8/5 (68)
(68) During a recent audit, it was discovered that several user accounts belonging to former employees were still active and had valid VPN permissions. Which of the following would help reduce the amount of risk the organization incurs in this situation in the future?
(Multiple Choice)
4.9/5 (84)
(84) An intruder sniffs network traffic and captures a packet of internal network transactions that add funds to a game card. The intruder pushes the same packet multiple times across the network, which increments the funds on the game card. Which of the following should a security administrator implement to BEST protect against this type of attack?
(Multiple Choice)
4.8/5 (75)
(75) A security administrator is creating a subnet on one of the corporate firewall interfaces to use as a DMZ which is expected to accommodate at most 14 physical hosts. Which of the following subnets would BEST meet the requirements?
(Multiple Choice)
4.9/5 (67)
(67) A security analyst is hardening a server with the directory services role installed. The analyst must ensure LDAP traffic cannot be monitored or sniffed and maintains compatibility with LDAP clients. Which of the following should the analyst implement to meet these requirements? (Choose two.)
(Multiple Choice)
4.9/5 (67)
(67) A system's administrator has finished configuring firewall ACL to allow access to a new web server. 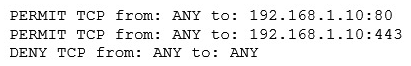 The security administrator confirms form the following packet capture that there is network traffic from the internet to the web server:
 The company's internal auditor issues a security finding and requests that immediate action be taken. With which of the following is the auditor MOST concerned?
The security administrator confirms form the following packet capture that there is network traffic from the internet to the web server: The company's internal auditor issues a security finding and requests that immediate action be taken. With which of the following is the auditor MOST concerned? (Multiple Choice)
4.9/5 (88)
(88) A network administrator wants to implement a method of securing internal routing. Which of the following should the administrator implement?
(Multiple Choice)
4.9/5 (74)
(74) A company has had a BYOD policy in place for many years and now wants to roll out an MDM solution. The company has decided that end users who wish to utilize their personal devices for corporate use must opt in to the MDM solution. End users are voicing concerns about the company having access to their personal devices via the MDM solution. Which of the following should the company implement to ease these concerns?
(Multiple Choice)
4.8/5 (76)
(76) An organization has hired a penetration tester to test the security of its ten web servers. The penetration tester is able to gain root/administrative access in several servers by exploiting vulnerabilities associated with the implementation of SMTP, POP, DNS, FTP, Telnet, and IMAP. Which of the following recommendations should the penetration tester provide to the organization to better protect their web servers in the future?
(Multiple Choice)
4.9/5 (86)
(86) A company has just experienced a malware attack affecting a large number of desktop users. The antivirus solution was not able to block the malware, but the HIDS alerted to C2 calls as 'Troj.Generic' . Once the security team found a solution to remove the malware, they were able to remove the malware files successfully, and the HIDS stopped alerting. The next morning, however, the HIDS once again started alerting on the same desktops, and the security team discovered the files were back. Which of the following BEST describes the type of malware infecting this company's network?
(Multiple Choice)
4.8/5 (90)
(90) A technician is configuring a load balancer for the application team to accelerate the network performance of their applications. The applications are hosted on multiple servers and must be redundant. Given this scenario, which of the following would be the BEST method of configuring the load balancer?
(Multiple Choice)
4.8/5 (94)
(94) When sending messages using symmetric encryption, which of the following must happen FIRST?
(Multiple Choice)
4.7/5 (70)
(70) An organization wants to upgrade its enterprise-wide desktop computer solution. The organization currently has 500 PCs active on the network. The Chief Information Security Officer (CISO) suggests that the organization employ desktop imaging technology for such a large-scale upgrade. Which of the following is a security benefit of implementing an imaging solution?
(Multiple Choice)
4.9/5 (72)
(72) Which of the following BEST describes a security exploit for which a vendor patch is not readily available?
(Multiple Choice)
4.9/5 (69)
(69) After a breach, a company has decided to implement a solution to better understand the technique used by the attackers. Which of the following is the BEST solution to be deployed?
(Multiple Choice)
4.8/5 (66)
(66) Company policy requires the use if passphrases instead if passwords. Which of the following technical controls MUST be in place in order to promote the use of passphrases?
(Multiple Choice)
5.0/5 (83)
(83) The computer resource center issued smartphones to all first-level and above managers. The managers have the ability to install mobile tools. Which of the following tools should be implemented to control the types of tools the managers install?
(Multiple Choice)
4.9/5 (71)
(71) The Chief Information Security Officer (CISO) in a company is working to maximize protection efforts of sensitive corporate data. The CISO implements a "100% shred" policy within the organization, with the intent to destroy any documentation that is not actively in use in a way that it cannot be recovered or reassembled. Which of the following attacks is this deterrent MOST likely to mitigate?
(Multiple Choice)
5.0/5 (72)
(72) Showing 561 - 580 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)