



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


After reports of slow internet connectivity, a technician reviews the following logs from a server's host-based firewall: 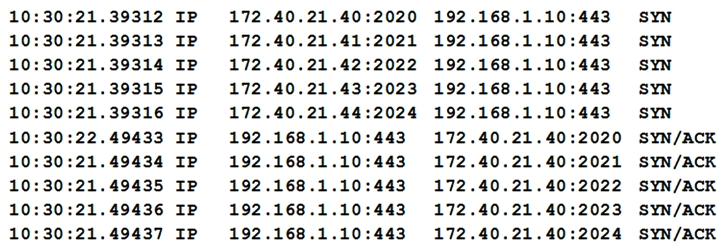 Which of the following can the technician conclude after reviewing the above logs?
 (Multiple Choice)
4.9/5  (61)
(61) A security analyst wishes to scan the network to view potentially vulnerable systems the way an attacker would. Which of the following would BEST enable the analyst to complete the objective?
(Multiple Choice)
4.8/5 (80)
(80) A security architect has convened a meeting to discuss an organization's key management policy. The organization has a reliable internal key management system, and some argue that it would be best to manage the cryptographic keys internally as opposed to using a solution from a third party. The company should use:
(Multiple Choice)
4.8/5 (93)
(93) The Chief Technology Officer (CTO) of a company, Ann, is putting together a hardware budget for the next 10 years. She is asking for the average lifespan of each hardware device so that she is able to calculate when she will have to replace each device. Which of the following categories BEST describes what she is looking for?
(Multiple Choice)
4.8/5 (72)
(72) The Chief Information Officer (CIO) has determined the company's new PKI will not use OCSP. The purpose of OCSP still needs to be addressed. Which of the following should be implemented?
(Multiple Choice)
4.9/5 (80)
(80) A systems administrator has created network file shares for each department with associated security groups for each role within the organization. Which of the following security concepts is the systems administrator implementing?
(Multiple Choice)
4.9/5 (79)
(79) An information security specialist is reviewing the following output from a Linux server. 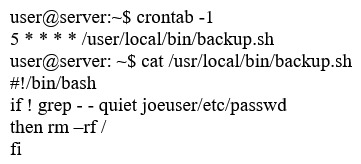 Based on the above information, which of the following types of malware was installed on the server? /local/
 (Multiple Choice)
4.9/5 (79)
(79) A security administrator in a bank is required to enforce an access control policy so no single individual is allowed to both initiate and approve financial transactions. Which of the following BEST represents the impact the administrator is deterring?
(Multiple Choice)
4.7/5 (66)
(66) An in-house penetration tester is using a packet capture device to listen in on network communications. This is an example of:
(Multiple Choice)
4.9/5 (83)
(83) A system's administrator has finished configuring firewall ACL to allow access to a new web answer. PERMIT TCP from: ANY to: 192.168.1.10:80 PERMIT TCP from: ANY to: 192.168.1.10:443 DENY TCP from: ANY to: ANY The security administrator confirms form the following packet capture that there is network traffic from the internet to the web server: TCP 10.23.243.2:2000->192.168.1.10:80 POST/default's TCP 172.16.4.100:1934->192.168.1.10:80 GET/session.aspx?user_1_sessionid= a12ad8741d8f7e7ac723847aa8231a The company's internal auditor issues a security finding and requests that immediate action be taken. With which of the following is the auditor MOST concerned?
(Multiple Choice)
4.8/5 (77)
(77) Datacenter employees have been battling alarms in a datacenter that has been experiencing hotter than normal temperatures. The server racks are designed so all 48 rack units are in use, and servers are installed in any manner in which the technician can get them installed. Which of the following practices would BEST alleviate the heat issues and keep costs low?
(Multiple Choice)
4.9/5 (74)
(74) Which of the following BEST explains how the use of configuration templates reduces organization risk?
(Multiple Choice)
4.9/5 (78)
(78) A security analyst is reviewing an assessment report that includes software versions, running services, supported encryption algorithms, and permission settings. Which of the following produced the report?
(Multiple Choice)
4.9/5 (74)
(74) An audit has revealed that database administrators are also responsible for auditing database changes and backup logs. Which of the following access control methodologies would BEST mitigate this concern?
(Multiple Choice)
4.7/5 (68)
(68) Which of the following are considered to be "something you do"? (Choose two.)
(Multiple Choice)
4.8/5 (77)
(77) Fuzzing is used to reveal which of the following vulnerabilities in web applications?
(Multiple Choice)
4.9/5 (82)
(82) Moving laterally within a network once an initial exploit is used to gain persistent access for the purpose of establishing further control of a system is known as:
(Multiple Choice)
4.7/5 (81)
(81) Which of the following command line tools would be BEST to identify the services running in a server?
(Multiple Choice)
4.7/5 (83)
(83) A security analyst is investigating a security breach. Upon inspection of the audit an access logs, the analyst notices the host was accessed and the /etc/passwd file was modified with a new entry for username "gotcha" and user ID of 0. Which of the following are the MOST likely attack vector and tool the analyst should use to determine if the attack is still ongoing? (Select TWO)
(Multiple Choice)
4.9/5 (86)
(86) A security, who is analyzing the security of the company's web server, receives the following output: 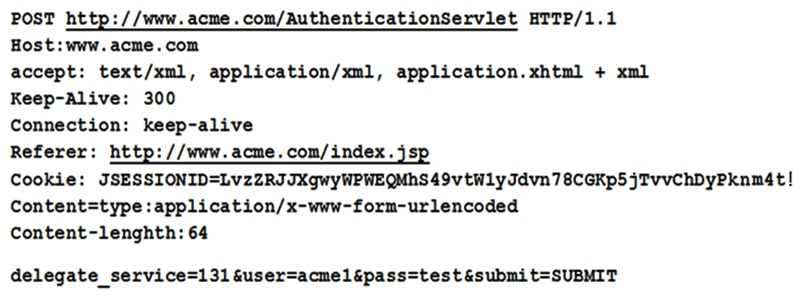 Which of the following is the issue?
 (Multiple Choice)
4.8/5 (78)
(78) Showing 1081 - 1100 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)