



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A penetration tester finds that a company's login credentials for the email client were being sent in clear text. Which of the following should be done to provide encrypted logins to the email server?
(Multiple Choice)
4.9/5  (70)
(70) Management wants to ensure any sensitive data on company-provided cell phones is isolated in a single location that can be remotely wiped if the phone is lost. Which of the following technologies BEST meets this need?
(Multiple Choice)
4.8/5 (77)
(77) Ann, a security administrator, has been instructed to perform fuzz-based testing on the company's applications. Which of the following best describes what she will do?
(Multiple Choice)
4.8/5 (89)
(89) Which of the following threat actors is MOST likely to steal a company's proprietary information to gain a market edge and reduce time to market?
(Multiple Choice)
4.8/5 (85)
(85) A user attempts to send an email to an external domain and quickly receives a bounce-back message. The user then contacts the help desk stating the message is important and needs to be delivered immediately. While digging through the email logs, a systems administrator finds the email and bounce-back details: Your email has been rejected because it appears to contain SSN information. Sending SSN information via email to external recipients violates company policy. Which of the following technologies successfully stopped the email from being sent?
(Multiple Choice)
4.8/5 (99)
(99) Which of the following would meet the requirements for multifactor authentication?
(Multiple Choice)
4.8/5 (77)
(77) An email systems administrator is configuring the mail server to prevent spear phishing attacks through email messages. Which of the following refers to what the administrator is doing?
(Multiple Choice)
4.8/5 (79)
(79) Which of the following is the proper way to quantify the total monetary damage resulting from an exploited vulnerability?
(Multiple Choice)
4.7/5 (84)
(84) Which of the following is being used when a malicious actor searches various social media websites to find information about a company's system administrators and help desk staff?
(Multiple Choice)
4.8/5 (91)
(91) A security administrator is developing training for corporate users on basic security principles for personal email accounts. Which of the following should be mentioned as the MOST secure way for password recovery?
(Multiple Choice)
4.8/5 (79)
(79) An organization's research department uses workstations in an air-gapped network. A competitor released products based on files that originated in the research department. Which of the following should management do to improve the security and confidentiality of the research files?
(Multiple Choice)
4.8/5 (74)
(74) A systems administrator is installing a new server in a large datacenter. Which of the following BEST describes the importance of properly positioning servers in the rack to maintain availability?
(Multiple Choice)
4.9/5 (72)
(72) Which of the following attack types BEST describes a client-side attack that is used to manipulate an HTML iframe with JavaScript code via a web browser?
(Multiple Choice)
4.8/5 (91)
(91) Which of the following penetration testing concepts is being used when an attacker uses public Internet databases to enumerate and learn more about a target?
(Multiple Choice)
4.8/5 (88)
(88) A company has just completed a vulnerability scan of its servers. A legacy application that monitors the HVAC system in the datacenter presents several challenges, as the application vendor is no longer in business. Which of the following secure network architecture concepts would BEST protect the other company servers if the legacy server were to be exploited?
(Multiple Choice)
4.7/5 (85)
(85) A healthcare company is revamping its IT strategy in light of recent regulations. The company is concerned about compliance and wants to use a pay-per-use model. Which of the following is the BEST solution?
(Multiple Choice)
4.9/5 (85)
(85) A Chief Information Security Officer (CISO) asks the security architect to design a method for contractors to access the company's internal network securely without allowing access to systems beyond the scope of their project. Which of the following methods would BEST fit the needs of the CISO?
(Multiple Choice)
4.8/5 (88)
(88) When attempting to secure a mobile workstation, which of the following authentication technologies rely on the user's physical characteristics? (Choose two.)
(Multiple Choice)
5.0/5 (84)
(84) A security analyst is investigating a report from an employee in the human resources (HR) department who is having sporadic issues with Internet access. When the security analyst pulls the UTM logs for the IP addresses in the HR group, the following activity is shown: 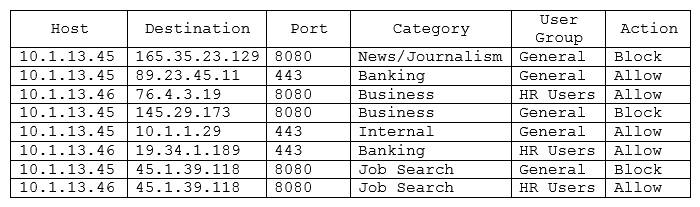 Which of the following actions should the security analyst take?
 (Multiple Choice)
4.9/5 (71)
(71) A security analyst receives an alert from a WAF with the following payload: var data= "<test test test>" ++ <../../../../../../etc/passwd>" Which of the following types of attacks is this?
(Multiple Choice)
4.9/5 (77)
(77) Showing 641 - 660 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)