



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A recent penetration test revealed several issues with a public-facing website used by customers. The testers were able to: Enter long lines of code and special characters Crash the system Gain unauthorized access to the internal application server Map the internal network The development team has stated they will need to rewrite a significant portion of the code used, and it will take more than a year to deliver the finished product. Which of the following would be the BEST solution to introduce in the interim?
(Multiple Choice)
4.8/5  (80)
(80) Given the following requirements: Help to ensure non-repudiation Capture motion in various formats Which of the following physical controls BEST matches the above descriptions?
(Multiple Choice)
4.8/5 (78)
(78) Which of the following differentiates a collision attack from a rainbow table attack?
(Multiple Choice)
4.7/5 (72)
(72) While troubleshooting a client application connecting to the network, the security administrator notices the following error: Certificate is not valid. Which of the following is the BEST way to check if the digital certificate is valid?
(Multiple Choice)
4.7/5 (74)
(74) A member of the human resources department received the following email message after sending an email containing benefit and tax information to a candidate: "Your message has been quarantined for the following policy violation: external potential_PII. Please contact the IT security administrator for further details". Which of the following BEST describes why this message was received?
(Multiple Choice)
4.9/5 (71)
(71) Ann. An employee in the payroll department, has contacted the help desk citing multiple issues with her device, including: Slow performance Word documents, PDFs, and images no longer opening A pop-up Ann states the issues began after she opened an invoice that a vendor emailed to her. Upon opening the invoice, she had to click several security warnings to view it in her word processor. With which of the following is the device MOST likely infected?
(Multiple Choice)
4.8/5 (87)
(87) An organization recently acquired an ISO 27001 certification. Which of the following would MOST likely be considered a benefit of this certification?
(Multiple Choice)
4.7/5 (63)
(63) The Chief Executive Officer (CEO) of an organization would like staff members to have the flexibility to work from home anytime during business hours, including during a pandemic or crisis. However, the CEO is concerned that some staff members may take advantage of the flexibility and work from high-risk countries while on holiday or outsource work to a third-party organization in another country. The Chief Information Officer (CIO) believes the company can implement some basic controls to mitigate the majority of the risk. Which of the following would be BEST to mitigate the CEO's concerns? (Choose two.)
(Multiple Choice)
4.8/5 (84)
(84) Which of the following vulnerability types would the type of hacker known as a script kiddie be MOST dangerous against?
(Multiple Choice)
4.8/5 (81)
(81) Which of the following allows an application to securely authenticate a user by receiving credentials from a web domain?
(Multiple Choice)
4.8/5 (80)
(80) A vulnerability scanner that uses its running service's access level to better assess vulnerabilities across multiple assets within an organization is performing a:
(Multiple Choice)
4.8/5 (77)
(77) A company is planning to encrypt the files in several sensitive directories of a file server with a symmetric key. Which of the following could be used?
(Multiple Choice)
4.8/5 (79)
(79) Which of the following solutions should an administrator use to reduce the risk from an unknown vulnerability in a third-party software application?
(Multiple Choice)
4.9/5 (77)
(77) A security analyst is hardening a server with the directory services role installed. The analyst must ensure LDAP traffic cannot be monitored or sniffed and maintains compatibility with LDAP clients. Which of the following should the analyst implement to meet these requirements? (Select two.)
(Multiple Choice)
4.8/5 (72)
(72) Which of the following BEST explains the reason why a server administrator would place a document named password.txt on the desktop of an administrator account on a server?
(Multiple Choice)
4.7/5 (84)
(84) A security analyst runs a monthly file integrity check on the main web server. When analyzing the logs, the analyst observed the following entry: 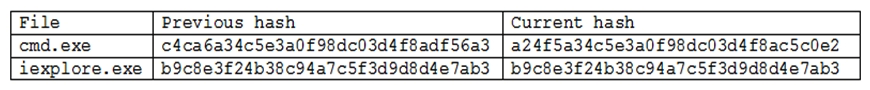 No OS patches were applied to this server during this period. Considering the log output, which of the following is the BEST conclusion?
 (Multiple Choice)
4.8/5 (75)
(75) A security administrator receives notice that a third-party certificate authority has been compromised, and new certificates will need to be issued. Which of the following should the administrator submit to receive a new certificate?
(Multiple Choice)
4.8/5 (72)
(72) An organization's internal auditor discovers that large sums of money have recently been paid to a vendor that management does not recognize. The IT security department is asked to investigate the organizations the organization's ERP system to determine how the accounts payable module has been used to make these vendor payments. The IT security department finds the following security configuration for the accounts payable module: New Vendor Entry - Required Role: Accounts Payable Clerk New Vendor Approval - Required Role: Accounts Payable Clerk Vendor Payment Entry - Required Role: Accounts Payable Clerk Vendor Payment Approval - Required Role: Accounts Payable Manager Which of the following changes to the security configuration of the accounts payable module would BEST mitigate the risk?
(Multiple Choice)
4.8/5 (84)
(84) A company recently implemented a new security system. In the course of configuration, the security administrator adds the following entry: #Whitelist USB\VID_13FE&PID_4127&REV_0100 Which of the following security technologies is MOST likely being configured?
(Multiple Choice)
4.9/5 (80)
(80) Showing 481 - 500 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)