



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A security consultant is analyzing data from a recent compromise. The following data points are documented: Access to data on share drives and certain networked hosts was lost after an employee logged in to an interactive session as a privileged user. The data was unreadable by any known commercial software. The issue spread through the enterprise via SMB only when certain users accessed data. Removal instructions were not available from any major antivirus vendor. Which of the following types of malware is this an example of?
(Multiple Choice)
4.8/5  (76)
(76) Joe is exchanging encrypted email with another party. Joe encrypts the initial email with a key. When Joe receives a response, he is unable to decrypt the response with the same key he used initially. Which of the following would explain the situation?
(Multiple Choice)
4.8/5 (71)
(71) An organization recently moved its custom web applications to the cloud, and it is obtaining managed services of the back-end environment as part of its subscription. Which of the following types of services is this company now using?
(Multiple Choice)
4.7/5 (78)
(78) A security analyst has been asked to implement secure protocols to prevent cleartext credentials from being transmitted over the internal network. Which of the following protocols is the security analyst MOST likely to implement? (Choose two.)
(Multiple Choice)
4.8/5 (84)
(84) A penetration tester is checking to see if an internal system is vulnerable to an attack using a remote listener. Which of the following commands should the penetration tester use to verify if this vulnerability exists? (Choose two.)
(Multiple Choice)
5.0/5 (94)
(94) A security administrator is configuring a new network segment, which contains devices that will be accessed by external users, such as web and FTP server. Which of the following represents the MOST secure way to configure the new network segment?
(Multiple Choice)
4.9/5 (81)
(81) After a user reports stow computer performance, a systems administrator detects a suspicious file, which was installed as part of a freeware software package. The systems administrator reviews the output below: 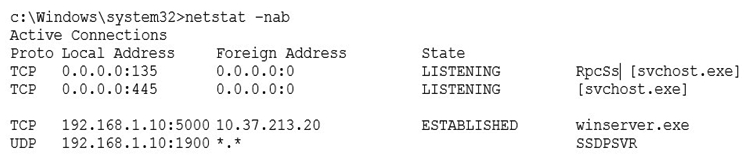 Based on the above information, which of the following types of malware was installed on the user's computer?
 (Multiple Choice)
4.9/5 (80)
(80) A small organization has implemented a rogue system detection solution. Which of the following BEST explains the organization's intent?
(Multiple Choice)
4.9/5 (82)
(82) While monitoring the SIEM, a security analyst observes traffic from an external IP to an IP address of the business network on port 443. Which of the following protocols would MOST likely cause this traffic?
(Multiple Choice)
4.8/5 (78)
(78) A consultant is configuring a vulnerability scanner for a large, global organization in multiple countries. The consultant will be using a service account to scan systems with administrative privileges on a weekly basis, but there is a concern that hackers could gain access to the account and pivot throughout the global network. Which of the following would be BEST to help mitigate this concern?
(Multiple Choice)
4.8/5 (88)
(88) A company has three divisions, each with its own networks and services. The company decides to make its secure web portal accessible to all employees utilizing their existing usernames and passwords. The security administrator has elected to use SAML to support authentication. In this scenario, which of the following will occur when users try to authenticate to the portal? (Select two.)
(Multiple Choice)
4.8/5 (80)
(80) A security guard has informed the Chief Information Security Officer that a person with a tablet has been walking around the building. The guard also noticed strange white markings in different areas of the parking lot. The person is attempting which of the following types of attacks?
(Multiple Choice)
4.9/5 (65)
(65) Which of the following describes the ability of code to target a hypervisor from inside a guest OS?
(Multiple Choice)
4.7/5 (80)
(80) Which of the following is the BEST reason for salting a password hash before it is stored in a database?
(Multiple Choice)
4.8/5 (67)
(67) A company would like to prevent the use of a known set of applications from being used on company computers. Which of the following should the security administrator implement?
(Multiple Choice)
4.7/5 (71)
(71) An organization needs to integrate with a third-party cloud application. The organization has 15000 users and does not want to allow the cloud provider to query its LDAP authentication server directly. Which of the following is the BEST way for the organization to integrate with the cloud application?
(Multiple Choice)
4.8/5 (82)
(82) A network technician is setting up a segmented network that will utilize a separate ISP to provide wireless access to the public area for a company. Which of the following wireless security methods should the technician implement to provide basic accountability for access to the public network?
(Multiple Choice)
4.8/5 (79)
(79) A member of a digital forensics team, Joe arrives at a crime scene and is preparing to collect system data. Before powering the system off, Joe knows that he must collect the most volatile date first. Which of the following is the correct order in which Joe should collect the data?
(Multiple Choice)
4.9/5 (81)
(81) The Chief Executive Officer (CEO) of a major defense contracting company a traveling overseas for a conference. The CEO will be taking a laptop. Which of the following should the security administrator implement to ensure confidentiality of the data if the laptop were to be stolen or lost during the trip?
(Multiple Choice)
4.7/5 (72)
(72) During an audit, the auditor requests to see a copy of the identified mission-critical applications as well as their disaster recovery plans. The company being audited has an SLA around the applications it hosts. With which of the following is the auditor MOST likely concerned?
(Multiple Choice)
4.9/5 (69)
(69) Showing 621 - 640 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)