



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A new Chief Information Officer (CIO) has been reviewing the badging and decides to write a policy that all employees must have their badges rekeyed at least annually. Which of the following controls BEST describes this policy?
(Multiple Choice)
4.9/5  (65)
(65) Students at a residence hall are reporting Internet connectivity issues. The university's network administrator configured the residence hall's network to provide public IP addresses to all connected devices, but many student devices are receiving private IP addresses due to rogue devices. The network administrator verifies the residence hall's network is correctly configured and contacts the security administrator for help. Which of the following configurations should the security administrator suggest for implementation?
(Multiple Choice)
4.8/5 (70)
(70) A company is currently using the following configuration: IAS server with certificate-based EAP-PEAP and MSCHAP Unencrypted authentication via PAP A security administrator needs to configure a new wireless setup with the following configurations: PAP authentication method PEAP and EAP provide two-factor authentication Which of the following forms of authentication are being used? (Choose two.)
(Multiple Choice)
4.8/5 (81)
(81) An analyst is part of a team that is investigating a potential breach of sensitive data at a large financial services organization. The organization suspects a breach occurred when proprietary data was disclosed to the public. The team finds servers were accessed using shared credentials that have been in place for some time. In addition, the team discovers undocumented firewall rules, which provided unauthorized external access to a server. Suspecting the activities of a malicious insider threat, which of the following was MOST likely to have been utilized to exfiltrate the proprietary data?
(Multiple Choice)
4.8/5 (70)
(70) A department head at a university resigned on the first day of the spring semester. It was subsequently determined that the department head deleted numerous files and directories from the server-based home directory while the campus was closed. Which of the following policies or procedures could have prevented this from occurring?
(Multiple Choice)
4.9/5 (69)
(69) Which of the following uses precomputed hashes to guess passwords?
(Multiple Choice)
4.8/5 (71)
(71) A technician is investigating a report of unusual behavior and slow performance on a company-owned laptop. The technician runs a command and reviews the following information: 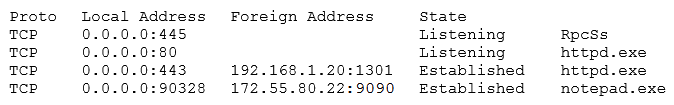 Based on the above information, which of the following types of malware should the technician report?
 (Multiple Choice)
4.7/5 (69)
(69) A security administrator has written a script that will automatically upload binary and text-based configuration files onto a remote server using a scheduled task. The configuration files contain sensitive information. Which of the following should the administrator use? (Select TWO)
(Multiple Choice)
4.9/5 (92)
(92) A system uses an application server and database server. Employing the principle of least privilege, only database administrators are given administrative privileges on the database server, and only application team members are given administrative privileges on the application server. Audit and log file reviews are performed by the business unit (a separate group from the database and application teams). The organization wants to optimize operational efficiency when application or database changes are needed, but it also wants to enforce least privilege, prevent modification of log files, and facilitate the audit and log review performed by the business unit. Which of the following approaches would BEST meet the organization's goals?
(Multiple Choice)
4.8/5 (73)
(73) When designing a web based client server application with single application server and database cluster backend, input validation should be performed:
(Multiple Choice)
4.8/5 (91)
(91) A manager wants to distribute a report to several other managers within the company. Some of them reside in remote locations that are not connected to the domain but have a local server. Because there is sensitive data within the report and the size of the report is beyond the limit of the email attachment size, emailing the report is not an option. Which of the following protocols should be implemented to distribute the report securely? (Choose three.)
(Multiple Choice)
4.9/5 (70)
(70) Which of the following is an example of federated access management?
(Multiple Choice)
4.8/5 (88)
(88) A company's AUP requires: Passwords must meet complexity requirements. Passwords are changed at least once every six months. Passwords must be at least eight characters long. An auditor is reviewing the following report: 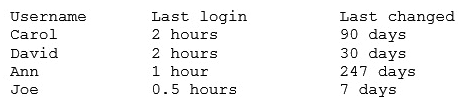 Which of the following controls should the auditor recommend to enforce the AUP?
 (Multiple Choice)
4.8/5 (78)
(78) Which of the following control types are alerts sent from a SIEM fulfilling based on vulnerability signatures?
(Multiple Choice)
4.7/5 (80)
(80) Users report the following message appears when browsing to the company's secure site: This website cannot be trusted. Which of the following actions should a security analyst take to resolve these messages? (Select two.)
(Multiple Choice)
4.7/5 (70)
(70) The Chief Information Security Officer (CISO) is asking for ways to protect against zero-day exploits. The CISO is concerned that an unrecognized threat could compromise corporate data and result in regulatory fines as well as poor corporate publicity. The network is mostly flat, with split staff/guest wireless functionality. Which of the following equipment MUST be deployed to guard against unknown threats?
(Multiple Choice)
4.9/5 (83)
(83) Which of the following attacks specifically impact data availability?
(Multiple Choice)
4.9/5 (86)
(86) A law office has been leasing dark fiber from a local telecommunications company to connect a remote office to company headquarters. The telecommunications company has decided to discontinue its dark fiber product and is offering an MPLS connection, which the law office feels is too expensive. Which of the following is the BEST solution for the law office?
(Multiple Choice)
4.8/5 (64)
(64) An attacker has gathered information about a company employee by obtaining publicly available information from the Internet and social networks. Which of the following types of activity is the attacker performing?
(Multiple Choice)
4.9/5 (72)
(72) Showing 681 - 700 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)