



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A security administrator is configuring a RADIUS server for wireless authentication. The configuration must ensure client credentials are encrypted end-to-end between the client and the authenticator. Which of the following protocols should be configured on the RADIUS server? (Choose two.)
(Multiple Choice)
4.8/5  (84)
(84) A security analyst is performing a quantitative risk analysis. The risk analysis should show the potential monetary loss each time a threat or event occurs. Given this requirement, which of the following concepts would assist the analyst in determining this value? (Choose two.)
(Multiple Choice)
4.8/5 (77)
(77) A network administrator is configuring a honeypot in a company's DMZ. To provide a method for hackers to access the system easily, the company needs to configure a plaintext authentication method that will send only the username and password to a service in the honeypot. Which of the following protocols should the company use?
(Multiple Choice)
4.7/5 (94)
(94) An in-house penetration tester has been asked to evade a new DLP system. The tester plans to exfiltrate data through steganography. Discovery of which of the following would help catch the tester in the act?
(Multiple Choice)
4.9/5 (78)
(78) A computer emergency response team is called at midnight to investigate a case in which a mail server was restarted. After an initial investigation, it was discovered that email is being exfiltrated through an active connection. Which of the following is the NEXT step the team should take?
(Multiple Choice)
4.8/5 (74)
(74) A systems developer needs to provide machine-to-machine interface between an application and a database server in the production environment. This interface will exchange data once per day. Which of the following access control account practices would BEST be used in this situation?
(Multiple Choice)
4.8/5 (78)
(78) A company is looking for an all-in-one solution to provide identification, authentication, authorization, and accounting services. Which of the following technologies should the company use?
(Multiple Choice)
4.8/5 (84)
(84) Users report the following message appears when browsing to the company's secure site: This website cannot be trusted. Which of the following actions should a security analyst take to resolve these messages? (Choose two.)
(Multiple Choice)
4.9/5 (95)
(95) While performing a penetration test, the technicians want their efforts to go unnoticed for as long as possible while they gather useful data about the network they are assessing. Which of the following would be the BEST choice for the technicians?
(Multiple Choice)
4.7/5 (61)
(61) Which of the following agreement types is a non-contractual agreement between two or more parties and outlines each party's requirements and responsibilities?
(Multiple Choice)
4.9/5 (99)
(99) A Chief Information Officer (CIO) is concerned that encryption keys might be exfiltrated by a contractor. The CIO wants to keep control over key visibility and management. Which of the following would be the BEST solution for the CIO to implement?"
(Multiple Choice)
4.8/5 (81)
(81) A user is unable to obtain an IP address from the corporate DHCP server. Which of the following is MOST likely the cause?
(Multiple Choice)
4.9/5 (70)
(70) A penetration testing team deploys a specifically crafted payload to a web server, which results in opening a new session as the web server daemon. This session has full read/write access to the file system and the admin console. Which of the following BEST describes the attack?
(Multiple Choice)
4.8/5 (66)
(66) Which of the following is the main difference an XSS vulnerability and a CSRF vulnerability?
(Multiple Choice)
4.9/5 (77)
(77) A technician has installed a new AAA server, which will be used by the network team to control access to a company's routers and switches. The technician completes the configuration by adding the network team members to the NETWORK_TEAM group, and then adding the NETWORK_TEAM group to the appropriate ALLOW_ACCESS access list. Only members of the network team should have access to the company's routers and switches. 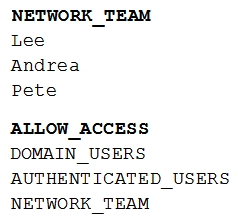 Members of the network team successfully test their ability to log on to various network devices configured to use the AAA server. Weeks later, an auditor asks to review the following access log sample:
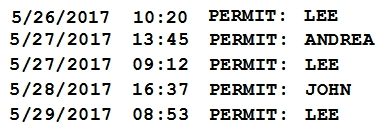 Which of the following should the auditor recommend based on the above information?
Members of the network team successfully test their ability to log on to various network devices configured to use the AAA server. Weeks later, an auditor asks to review the following access log sample: Which of the following should the auditor recommend based on the above information? (Multiple Choice)
4.9/5 (81)
(81) A security administrator has configured a RADIUS and a TACACS+ server on the company's network. Network devices will be required to connect to the TACACS+ server for authentication and send accounting information to the RADIUS server. Given the following information: RADIUS IP: 192.168.20.45 TACACS+ IP: 10.23.65.7 Which of the following should be configured on the network clients? (Select two.)
(Multiple Choice)
5.0/5 (84)
(84) A company notices that at 10 a.m. every Thursday, three users' computers become inoperable. The security analyst team discovers a file called where.pdf.exe that runs on system startup. The contents of where.pdf.exe are shown below: @echo off if [c:\file.txt] deltree C:\ Based on the above information, which of the following types of malware was discovered?
(Multiple Choice)
4.8/5 (78)
(78) Users in a corporation currently authenticate with a username and password. A security administrator wishes to implement two-factor authentication to improve security. Which of the following authentication methods should be deployed to achieve this goal?
(Multiple Choice)
4.9/5 (73)
(73) A security administrator is diagnosing a server where the CPU utilization is at 100% for 24 hours. The main culprit of CPU utilization is the antivirus program. Which of the following issue could occur if left unresolved? (Choose two.)
(Multiple Choice)
4.9/5 (75)
(75) A company is currently using the following configuration: IAS server with certificate-based EAP-PEAP and MSCHAP Unencrypted authentication via PAP A security administrator needs to configure a new wireless setup with the following configurations: PAP authentication method PEAP and EAP provide two-factor authentication Which of the following forms of authentication are being used? (Select two.)
(Multiple Choice)
4.8/5 (96)
(96) Showing 1141 - 1160 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)