



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


Which of the following provides the ability to attest to the integrity of a system from the initiation of an incident to the time the incident is litigated?
(Multiple Choice)
4.8/5  (73)
(73) During a lessons learned meeting regarding a previous incident, the security team receives a follow-up action item with the following requirements: Allow authentication from within the United States anytime Allow authentication if the user is accessing email or a shared file system Do not allow authentication if the AV program is two days out of date Do not allow authentication if the location of the device is in two specific countries Given the requirements, which of the following mobile deployment authentication types is being utilized?
(Multiple Choice)
5.0/5 (77)
(77) The IT department needs to prevent users from installing untested applications. Which of the following would provide the BEST solution?
(Multiple Choice)
4.9/5 (95)
(95) Which of the following would allow for the QUICKEST restoration of a server into a warm recovery site in a case in which server data mirroring is not enabled?
(Multiple Choice)
4.7/5 (91)
(91) After discovering a security incident and removing the affected files, an administrator disabled an unneeded service that led to the breach. Which of the following steps in the incident response process has the administrator just completed?
(Multiple Choice)
4.9/5 (80)
(80) An attacker is able to capture the payload for the following packet: IP 192.168.1.22:2020 10.10.10.5:443 IP 192.168.1.10:1030 10.10.10.1:21 IP 192.168.1.57:5217 10.10.10.1:3389 During an investigation, an analyst discovers that the attacker was able to capture the information above and use it to log on to other servers across the company. Which of the following is the MOST likely reason?
(Multiple Choice)
4.9/5 (82)
(82) A database backup schedule consists of weekly full backups performed on Saturday at 12:00 a.m. and daily differential backups also performed at 12:00 a.m. If the database is restored on Tuesday afternoon, which of the following is the number of individual backups that would need to be applied to complete the database recovery?
(Multiple Choice)
4.7/5 (84)
(84) An application developer is working on a new calendar and scheduling application. The developer wants to test new functionality that is time/date dependent and set the local system time to one year in the future. The application also has a feature that uses SHA-256 hashing and AES encryption for data exchange. The application attempts to connect to a separate remote server using SSL, but the connection fails. Which of the following is the MOST likely cause and next step?
(Multiple Choice)
4.9/5 (88)
(88) To reduce disk consumption, an organization's legal department has recently approved a new policy setting the data retention period for sent email at six months. Which of the following is the BEST way to ensure this goal is met?
(Multiple Choice)
4.9/5 (64)
(64) A junior systems administrator noticed that one of two hard drives in a server room had a red error notification. The administrator removed the hard drive to replace it but was unaware that the server was configured in an array. Which of the following configurations would ensure no data is lost?
(Multiple Choice)
4.7/5 (91)
(91) A user downloads and installs an MP3 converter, and runs the application. Upon running the application, the antivirus detects a new port in a listening state. Which of the following has the user MOST likely executed?
(Multiple Choice)
4.7/5 (79)
(79) Multiple organizations operating in the same vertical want to provide seamless wireless access for their employees as they visit the other organizations. Which of the following should be implemented if all the organizations use the native 802.1x client on their mobile devices?
(Multiple Choice)
4.9/5 (93)
(93) To determine the ALE of a particular risk, which of the following must be calculated? (Choose two.)
(Multiple Choice)
4.9/5 (68)
(68) A Security Officer on a military base needs to encrypt several smart phones that will be going into the field. Which of the following encryption solutions should be deployed in this situation?
(Multiple Choice)
4.9/5 (86)
(86) While investigating a virus infection, a security analyst discovered the following on an employee laptop: Multiple folders containing a large number of newly released movies and music files Proprietary company data A large amount of PHI data Unapproved FTP software Documents that appear to belong to a competitor Which of the following should the analyst do FIRST?
(Multiple Choice)
4.8/5 (76)
(76) A security analyst is investigating a suspected security breach and discovers the following in the logs of the potentially compromised server: 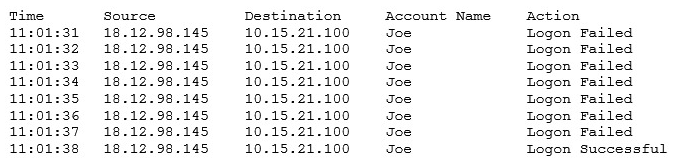 Which of the following would be the BEST method for preventing this type of suspected attack in the future?
 (Multiple Choice)
4.8/5 (69)
(69) An attacker has gained control of several systems on the Internet and is using them to attack a website, causing it to stop responding to legitimate traffic. Which of the following BEST describes the attack?
(Multiple Choice)
4.8/5 (77)
(77) During a risk assessment, results show that a fire in one of the company's datacenters could cost up to $20 million in equipment damages and lost revenue. As a result, the company insures the datacenter for up to $20 million damages for the cost of $30,000 a year. Which of the following risk response techniques has the company chosen?
(Multiple Choice)
5.0/5 (85)
(85) While reviewing the security controls in place for a web-based application, a security controls assessor notices that there are no password strength requirements in place. Because of this vulnerability, passwords might be easily discovered using a brute force attack. Which of the following password requirements will MOST effectively improve the security posture of the application against these attacks? (Choose two.)
(Multiple Choice)
4.9/5 (78)
(78) A security analyst is investigating a call from a user regarding one of the websites receiving a 503: Service Unavailable error. The analyst runs a netstat-an command to discover if the web server is up and listening. The analyst receives the following output: TCP 10.1.5.2:80 192.168.2.112:60973 TIME_WAIT TCP 10.1.5.2:80 192.168.2.112:60974 TIME_WAIT TCP 10.1.5.2:80 192.168.2.112:60975 TIME_WAIT TCP 10.1.5.2:80 192.168.2.112:60976 TIME_WAIT TCP 10.1.5.2:80 192.168.2.112:60977 TIME_WAIT TCP 10.1.5.2:80 192.168.2.112:60978 TIME_WAIT Which of the following types of attack is the analyst seeing?
(Multiple Choice)
4.7/5 (80)
(80) Showing 1001 - 1020 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)