



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


Which of the following are considered among the BEST indicators that a received message is a hoax? (Choose two.)
(Multiple Choice)
4.9/5  (71)
(71) A security administrator is reviewing the following PowerShell script referenced in the Task Scheduler on a database server: 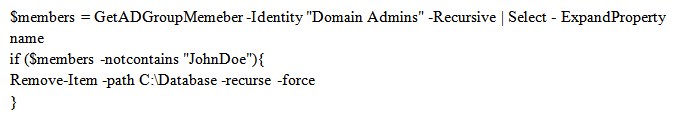 Which of the following did the security administrator discover?
 (Multiple Choice)
4.9/5 (87)
(87) A company has noticed multiple instances of proprietary information on public websites. It has also observed an increase in the number of email messages sent to random employees containing malicious links and PDFs. Which of the following changes should the company make to reduce the risks associated with phishing attacks? (Select TWO)
(Multiple Choice)
4.8/5 (83)
(83) An organization wants to utilize a common, Internet-based third-party provider for authorization and authentication. The provider uses a technology based on OAuth 2.0 to provide required services. To which of the following technologies is the provider referring?
(Multiple Choice)
4.8/5 (73)
(73) A security administrator has been conducting an account permissions review that has identified several users who belong to functional groups and groups responsible for auditing the functional groups' actions. Several recent outages have not been able to be traced to any user. Which of the following should the security administrator recommend to preserve future audit log integrity?
(Multiple Choice)
4.9/5 (77)
(77) Which of the following describes the key difference between vishing and phishing attacks?
(Multiple Choice)
4.9/5 (72)
(72) The data backup window has expanded into the morning hours and has begun to affect production users. The main bottleneck in the process is the time it takes to replicate the backups to separate severs at the offsite data center. Which of the following uses of deduplication could be implemented to reduce the backup window?
(Multiple Choice)
4.7/5 (75)
(75) A security administrator learns that PII, which was gathered by the organization, has been found in an open forum. As a result, several C-level executives found their identities were compromised, and they were victims of a recent whaling attack. Which of the following would prevent these problems in the future? (Select TWO).
(Multiple Choice)
4.9/5 (80)
(80) A systems administrator is receiving multiple alerts from the company NIPS. A review of the NIPS logs shows the following: reset both: 70.32.200.2:3194 -> 10.4.100.4:80 buffer overflow attempt reset both: 70.32.200.2:3230 -> 10.4.100.4:80 directory traversal attack reset client: 70.32.200.2:4019 -> 10.4.100.4:80 Blind SQL injection attack Which of the following should the systems administrator report back to management?
(Multiple Choice)
4.8/5 (90)
(90) A penetration tester has successfully accessed a web server using an exploit in the user-agent string for Apache Struts. The tester then brute forces a credential that provides access to the back-end database server in a different subnet. This is an example of:
(Multiple Choice)
4.8/5 (95)
(95) Which of the following is an example of resource exhaustion?
(Multiple Choice)
4.9/5 (77)
(77) The Chief Security Officer (CISO) at a multinational banking corporation is reviewing a plan to upgrade the entire corporate IT infrastructure. The architecture consists of a centralized cloud environment hosting the majority of data, small server clusters at each corporate location to handle the majority of customer transaction processing, ATMs, and a new mobile banking application accessible from smartphones, tablets, and the Internet via HTTP. The corporation does business having varying data retention and privacy laws. Which of the following technical modifications to the architecture and corresponding security controls should be implemented to provide the MOST complete protection of data?
(Multiple Choice)
4.8/5 (62)
(62) A network administrator needs to prevent users from accessing the accounting department records. All users are connected to the same Layer 2 device and access the Internet through the same router. Which of the following should be implemented to segment the accounting department from the rest of the users?
(Multiple Choice)
4.8/5 (91)
(91) A security administrator wants to implement a logon script that will prevent MITM attacks on the local LAN. Which of the following commands should the security administrator implement within the script to accomplish this task? 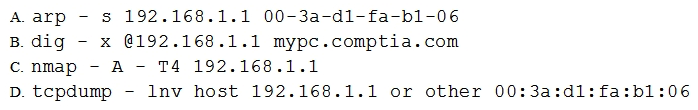
(Multiple Choice)
5.0/5 (88)
(88) A developer has just finished coding a custom web application and would like to test it for bugs by automatically injecting mailformed data into it. Which of the following is the developer looking to perform?
(Multiple Choice)
4.7/5 (86)
(86) A company researched the root cause of a recent vulnerability in its software. It was determined that the vulnerability was the result of two updates made in the last release. Each update alone would not have resulted in the vulnerability. In order to prevent similar situations in the future, the company should improve which of the following?
(Multiple Choice)
4.8/5 (80)
(80) As a security measure, an organization has disabled all external media from accessing the network. Since some users may have data that needs to be transferred to the network, which of the following would BEST assist a security administrator with transferring the data while keeping the internal network secure?
(Multiple Choice)
4.8/5 (73)
(73) Which of the following techniques can be bypass a user or computer's web browser privacy settings? (Choose two.)
(Multiple Choice)
4.9/5 (85)
(85) A security administrator is investigating many recent incidents of credential theft for users accessing the company's website, despite the hosting web server requiring HTTPS for access. The server's logs show the website leverages the HTTP POST method for carrying user authentication details. Which of the following is the MOST likely reason for compromise?
(Multiple Choice)
5.0/5 (81)
(81) A security analyst has identified malware that is propagating automatically to multiple systems on the network. Which of the following types of malware is MOST likely impacting the network?
(Multiple Choice)
4.9/5 (94)
(94) Showing 1021 - 1040 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)