



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An organization has several production-critical SCADA supervisory systems that cannot follow the normal 30- day patching policy. Which of the following BEST maximizes the protection of these systems from malicious software?
(Multiple Choice)
4.8/5  (82)
(82) Users are attempting to access a company's website but are transparently redirected to another websites. The users confirm the URL is correct. Which of the following would BEST prevent this issue in the future?
(Multiple Choice)
4.9/5 (76)
(76) A systems administrator is deploying a new mission essential server into a virtual environment. Which of the following is BEST mitigated by the environment's rapid elasticity characteristic?
(Multiple Choice)
4.9/5 (88)
(88) An organization uses SSO authentication for employee access to network resources. When an employee resigns, as per the organization's security policy, the employee's access to all network resources is terminated immediately. Two weeks later, the former employee sends an email to the help desk for a password reset to access payroll information from the human resources server. Which of the following represents the BEST course of action?
(Multiple Choice)
4.8/5 (80)
(80) Which of the following is a major difference between XSS attacks and remote code exploits?
(Multiple Choice)
4.8/5 (84)
(84) Which of the following differentiates ARP poisoning from a MAC spoofing attack?
(Multiple Choice)
4.8/5 (97)
(97) Which of the following attack types is being carried out where a target is being sent unsolicited messages via Bluetooth?
(Multiple Choice)
4.9/5 (75)
(75) A security auditor is putting together a report for the Chief Executive Officer (CEO) on personnel security and its impact on the security posture of the whole organization. Which of the following would be the MOST important factor to consider when it comes to personnel security?
(Multiple Choice)
4.8/5 (95)
(95) An audit takes place after company-wide restricting, in which several employees changed roles. The following deficiencies are found during the audit regarding access to confidential data: 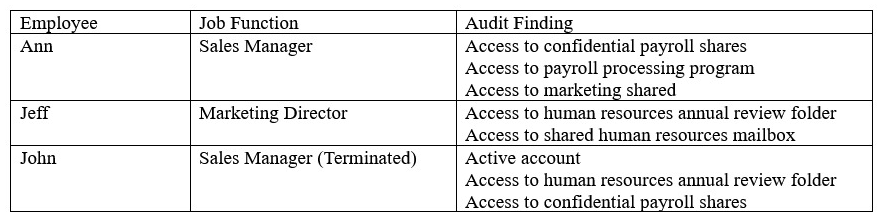 Which of the following would be the BEST method to prevent similar audit findings in the future?
 (Multiple Choice)
4.7/5 (92)
(92) A manager suspects that an IT employee with elevated database access may be knowingly modifying financial transactions for the benefit of a competitor. Which of the following practices should the manager implement to validate the concern?
(Multiple Choice)
4.9/5 (84)
(84) A vulnerability scan is being conducted against a desktop system. The scan is looking for files, versions, and registry values known to be associated with system vulnerabilities. Which of the following BEST describes the type of scan being performed?
(Multiple Choice)
4.9/5 (83)
(83) Anne, the Chief Executive Officer (CEO), has reported that she is getting multiple telephone calls from someone claiming to be from the helpdesk. The caller is asking to verify her network authentication credentials because her computer is broadcasting across the network. This is MOST likely which of the following types of attacks?
(Multiple Choice)
4.8/5 (76)
(76) A security team received reports of increased latency on a highly utilized e-commerce server. This led to eventual service unavailability as a result of internal scanning activity. The following web-server log was shared with the team to support this claim: 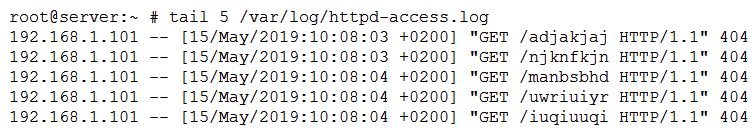 Which of the following actions would BEST address the service impact caused by scanning?
 (Multiple Choice)
4.8/5 (75)
(75) An organization is using a tool to perform a source code review. Which of the following describes the case in which the tool incorrectly identifies the vulnerability?
(Multiple Choice)
4.8/5 (83)
(83) Given the log output: Max 15 00:15:23.431 CRT: #SEC_LOGIN-5-LOGIN_SUCCESS: Login Success [user: msmith] [Source: 10.0.12.45] [localport: 23] at 00:15:23:431 CET Sun Mar 15 2015 Which of the following should the network administrator do to protect data security?
(Multiple Choice)
4.8/5 (69)
(69) A company's user lockout policy is enabled after five unsuccessful login attempts. The help desk notices a user is repeatedly locked out over the course of a workweek. Upon contacting the user, the help desk discovers the user is on vacation and does not have network access. Which of the following types of attacks are MOST likely occurring? (Select two.)
(Multiple Choice)
4.9/5 (79)
(79) An organization with very high security needs wants to implement a biometric system. It is required to minimize unauthorized access by ensuring authorized personnel are not denied access. Which of the following solutions will work?
(Multiple Choice)
4.9/5 (78)
(78) Malware that changes its binary pattern on specific dates at specific times to avoid detection is known as a (n):
(Multiple Choice)
5.0/5 (89)
(89) Which of the following authentication concepts is a gait analysis MOST closely associated?
(Multiple Choice)
4.7/5 (65)
(65) Showing 941 - 960 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)