



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


Which of the following should a technician use to protect a cellular phone that is needed for an investigation, to ensure the data will not be removed remotely?
(Multiple Choice)
4.9/5  (69)
(69) A company is executing a strategy to encrypt and sign all proprietary data in transit. The company recently deployed PKI services to support this strategy. Which of the following protocols supports the strategy and employs certificates generated by the PKI? (Choose three.)
(Multiple Choice)
4.9/5 (78)
(78) Which of the following is MOST likely caused by improper input handling?
(Multiple Choice)
4.8/5 (72)
(72) The exploitation of a buffer-overrun vulnerability in an application will MOST likely lead to:
(Multiple Choice)
4.9/5 (82)
(82) Which of the following development models entails several iterative and incremental software development methodologies such as Scrum?
(Multiple Choice)
4.7/5 (85)
(85) In an effort to reduce data storage requirements, some company devices to hash every file and eliminate duplicates. The data processing routines are time sensitive so the hashing algorithm is fast and supported on a wide range of systems. Which of the following algorithms is BEST suited for this purpose?
(Multiple Choice)
4.8/5 (73)
(73) A user needs to send sensitive information to a colleague using PKI. Which of the following concepts apply when a sender encrypts the message hash with the sender's private key? (Choose two.)
(Multiple Choice)
4.9/5 (83)
(83) Given the following: 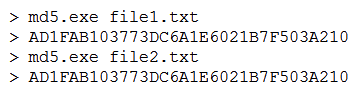 Which of the following concepts of cryptography is shown?
 (Multiple Choice)
4.8/5 (88)
(88) After a security assessment was performed on the enterprise network, it was discovered that: Configuration changes have been made by users without the consent of IT. Network congestion has increased due to the use of social media. Users are accessing file folders and network shares that are beyond the scope of their need to know. Which of the following BEST describe the vulnerabilities that exist in this environment? (Choose two.)
(Multiple Choice)
4.9/5 (80)
(80) A Chief Information Security Officer (CISO) is performing a BIA for the organization in case of a natural disaster. Which of the following should be at the top of the CISO's list?
(Multiple Choice)
4.9/5 (87)
(87) A state-sponsored threat actor has launched several successful attacks against a corporate network. Although the target has a robust patch management program in place, the attacks continue in depth and scope, and the security department has no idea how the attacks are able to gain access. Given that patch management and vulnerability scanners are being used, which of the following would be used to analyze the attack methodology?
(Multiple Choice)
4.8/5 (87)
(87) A technician needs to document which application versions are listening on open ports. Which of the following is MOST likely to return the information the technician needs?
(Multiple Choice)
4.8/5 (94)
(94) A mobile application developer wants to secure an application that transmits sensitive information. Which of the following should the developer implement to prevent SSL MITM attacks?
(Multiple Choice)
4.8/5 (79)
(79) A company hires a consulting firm to crawl its Active Directory network with a non-domain account looking for unpatched systems. Actively taking control of systems is out of scope, as is the creation of new administrator accounts. For which of the following is the company hiring the consulting firm?
(Multiple Choice)
4.9/5 (76)
(76) To get the most accurate results on the security posture of a system, which of the following actions should the security analyst do prior to scanning?
(Multiple Choice)
4.9/5 (78)
(78) A security analyst is acquiring data from a potential network incident. Which of the following evidence is the analyst MOST likely to obtain to determine the incident?
(Multiple Choice)
4.9/5 (74)
(74) An organization wants to implement a method to correct risks at the system/application layer. Which of the following is the BEST method to accomplish this goal?
(Multiple Choice)
4.8/5 (68)
(68) An organization allows the use of open-source software as long as users perform a file integrity check on the executables and verify the file against hashes of known malware. A user downloads the following files from an open-source website: 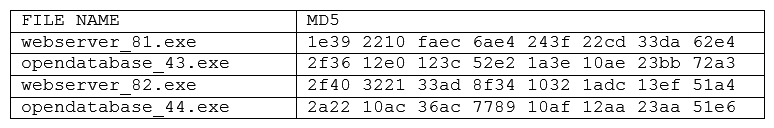 After submitting the hashes to the malware registry, the user is alerted that 2f40 3221 33ad 8f34 1032 1adc 13ef 51a4 matches a known malware signature. The organization has been running all of the above software with no known issues. Which of the following actions should the user take and why?
 (Multiple Choice)
4.8/5 (75)
(75) A company was recently audited by a third party. The audit revealed the company's network devices were transferring files in the clear. Which of the following protocols should the company use to transfer files?
(Multiple Choice)
4.8/5 (84)
(84) Exercising various programming responses for the purpose of gaining insight into a system's security posture without exploiting the system is BEST described as:
(Multiple Choice)
4.8/5 (87)
(87) Showing 781 - 800 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)