



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A security administrator has completed a monthly review of DNS server query logs. The administrator notices continuous name resolution attempts from a large number of internal hosts to a single Internet addressable domain name. The security administrator then correlated those logs with the establishment of persistent TCP connections out to this domain. The connections seem to be carrying on the order of kilobytes of data per week. Which of the following is the MOST likely explanation for this anomaly?
(Multiple Choice)
4.8/5  (92)
(92) A security analyst is hardening an authentication server. One of the primary requirements is to ensure there is mutual authentication and delegation. Given these requirements, which of the following technologies should the analyst recommend and configure?
(Multiple Choice)
4.7/5 (73)
(73) Several workstations on a network are found to be on OS versions that are vulnerable to a specific attack. Which of the following is considered to be a corrective action to combat this vulnerability?
(Multiple Choice)
4.9/5 (66)
(66) A company hired a third-party firm to conduct as assessment of vulnerabilities exposed to the Internet. The firm informs the company that an exploit exists for an FTP server that has a version installed from eight years ago. The company has decided to keep the system online anyway, as no upgrade exists from the vendor. Which of the following BEST describes the reason why the vulnerability exists?
(Multiple Choice)
4.9/5 (69)
(69) An organization is concerned about video emissions from users' desktops. Which of the following is the BEST solution to implement?
(Multiple Choice)
4.8/5 (89)
(89) A stock trading company had the budget for enhancing its secondary datacenter approved. Since the main site is in a hurricane-affected area and the disaster recovery site is 100mi (161km) away, the company wants to ensure its business is always operational with the least amount of man hours needed. Which of the following types of disaster recovery sites should the company implement?
(Multiple Choice)
4.8/5 (87)
(87) A technician has been asked to document which services are running on each of a collection of 200 servers. Which of the following tools BEST meets this need while minimizing the work required?
(Multiple Choice)
4.9/5 (83)
(83) Upon entering an incorrect password, the logon screen displays a message informing the user that the password does not match the username provided and is not the required length of 12 characters. Which of the following secure coding techniques should a security analyst address with the application developers to follow security best practices?
(Multiple Choice)
4.9/5 (79)
(79) A penetration tester has written an application that performs a bit-by-bit XOR 0xFF operation on binaries prior to transmission over untrusted media. Which of the following BEST describes the action performed by this type of application?
(Multiple Choice)
4.9/5 (78)
(78) A technician is auditing network security by connecting a laptop to open hardwired jacks within the facility to verify they cannot connect. Which of the following is being tested?
(Multiple Choice)
4.9/5 (80)
(80) A user receives a security alert pop-up from the host-based IDS, and a few minutes later notices a document on the desktop has disappeared and in its place is an odd filename with no icon image. When clicking on this icon, the user receives a system notification that it cannot find the correct program to use to open this file. Which of the following types of malware has MOST likely targeted this workstation?
(Multiple Choice)
4.8/5 (83)
(83) Recently several employees were victims of a phishing email that appeared to originate from the company president. The email claimed the employees would be disciplined if they did not click on a malicious link in the message. Which of the following principles of social engineering made this attack successful?
(Multiple Choice)
4.9/5 (87)
(87) An organization hosts a public-facing website that contains a login page for users who are registered and authorized to access a secure, non-public section of the site. That non-public site hosts information that requires multifactor authentication for access. Which of the following access management approaches would be the BEST practice for the organization?
(Multiple Choice)
4.9/5 (86)
(86) A computer forensics analyst collected a flash drive that contained a single file with 500 pages of text. Which of the following algorithms should the analyst use to validate the integrity of the file?
(Multiple Choice)
4.9/5 (86)
(86) A network administrator has been alerted that web pages are experiencing long load times. After determining it is not a routing or DNS issue, the administrator logs in to the router, runs a command, and receives the following output: 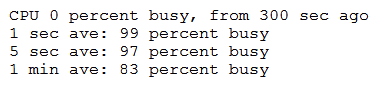 Which of the following is the router experiencing?
 (Multiple Choice)
4.8/5 (85)
(85) An administrator is testing the collision resistance of different hashing algorithms. Which of the following is the strongest collision resistance test?
(Multiple Choice)
4.9/5 (83)
(83) A company has forbidden the use of external media within its headquarters location. A security analyst is working on adding additional repositories to a server in the environment when the analyst notices some odd processes running on the system. The analyst runs a command and sees the following: 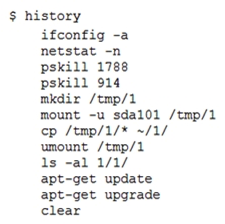 Given this output, which of the following security issues has been discovered?
 (Multiple Choice)
4.9/5 (91)
(91) A company is planning to build an internal website that allows for access to outside contracts and partners. A majority of the content will only be to internal employees with the option to share. Which of the following concepts is MOST appropriate?
(Multiple Choice)
4.8/5 (73)
(73) Which of the following vulnerabilities can lead to unexpected system behavior, including the bypassing of security controls, due to differences between the time of commitment and the time of execution?
(Multiple Choice)
4.9/5 (75)
(75) Which of the following types of attacks precedes the installation of a rootkit on a server?
(Multiple Choice)
4.8/5 (71)
(71) Showing 341 - 360 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)