



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A systems engineer wants to leverage a cloud-based architecture with low latency between network-connected devices that also reduces the bandwidth that is required by performing analytics directly on the endpoints. Which of the following would BEST meet the requirements? (Choose two.)
(Multiple Choice)
5.0/5  (87)
(87) After a user reports slow computer performance, a system administrator detects a suspicious file, which was installed as part of a freeware software package. The systems administrator reviews the output below: 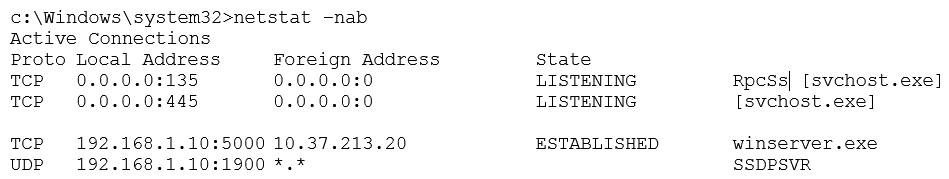 Based on the above information, which of the following types of malware was installed on the user's computer?
 (Multiple Choice)
4.7/5 (78)
(78) A dumpster diver recovers several hard drives from a company and is able to obtain confidential data from one of the hard drives. The company then discovers its information is posted online. Which of the following methods would have MOST likely prevented the data from being exposed?
(Multiple Choice)
4.9/5 (76)
(76) Which of the following is an example of the second A in the AAA model?
(Multiple Choice)
4.8/5 (84)
(84) Joe, a member of the sales team, recently logged into the company servers after midnight local time to download the daily lead form before his coworkers did. Management has asked the security team to provide a method for detecting this type of behavior without impeding the access for sales employee as they travel overseas. Which of the following would be the BEST method to achieve this objective?
(Multiple Choice)
4.8/5 (79)
(79) Ann, a user, reports she is receiving emails that appear to be from organizations to which she belongs, but the emails contain links to websites that do not belong to those organizations. Which of the following security scenarios does this describe?
(Multiple Choice)
4.7/5 (73)
(73) When it comes to cloud computing, if one of the requirements for a project is to have the most control over the systems in the cloud, which of the following is a service model that would be BEST suited for this goal?
(Multiple Choice)
4.9/5 (76)
(76) Which of the following types of cloud infrastructures would allow several organizations with similar structures and interests to realize the benefits of shared storage and resources?
(Multiple Choice)
4.8/5 (82)
(82) A security analyst conducts a manual scan on a known hardened host that identifies many non-compliant items. Which of the following BEST describe why this has occurred? (Choose two.)
(Multiple Choice)
4.8/5 (83)
(83) A security analyst is performing a BIA. The analyst notes that in a disaster, failover systems must be up and running within 30 minutes. The failover systems must use backup data that is no older than one hour. Which of the following should the analyst include in the business continuity plan?
(Multiple Choice)
4.8/5 (78)
(78) A company wishes to move all of its services and applications to a cloud provider but wants to maintain full control of the deployment, access, and provisions of its services to its users. Which of the following BEST represents the required cloud deployment model?
(Multiple Choice)
4.9/5 (80)
(80) A member of the admins group reports being unable to modify the "changes" file on a server. The permissions on the file are as follows: Permissions User Group File -rwxrw-r--+ Admins Admins changes Based on the output above, which of the following BEST explains why the user is unable to modify the "changes" file?
(Multiple Choice)
4.8/5 (69)
(69) When considering IoT systems, which of the following represents the GREATEST ongoing risk after a vulnerability has been discovered?
(Multiple Choice)
4.9/5 (81)
(81) Which of the following scenarios would make a DNS sinkhole effective in thwarting an attack?
(Multiple Choice)
4.8/5 (76)
(76) After successfully breaking into several networks and infecting multiple machines with malware, hackers contact the network owners, demanding payment to remove the infection and decrypt files. The hackers threaten to publicly release information about the breach if they are not paid. Which of the following BEST describes these attackers?
(Multiple Choice)
4.9/5 (77)
(77) Which of the following is commonly done as part of a vulnerability scan?
(Multiple Choice)
4.9/5 (69)
(69) Which of the following works by implanting software on systems but delays execution until a specific set of conditions is met?
(Multiple Choice)
4.9/5 (79)
(79) Which of the following is the BEST explanation of why control diversity is important in a defense-in-depth architecture?
(Multiple Choice)
4.9/5 (71)
(71) An incident responder is preparing to acquire images and files from a workstation that has been compromised. The workstation is still powered on and running. Which of the following should be acquired LAST?
(Multiple Choice)
4.9/5 (77)
(77) Showing 221 - 240 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)