



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An organization's Chief Executive Officer (CEO) directs a newly hired computer technician to install an OS on the CEO's personal laptop. The technician performs the installation, and a software audit later in the month indicates a violation of the EULA occurred as a result. Which of the following would address this violation going forward?
(Multiple Choice)
4.8/5  (77)
(77) A security analyst is reviewing the following output from an IPS: 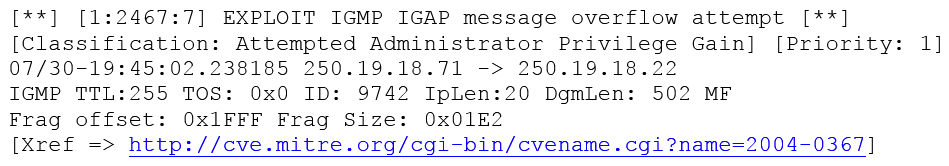 Given this output, which of the following can be concluded? (Select two.)
 (Multiple Choice)
4.7/5 (90)
(90) Every morning, a systems administrator monitors failed login attempts on the company's log management server. The administrator notices the DBAdmin account has five failed username and/or password alerts during a ten-minute window. The systems administrator determines the user account is a dummy account used to attract attackers. Which of the following techniques should the systems administrator implement?
(Multiple Choice)
4.7/5 (71)
(71) Which of the following threats has sufficient knowledge to cause the MOST danger to an organization?
(Multiple Choice)
4.9/5 (70)
(70) During a routine vulnerability assessment, the following command was successful: echo "vrfy 'perl -e 'print "hi" x 500 ' ' " | nc www.company.com 25 Which of the following vulnerabilities is being exploited?
(Multiple Choice)
4.8/5 (93)
(93) A technician needs to implement a system which will properly authenticate users by their username and password only when the users are logging in from a computer in the office building. Any attempt to authenticate from a location other than the office building should be rejected. Which of the following MUST the technician implement?
(Multiple Choice)
4.9/5 (82)
(82) A security analyst is testing both Windows and Linux systems for unauthorized DNS zone transfers within a LAN on comptia.org from example.org. Which of the following commands should the security analyst use? (Select two.)
(Multiple Choice)
4.7/5 (64)
(64) A company moved into a new building next to a sugar mill. Cracks have been discovered in the walls of the server room, which is located on the same side as the sugar mill loading docks. The cracks are believed to have been caused by heavy trucks. Moisture has begun to seep into the server room, causing extreme humidification problems and equipment failure. Which of the following BEST describes the type of threat the organization faces?
(Multiple Choice)
4.8/5 (79)
(79) An analysis of a threat actor, which has been active for several years, reveals the threat actor has high levels of funding, motivation, and sophistication. Which of the following types of threat actors does this BEST describe?
(Multiple Choice)
4.9/5 (80)
(80) When accessing a popular website, a user receives a warming that the certificate for the website is not valid. Upon investigation, it was noted that the certificate is not revoked and the website is working fine for other users. Which of the following is the MOST likely cause for this?
(Multiple Choice)
4.7/5 (71)
(71) A network technician discovered the usernames and passwords used for network device configuration have been compromised by a user with a packet sniffer. Which of the following would secure the credentials from sniffing?
(Multiple Choice)
4.8/5 (80)
(80) A malicious attacker has intercepted HTTP traffic and inserted an ASCII line that sets the referrer URL. Which of the following is the attacker most likely utilizing?
(Multiple Choice)
4.9/5 (77)
(77) Which of the following is the MOST likely motivation for a script kiddie threat actor?
(Multiple Choice)
4.9/5 (68)
(68) A senior incident response manager receives a call about some external IPs communicating with internal computers during off hours. Which of the following types of malware is MOST likely causing this issue?
(Multiple Choice)
4.9/5 (93)
(93) A company has migrated to two-factor authentication for accessing the corporate network, VPN, and SSO. Several legacy applications cannot support multifactor authentication and must continue to use usernames and passwords. Which of the following should be implemented to ensure the legacy applications are as secure as possible while ensuring functionality? (Choose two.)
(Multiple Choice)
4.8/5 (89)
(89) Which of the following allows an auditor to test proprietary-software compiled code for security flaws?
(Multiple Choice)
4.8/5 (77)
(77) Audit logs from a small company's vulnerability scanning software show the following findings: Destinations scanned: -Server001- Internal human resources payroll server -Server101-Internet-facing web server -Server201- SQL server for Server101 -Server301-Jumpbox used by systems administrators accessible from the internal network Validated vulnerabilities found: -Server001- Vulnerable to buffer overflow exploit that may allow attackers to install software -Server101- Vulnerable to buffer overflow exploit that may allow attackers to install software -Server201-OS updates not fully current -Server301- Accessible from internal network without the use of jumpbox -Server301-Vulnerable to highly publicized exploit that can elevate user privileges Assuming external attackers who are gaining unauthorized information are of the highest concern, which of the following servers should be addressed FIRST?
(Multiple Choice)
4.8/5 (69)
(69) New magnetic locks were ordered for an entire building. In accordance with company policy, employee safety is the top priority. In case of a fire where electricity is cut, which of the following should be taken into consideration when installing the new locks?
(Multiple Choice)
4.8/5 (91)
(91) After an identified security breach, an analyst is tasked to initiate the IR process. Which of the following is the NEXT step the analyst should take?
(Multiple Choice)
4.9/5 (86)
(86) Showing 881 - 900 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)