



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An employee workstation with an IP address of 204.211.38.211/24 reports it is unable to submit print jobs to a network printer at 204.211.38.52/24 after a firewall upgrade. The active firewall rules are as follows: 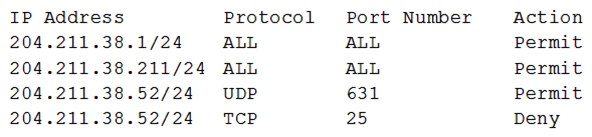 Assuming port numbers have not been changed from their defaults, which of the following should be modified to allow printing to the network printer?
 (Multiple Choice)
4.8/5  (72)
(72) An employee opens a web browser and types a URL into the address bar. Instead of reaching the requested site, the browser opens a completely different site. Which of the following types of attacks have MOST likely occurred? (Choose two.)
(Multiple Choice)
4.8/5 (75)
(75) In the event of a security incident, which of the following should be captured FIRST?
(Multiple Choice)
4.8/5 (77)
(77) An organization is expanding its network team. Currently, it has local accounts on all network devices, but with growth, it wants to move to centrally managed authentication. Which of the following are the BEST solutions for the organization? (Select TWO)
(Multiple Choice)
4.9/5 (74)
(74) An organization wants to conduct secure transactions of large data files. Before encrypting and exchanging the data files, the organization wants to ensure a secure exchange of keys. Which of the following algorithms is appropriate for securing the key exchange?
(Multiple Choice)
4.8/5 (100)
(100) A web server, which is configured to use TLS with AES-GCM-256, SHA-384, and ECDSA, recently suffered an information loss breach. Which of the following is MOST likely the cause?
(Multiple Choice)
4.9/5 (92)
(92) An incident response manager has started to gather all the facts related to a SIEM alert showing multiple systems may have been compromised. The manager has gathered these facts: The breach is currently indicated on six user PCs One service account is potentially compromised Executive management has been notified In which of the following phases of the IRP is the manager currently working?
(Multiple Choice)
4.9/5 (85)
(85) An administrator is disposing of media that contains sensitive information. Which of the following will provide the MOST effective method to dispose of the media while ensuring the data will be unrecoverable?
(Multiple Choice)
4.9/5 (74)
(74) A security administrator needs to configure remote access to a file share so it can only be accessed between the hours of 9:00 a.m. and 5:00 p.m. Files in the share can only be accessed by members of the same department as the data owner. Users should only be able to create files with approved extensions, which may differ by department. Which of the following access controls would be the MOST appropriate for this situation?
(Multiple Choice)
4.7/5 (85)
(85) Malicious traffic from an internal network has been detected on an unauthorized port on an application server. Which of the following network-based security controls should the engineer consider implementing?
(Multiple Choice)
4.8/5 (80)
(80) Which of the following BEST explains why a development environment should have the same database server secure baseline that exists in production even if there is no PII in the database?
(Multiple Choice)
4.8/5 (81)
(81) A small company's Chief Executive Officer (CEO) has asked its Chief Security Officer (CSO) to improve the company's security posture quickly with regard to targeted attacks. Which of the following should the CSO conduct FIRST?
(Multiple Choice)
5.0/5 (86)
(86) A user receives an email from ISP indicating malicious traffic coming from the user's home network is detected. The traffic appears to be Linux-based, and it is targeting a website that was recently featured on the news as being taken offline by an Internet attack. The only Linux device on the network is a home surveillance camera system. Which of the following BEST describes what is happening?
(Multiple Choice)
4.9/5 (84)
(84) A bank is experiencing a DoS attack against an application designed to handle 500 IP-based sessions. in addition, the perimeter router can only handle 1Gbps of traffic. Which of the following should be implemented to prevent a DoS attacks in the future?
(Multiple Choice)
4.8/5 (84)
(84) Which of the following implements two-factor authentication on a VPN?
(Multiple Choice)
4.9/5 (86)
(86) A security analyst has set up a network tap to monitor network traffic for vulnerabilities. Which of the following techniques would BEST describe the approach the analyst has taken?
(Multiple Choice)
4.9/5 (74)
(74) A security administrator needs to address the following audit recommendations for a public-facing SFTP server: Users should be restricted to upload and download files to their own home directories only. Users should not be allowed to use interactive shell login. Which of the following configuration parameters should be implemented? (Choose two.).
(Multiple Choice)
4.8/5 (88)
(88) Which of the following characteristics differentiate a rainbow table attack from a brute force attack? (Choose two.)
(Multiple Choice)
4.8/5 (82)
(82) A security engineer wants to add SSL to the public web server. Which of the following would be the FIRST step to implement the SSL certificate?
(Multiple Choice)
4.9/5 (75)
(75) A systems administrator is reviewing the following information from a compromised server: 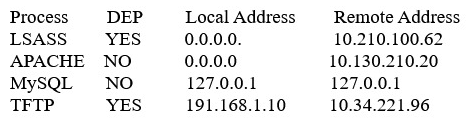 Given the above information, which of the following processes was MOST likely exploited via a remote buffer overflow attack?
 (Multiple Choice)
4.7/5 (69)
(69) Showing 861 - 880 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)