



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


The Chief Information Officer (CIO) has decided to add two-factor authentication along with the use of passwords when logging on to the network. Which of the following should be implemented to BEST accomplish this requirement?
(Multiple Choice)
4.9/5  (72)
(72) The process of applying a salt and cryptographic hash to a password then repeating the process many times is known as which of the following?
(Multiple Choice)
4.9/5 (90)
(90) A systems administrator is installing and configuring an application service that requires access to read and write to log and configuration files on a local hard disk partition. The service must run as an account with authorization to interact with the file system. Which of the following would reduce the attack surface added by the service and account? (Choose two.)
(Multiple Choice)
4.7/5 (94)
(94) Joe, a user, has been trying to send Ann, a different user, an encrypted document via email. Ann has not received the attachment but is able to receive the header information. Which of the following is MOST likely preventing Ann from receiving the encrypted file?
(Multiple Choice)
4.9/5 (84)
(84) A security consultant discovers that an organization is using the PCL protocol to print documents, utilizing the default driver and print settings. Which of the following is the MOST likely risk in this situation?
(Multiple Choice)
4.9/5 (74)
(74) When backing up a database server to LTO tape drives, the following backup schedule is used. Backups take one hour to complete: 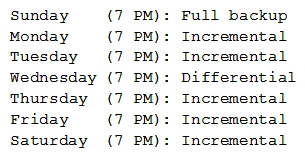 On Friday at 9:00 p.m., there is a RAID failure on the database server. The data must be restored from backup. Which of the following is the number of backup tapes that will be needed to complete this operation?
 (Multiple Choice)
4.8/5 (75)
(75) A company is planning to build an internal website that allows for access to outside contracts and partners. A majority of the content will only be available to internal employees with the option to share. Which of the following concepts is MOST appropriate?
(Multiple Choice)
4.8/5 (66)
(66) Which of the following is a benefit of credentialed vulnerability scans?
(Multiple Choice)
4.9/5 (74)
(74) A developer is creating a new web application on a public cloud platform and wants to ensure the application can respond to increases in load while minimizing costs during periods of low usage. Which of the following strategies is MOST relevant to the use-case?
(Multiple Choice)
4.8/5 (78)
(78) A tester was able to leverage a pass-the-hash attack during a recent penetration test. The tester gained a foothold and moved laterally through the network. Which of the following would prevent this type of attack from reoccurring?
(Multiple Choice)
4.8/5 (77)
(77) A security administrator is investigating a report that a user is receiving suspicious emails. The user's machine has an old functioning modem installed. Which of the following security concerns need to be identified and mitigated? (Choose two.)
(Multiple Choice)
4.7/5 (74)
(74) A security analyst captures forensic evidence from a potentially compromised system for further investigation. The evidence is documented and securely stored to FIRST:
(Multiple Choice)
4.9/5 (78)
(78) After deploying an antivirus solution on some network-isolated industrial computers, the service desk team received a trouble ticket about the following message being displayed on the computers' screens: Your AV protection has blocked an unknown application while performing suspicious activities. The application was put in quarantine. Which of the following would be the SAFEST next step to address the issue?
(Multiple Choice)
4.8/5 (74)
(74) Joe, a user at a company, clicked an email link that led to a website that infected his workstation. Joe was connected to the network, and the virus spread to the network shares. The protective measures failed to stop this virus, and it has continued to evade detection. Which of the following should a security administrator implement to protect the environment from this malware?
(Multiple Choice)
4.8/5 (82)
(82) A network administrator adds an ACL to allow only HTTPS connections form host 192.168.2.3 to web server 192.168.5.2. After applying the rule, the host is unable to access the server. The network administrator runs the output and notices the configuration below: 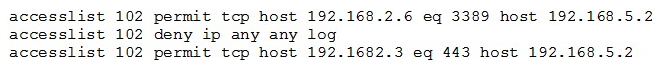 Which of the following rules would be BEST to resolve the issue?
 (Multiple Choice)
4.9/5 (91)
(91) Which of the following are the MAIN reasons why a systems administrator would install security patches in a staging environment before the patches are applied to the production server? (Select two.)
(Multiple Choice)
4.7/5 (80)
(80) A network operations manager has added a second row of server racks in the datacenter. These racks face the opposite direction of the first row of racks. Which of the following is the reason the manager installed the racks this way?
(Multiple Choice)
4.9/5 (76)
(76) An attacker compromises a public CA and issues unauthorized X.509 certificates for Company.com. In the future, Company.com wants to mitigate the impact of similar incidents. Which of the following would assist Company.com with its goal?
(Multiple Choice)
4.9/5 (87)
(87) An information security specialist is reviewing the following output from a Linux server. 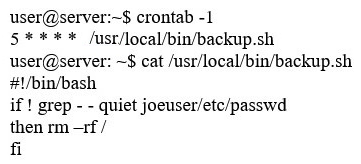 Based on the above information, which of the following types of malware was installed on the server?
 (Multiple Choice)
4.8/5 (86)
(86) During an incident, a company's CIRT determines it is necessary to observe the continued network-based transactions between a callback domain and the malware running on an enterprise PC. Which of the following techniques would be BEST to enable this activity while reducing the risk of lateral spread and the risk that the adversary would notice any changes?
(Multiple Choice)
4.9/5 (90)
(90) Showing 41 - 60 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)