



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


Ann, a user, reported to the service desk that many files on her computer will not open or the contents are not readable. The service desk technician asked Ann if she encountered any strange messages on boot-up or login, and Ann indicated she did not. Which of the following has MOST likely occurred on Ann's computer?
(Multiple Choice)
4.9/5  (86)
(86) A security analyst is updating a BIA document. The security analyst notices the support vendor's time to replace a server hard drive went from eight hours to two hours. Given these new metrics, which of the following can be concluded? (Select TWO)
(Multiple Choice)
4.9/5 (75)
(75) During a recent audit, it was discovered that many services and desktops were missing security patches. Which of the following BEST describes the assessment that was performed to discover this issue?
(Multiple Choice)
4.9/5 (73)
(73) A security administrator is developing controls for creating audit trails and tracking if a PHI data breach is to occur. The administrator has been given the following requirements: All access must be correlated to a user account. All user accounts must be assigned to a single individual. User access to the PHI data must be recorded. Anomalies in PHI data access must be reported. Logs and records cannot be deleted or modified. Which of the following should the administrator implement to meet the above requirements? (Select three.)
(Multiple Choice)
4.8/5 (80)
(80) When attempting to secure a mobile workstation, which of the following authentication technologies rely on the user's physical characteristics? (Select TWO)
(Multiple Choice)
4.7/5 (82)
(82) Which of the following BEST describes an important security advantage yielded by implementing vendor diversity?
(Multiple Choice)
4.8/5 (82)
(82) An administrator thinks the UNIX systems may be compromised, but a review of system log files provides no useful information. After discussing the situation with the security team, the administrator suspects that the attacker may be altering the log files and removing evidence of intrusion activity. Which of the following actions will help detect attacker attempts to further alter log files?
(Multiple Choice)
4.8/5 (69)
(69) A security administrator wants to implement a logon script that will prevent MITM attacks on the local LAN. Which of the following commands should the security administrator implement within the script to accomplish this task?
(Multiple Choice)
4.9/5 (79)
(79) Which of the following could help detect trespassers in a secure facility? (Select TWO)
(Multiple Choice)
4.9/5 (82)
(82) A network technician needs to monitor and view the websites that are visited by an employee. The employee is connected to a network switch. Which of the following would allow the technician to monitor the employee's web traffic?
(Multiple Choice)
4.8/5 (80)
(80) A security analyst identified an SQL injection attack. Which of the following is the FIRST step in remediating the vulnerability?
(Multiple Choice)
4.7/5 (75)
(75) An organization wants to ensure network access is granted only after a user or device has been authenticated. Which of the following should be used to achieve this objective for both wired and wireless networks?
(Multiple Choice)
4.8/5 (77)
(77) The phones at a business are being replaced with VoIP phones that get plugged in-line between the switch and PC. The voice and data networks still need to be kept separate. Which of the following would allow for this?
(Multiple Choice)
4.9/5 (73)
(73) A large financial services firm recently released information regarding a security breach within its corporate network that began several years before. During the time frame in which the breach occurred, indicators show an attacker gained administrative access to the network through a file download from a social media site and subsequently installed it without the user's knowledge. Since the compromise, the attacker was able to take command and control of the computer systems anonymously while obtaining sensitive corporate and personal employee information. Which of the following methods did the attacker MOST likely use to gain access?
(Multiple Choice)
4.7/5 (90)
(90) Despite having implemented password policies, users continue to set the same weak passwords and reuse old passwords. Which of the following technical controls would help prevent these policy violations? (Choose two.)
(Multiple Choice)
4.8/5 (80)
(80) Ann a security analyst is monitoring the IDS console and noticed multiple connections from an internal host to a suspicious call back domain. Which of the following tools would aid her to decipher the network traffic?
(Multiple Choice)
4.9/5 (71)
(71) A security administrator suspects a MITM attack aimed at impersonating the default gateway is underway. Which of the following tools should the administrator use to detect this attack? (Select two.)
(Multiple Choice)
4.9/5 (88)
(88) Which of the following components of printers and MFDs are MOST likely to be used as vectors of compromise if they are improperly configured?
(Multiple Choice)
4.8/5 (76)
(76) An analyst is reviewing a simple program for potential security vulnerabilities before being deployed to a Windows server. Given the following code: 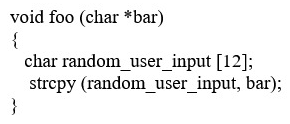 Which of the following vulnerabilities is present?
 (Multiple Choice)
4.7/5 (82)
(82) A systems administrator wants to protect data stored on mobile devices that are used to scan and record assets in a warehouse. The control must automatically destroy the secure container of mobile devices if they leave the warehouse. Which of the following should the administrator implement? (Select two.)
(Multiple Choice)
4.9/5 (76)
(76) Showing 181 - 200 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)