



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A company has noticed multiple instances of proprietary information on public websites. It has also observed an increase in the number of email messages sent to random employees containing malicious links and PDFs. Which of the following changes should the company make to reduce the risks associated with phishing attacks? (Choose two.)
(Multiple Choice)
4.9/5  (91)
(91) The website of a bank that an organization does business with is being reported as untrusted by the organization's web browser. A security analyst has been assigned to investigate. The analyst discovers the bank recently merged with another local bank and combined names. Additionally, the user's bookmark automatically redirects to the website of the newly named bank. Which of the following is the MOST likely cause of the issue?
(Multiple Choice)
5.0/5 (86)
(86) A systems administrator just issued the ssh-keygen -t rsa command on a Linux terminal. Which of the following BEST describes what the rsa portion of the command represents?
(Multiple Choice)
4.8/5 (83)
(83) A user from the financial aid office is having trouble interacting with the finaid directory on the university's ERP system. The systems administrator who took the call ran a command and received the following output: 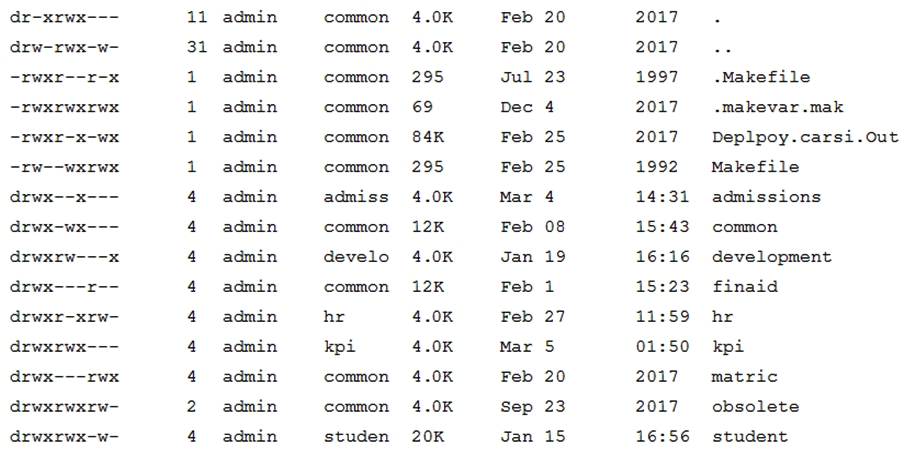 Subsequently, the systems administrator has also confirmed the user is a member of the finaid group on the ERP system. Which of the following is the MOST likely reason for the issue?
 (Multiple Choice)
4.7/5 (86)
(86) Which of the following is used to encrypt web application data?
(Multiple Choice)
4.9/5 (82)
(82) A technician wants to implement PKI-based authentication on an enterprise wireless network. Which of the following should the technician configure to enforce the use of client-side certificates?
(Multiple Choice)
4.8/5 (80)
(80) During a penetration test, the tester performs a preliminary scan for any responsive hosts. Which of the following BEST explains why the tester is doing this?
(Multiple Choice)
4.9/5 (85)
(85) A systems administrator has isolated an infected system from the network and terminated the malicious process from executing. Which of the following should the administrator do NEXT according to the incident response process?
(Multiple Choice)
4.8/5 (83)
(83) Which of the following types of vulnerability scans typically returns more detailed and thorough insights into actual system vulnerabilities?
(Multiple Choice)
4.9/5 (70)
(70) A company is performing an analysis of which corporate units are most likely to cause revenue loss in the event the unit is unable to operate. Which of the following is an element of the BIA that this action is addressing?
(Multiple Choice)
4.8/5 (72)
(72) A systems administrator is increasing the security settings on a virtual host to ensure users on one VM cannot access information from another VM. Which of the following is the administrator protecting against?
(Multiple Choice)
4.9/5 (85)
(85) An analyst generates the following color-coded table shown in the exhibit to help explain the risk of potential incidents in the company. The vertical axis indicates the likelihood of an incident, while the horizontal axis indicates the impact. 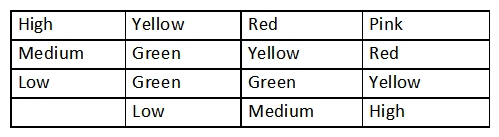 Which of the following is this table an example of?
 (Multiple Choice)
4.9/5 (74)
(74) A security manager is creating an account management policy for a global organization with sales personnel who must access corporate network resources while traveling all over the world. Which of the following practices is the security manager MOST likely to enforce with the policy? (Choose two.)
(Multiple Choice)
4.9/5 (69)
(69) Which of the following are methods to implement HA in a web application server environment? (Select two.)
(Multiple Choice)
4.8/5 (66)
(66) A company recently updated its website to increase sales. The new website uses PHP forms for leads and provides a directory with sales staff and their phone numbers. A systems administrator is concerned with the new website and provides the following log to support the concern: 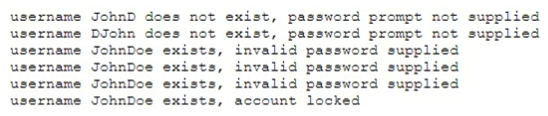 Which of the following is the systems administrator MOST likely to suggest to the Chief Information Security Officer (CISO) based on the above?
 (Multiple Choice)
4.9/5 (78)
(78) An administrator has configured a new Linux server with the FTP service. Upon verifying that the service was configured correctly, the administrator has several users test the FTP service. Users report that they are able to connect to the FTP service and download their personal files, however, they cannot transfer new files to the server. Which of the following will most likely fix the uploading issue for the users?
(Multiple Choice)
4.8/5 (83)
(83) Which of the following methods is used by internal security teams to assess the security of internally developed applications?
(Multiple Choice)
4.8/5 (85)
(85) A security administrator installed a new network scanner that identifies new host systems on the network. Which of the following did the security administrator install?
(Multiple Choice)
4.9/5 (71)
(71) A network administrator is implementing multifactor authentication for employees who travel and use company devices remotely by using the company VPN. Which of the following would provide the required level of authentication?
(Multiple Choice)
4.9/5 (84)
(84) A security administrator is evaluating three different services: radius, diameter, and Kerberos. Which of the following is a feature that is UNIQUE to Kerberos?
(Multiple Choice)
4.9/5 (76)
(76) Showing 301 - 320 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)