



 Chat with AI
Exam 15: CompTIA Security+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An attacker discovers a new vulnerability in an enterprise application. The attacker takes advantage of the vulnerability by developing new malware. After installing the malware, the attacker is provided with access to the infected machine. Which of the following is being described?
(Multiple Choice)
4.8/5  (79)
(79) Which of the following must be intact for evidence to be admissible in court?
(Multiple Choice)
4.9/5 (79)
(79) Which of the following locations contain the MOST volatile data?
(Multiple Choice)
4.9/5 (82)
(82) Which of the following could occur when both strong and weak ciphers are configured on a VPN concentrator? (Select TWO)
(Multiple Choice)
4.9/5 (77)
(77) A bank requires tellers to get manager approval when a customer wants to open a new account. A recent audit shows that there have been four cases in the previous year where tellers opened accounts without management approval. The bank president thought separation of duties would prevent this from happening. In order to implement a true separation of duties approach the bank could:
(Multiple Choice)
4.8/5 (81)
(81) A company is deploying a new VoIP phone system. They require 99.999% uptime for their phone service and are concerned about their existing data network interfering with the VoIP phone system. The core switches in the existing data network are almost fully saturated. Which of the following options will pro-vide the best performance and availability for both the VoIP traffic, as well as the traffic on the existing data network?
(Multiple Choice)
4.9/5 (79)
(79) A systems administrator wants to implement a secure wireless network requiring wireless clients to pre-register with the company and install a PKI client certificate prior to being able to connect to the wireless network. Which of the following should the systems administrator configure?
(Multiple Choice)
4.8/5 (79)
(79) A law firm wants to protect its customers' individual information, which is stored at a remote facility, from inadvertently being compromised through a violation of the security objectives. Which of the following BEST describes the customer information that is being stored at this facility?
(Multiple Choice)
4.8/5 (71)
(71) Attackers have been using revoked certificates for MITM attacks to steal credentials from employees of Company.com. Which of the following options should Company.com implement to mitigate these attacks?
(Multiple Choice)
4.9/5 (72)
(72) A security analyst is reviewing the following output from an IPS: 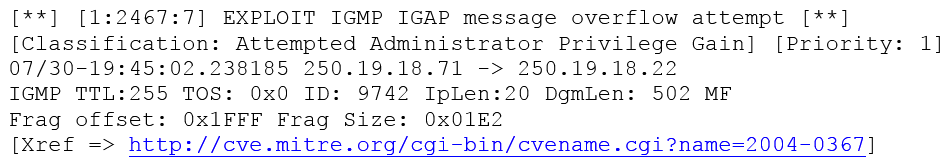 Given this output, which of the following can be concluded? (Choose two.)
 (Multiple Choice)
4.7/5 (86)
(86) A security analyst received an after-hours alert indicating that a large number of accounts with the suffix "admin" were locked out. The accounts were all locked out after five unsuccessful login attempts, and no other accounts on the network triggered the same alert. Which of the following is the BEST explanation for these alerts?
(Multiple Choice)
4.8/5 (75)
(75) Which of the following strategies helps reduce risk if a rollback is needed when upgrading a critical system platform?
(Multiple Choice)
4.7/5 (77)
(77) An organization has the following password policies: Passwords must be at least 16 characters long. A password cannot be the same as any previous 20 passwords. Three failed login attempts will lock the account for five minutes. Passwords must have one uppercase letter, one lowercase letter, and one non-alphanumeric symbol. A database server was recently breached, and the incident response team suspects the passwords were compromised. Users with permission on that database server were forced to change their passwords for that server. Unauthorized and suspicious logins are now being detected on a completely separate server. Which of the following is MOST likely the issue and the best solution?
(Multiple Choice)
4.8/5 (69)
(69) A security analyst is hardening a web server, which should allow a secure certificate-based session using the organization's PKI infrastructure. The web server should also utilize the latest security techniques and standards. Given this set of requirements, which of the following techniques should the analyst implement to BEST meet these requirements? (Select two.)
(Multiple Choice)
4.7/5 (70)
(70) An organization plans to transition the intrusion detection and prevention techniques on a critical subnet to an anomaly-based system. Which of the following does the organization need to determine for this to be successful?
(Multiple Choice)
4.8/5 (85)
(85) Which of the following AES modes of operation provide authentication? (Select two.)
(Multiple Choice)
4.9/5 (74)
(74) A recent internal audit is forcing a company to review each internal business unit's VMs because the cluster they are installed on is in danger of running out of computer resources. Which of the following vulnerabilities exist?
(Multiple Choice)
4.9/5 (75)
(75) A systems administrator is auditing the company's Active Directory environment. It is quickly noted that the username "company\bsmith" is interactively logged into several desktops across the organization. Which of the following has the systems administrator MOST likely come across?
(Multiple Choice)
4.8/5 (87)
(87) After a routine audit, a company discovers that engineering documents have been leaving the network on a particular port. The company must allow outbound traffic on this port, as it has a legitimate business use. Blocking the port would cause an outage. Which of the following technology controls should the company implement?
(Multiple Choice)
4.8/5 (82)
(82) Showing 821 - 840 of 1164

Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)