Multiple Choice
A security analyst has received several reports of an issue on an internal web application. Users state they are having to provide their credentials twice to log in. The analyst checks with the application team and notes this is not an expected behavior. After looking at several logs, the analyst decides to run some commands on the gateway and obtains the following output: 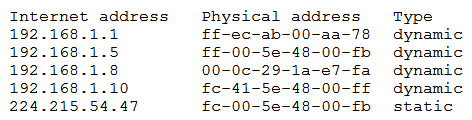 Which of the following BEST describes the attack the company is experiencing?
A) MAC flooding
B) URL redirection
C) ARP poisoning
D) DNS hijacking
Correct Answer:

Verified
Correct Answer:
Verified
Q210: If two employees are encrypting traffic between
Q211: A security researcher is tracking an adversary
Q212: Which of the following is a reason
Q213: A security consultant was asked to revise
Q214: A security analyst is doing a vulnerability
Q216: A company has a data system with
Q217: An organization finds that most help desk
Q218: Which of the following is commonly used
Q219: When a malicious user is able to
Q220: A systems administrator is implementing a remote