Multiple Choice
After being alerted to potential anomalous activity related to trivial DNS lookups, a security analyst looks at the following output of implemented firewall rules: 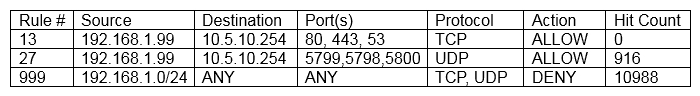 The analyst notices that the expected policy has no hit count for the day. Which of the following MOST likely occurred?
A) Data execution prevention is enabled.
B) The VLAN is not trunked properly.
C) There is a policy violation for DNS lookups.
D) The firewall policy is misconfigured.
Correct Answer:

Verified
Correct Answer:
Verified
Q609: Which of the following is the BEST
Q610: A company occupies the third floor of
Q611: A third-party penetration testing company was able
Q612: Joe recently assumed the role of data
Q613: A security analyst is securing smartphones and
Q615: An employee uses RDP to connect back
Q616: A security team has completed the installation
Q617: Despite having implemented password policies, users continue
Q618: A security administrator is diagnosing a server
Q619: A new Chief Information Officer (CIO) has