Multiple Choice
A security analyst has received the following alert snippet from the HIDS appliance: 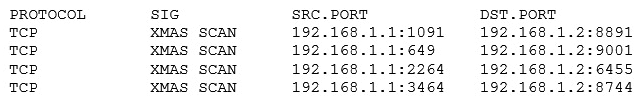 Given the above logs, which of the following is the cause of the attack?
A) The TCP ports on destination are all open
B) FIN, URG, and PSH flags are set in the packet header
C) TCP MSS is configured improperly
D) There is improper Layer 2 segmentation
Correct Answer:

Verified
Correct Answer:
Verified
Q1127: Which of the following access management concepts
Q1128: A security technician has been receiving alerts
Q1129: An organization handling highly confidential information needs
Q1130: A supervisor in your organization was demoted
Q1131: Joe notices there are several user accounts
Q1133: A company is deploying smartphones for its
Q1134: An analyst is currently looking at the
Q1135: A company is terminating an employee for
Q1136: Which of the following metrics are used
Q1137: A chief Financial Officer (CFO) has asked