



 Chat with AI
Exam 5: CompTIA Cloud Essentials+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A security analyst is trying to determine if a host is active on a network. The analyst first attempts the following: 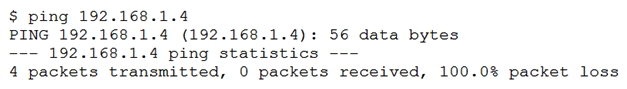 The analyst runs the following command next:
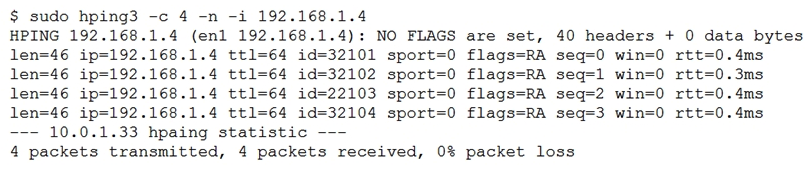 Which of the following would explain the difference in results?
The analyst runs the following command next: Which of the following would explain the difference in results? (Multiple Choice)
4.9/5  (83)
(83) A cybersecurity analyst is investigating a potential incident affecting multiple systems on a company's internal network. Although there is a negligible impact to performance, the following symptoms are present on each of the affected systems: Existence of a new and unexpected svchost.exe process Persistent, outbound TCP/IP connections to an unknown external host with routine keep-alives transferred DNS query logs showing successful name resolution for an Internet-resident dynamic DNS domain If this situation remains unresolved, which of the following will MOST likely occur?
(Multiple Choice)
4.8/5 (85)
(85) A security analyst discovers accounts in sensitive SaaS-based systems are not being removed in a timely manner when an employee leaves the organization. To BEST resolve the issue, the organization should implement:
(Multiple Choice)
4.9/5 (75)
(75) Bootloader malware was recently discovered on several company workstations. All the workstations run Windows and are current models with UEFI capability. Which of the following UEFI settings is the MOST likely cause of the infections?
(Multiple Choice)
5.0/5 (71)
(71) During a cyber incident, which of the following is the BEST course of action?
(Multiple Choice)
4.9/5 (78)
(78) Because some clients have reported unauthorized activity on their accounts, a security analyst is reviewing network packet captures from the company's API server. A portion of a capture file is shown below: POST /services/v1_0/Public/Members.svc/soap <s:Envelope+xmlns:s="http://schemas.s/soap/envelope/"><s:Body><GetIPLocation+xmlns="http://tempuri.org/ "> <request+xmlns:a=" http://schemas.somesite.org "+xmlns:i=" http://www.w3.org/2001/XMLSchema-instance "></s:Body></s:Envelope> 192.168.1.22 - - api.somesite.com 200 0 1006 1001 0 192.168.1.22 POST /services/v1_0/Public/Members.svc/soap <<a:Password>Password123</a:Password><a:ResetPasswordToken+i:nil="true"/> <a:ShouldImpersonatedAuthenticationBePopulated+i:nil="true"/><a:Username>somebody@companyname.com</a:Username></request></Login></s:Body></s:Envelope> 192.168.5.66 - - api.somesite.com 200 0 11558 1712 2024 192.168.4.89 POST /services/v1_0/Public/Members.svc/soap <s:Envelope+xmlns:s=" http://schemas.xmlsoap.org/soap/envelope/ "><s:Body><GetIPLocation+xmlns=" http://tempuri.org/"> <a:IPAddress>516.7.446.605</a:IPAddress><a:ZipCode+i:nil="true"/></request></GetIPLocation></s:Body></s:Envelope> 192.168.1.22 - - api.somesite.com 200 0 1003 1011 307 192.168.1.22 "><s:Body><IsLoggedIn+xmlns=" http://tempuri.org/ "> <request+xmlns:a=" http://schemas.datacontract.org/2004/07/somesite.web +xmlns:i=" "><a:Authentication> <a:ApiToken>kmL4krg2CwwWBan5BReGv5Djb7syxXTNKcWFuSjd</a:ApiToken><a:ImpersonateUserId>0</a:ImpersonateUserId><a:LocationId>161222</a:LocationId> <a:NetworkId>4</a:NetworkId><a:ProviderId>''1=1</a:ProviderId><a:UserId>13026046</a:UserId></a:Authentication></request></IsLoggedIn></s:Body></s:Envelope> 192.168.5.66 - - api.somesite.com 200 0 1378 1209 48 192.168.4.89 Which of the following MOST likely explains how the clients' accounts were compromised?
(Multiple Choice)
4.8/5 (77)
(77) A security analyst recently used Arachni to perform a vulnerability assessment of a newly developed web application. The analyst is concerned about the following output: 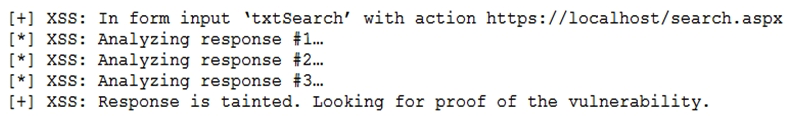 Which of the following is the MOST likely reason for this vulnerability?
 (Multiple Choice)
4.9/5 (74)
(74) A security analyst suspects a malware infection was caused by a user who downloaded malware after clicking http://<malwaresource>/a.php in a phishing email. To prevent other computers from being infected by the same malware variation, the analyst should create a rule on the __________.
(Multiple Choice)
4.8/5 (93)
(93) It is important to parameterize queries to prevent __________.
(Multiple Choice)
4.8/5 (79)
(79) A security analyst discovers a vulnerability on an unpatched web server that is used for testing machine learning on Big Data sets. Exploitation of the vulnerability could cost the organization $1.5 million in lost productivity. The server is located on an isolated network segment that has a 5% chance of being compromised. Which of the following is the value of this risk?
(Multiple Choice)
4.8/5 (81)
(81) An organization wants to move non-essential services into a cloud computing environment. Management has a cost focus and would like to achieve a recovery time objective of 12 hours. Which of the following cloud recovery strategies would work BEST to attain the desired outcome?
(Multiple Choice)
4.8/5 (70)
(70) A security analyst is reviewing the following log from an email security service. 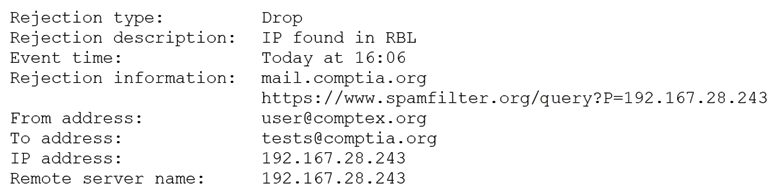 Which of the following BEST describes the reason why the email was blocked?
 (Multiple Choice)
4.7/5 (84)
(84) As part of an exercise set up by the information security officer, the IT staff must move some of the network systems to an off-site facility and redeploy them for testing. All staff members must ensure their respective systems can power back up and match their gold image. If they find any inconsistencies, they must formally document the information. Which of the following BEST describes this test?
(Multiple Choice)
4.7/5 (83)
(83) A security analyst is reviewing vulnerability scan results and notices new workstations are being flagged as having outdated antivirus signatures. The analyst observes the following plugin output: Antivirus is installed on the remote host: Installation path: C:\Program Files\AVProduct\Win32\ Product Engine: 14.12.101 Engine Version: 3.5.71 Scanner does not currently have information about AVProduct version 3.5.71. It may no longer be supported. The engine version is out of date. The oldest supported version from the vendor is 4.2.11. The analyst uses the vendor's website to confirm the oldest supported version is correct. Which of the following BEST describes the situation?
(Multiple Choice)
4.7/5 (78)
(78) A cybersecurity analyst has access to several threat feeds and wants to organize them while simultaneously comparing intelligence against network traffic. Which of the following would BEST accomplish this goal?
(Multiple Choice)
4.7/5 (87)
(87) A security analyst discovered a specific series of IP addresses that are targeting an organization. None of the attacks have been successful. Which of the following should the security analyst perform NEXT?
(Multiple Choice)
4.8/5 (70)
(70) An analyst has been asked to provide feedback regarding the controls required by a revised regulatory framework. At this time, the analyst only needs to focus on the technical controls. Which of the following should the analyst provide an assessment of?
(Multiple Choice)
4.9/5 (89)
(89) An incident response team is responding to a breach of multiple systems that contain PII and PHI. Disclosing the incident to external entities should be based on:
(Multiple Choice)
4.9/5 (71)
(71) While preparing for an audit of information security controls in the environment, an analyst outlines a framework control that has the following requirements: All sensitive data must be classified. All sensitive data must be purged on a quarterly basis. Certificates of disposal must remain on file for at least three years. This framework control is MOST likely classified as:
(Multiple Choice)
4.9/5 (75)
(75) During an investigation, a security analyst identified machines that are infected with malware the antivirus was unable to detect. Which of the following is the BEST place to acquire evidence to perform data carving?
(Multiple Choice)
4.8/5 (85)
(85) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)