



 Chat with AI
Exam 5: CompTIA Cloud Essentials+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


During an investigation, an analyst discovers the following rule in an executive's email client: IF * TO <executive@anycompany.com> THEN mailto: <someaddress@domain.com> SELECT FROM 'sent' THEN DELETE FROM <executive@anycompany.com> The executive is not aware of this rule. Which of the following should the analyst do FIRST to evaluate the potential impact of this security incident?
(Multiple Choice)
5.0/5  (79)
(79) A security analyst is investigating malicious traffic from an internal system that attempted to download proxy avoidance as identified from the firewall logs, but the destination IP is blocked and not captured. Which of the following should the analyst do?
(Multiple Choice)
4.9/5 (89)
(89) A Chief Information Security Officer (CISO) is concerned the development team, which consists of contractors, has too much access to customer data. Developers use personal workstations, giving the company little to no visibility into the development activities. Which of the following would be BEST to implement to alleviate the CISO's concern?
(Multiple Choice)
4.9/5 (77)
(77) A security team wants to make SaaS solutions accessible from only the corporate campus. Which of the following would BEST accomplish this goal?
(Multiple Choice)
4.9/5 (78)
(78) A small electronics company decides to use a contractor to assist with the development of a new FPGA-based device. Several of the development phases will occur off-site at the contractor's labs. Which of the following is the main concern a security analyst should have with this arrangement?
(Multiple Choice)
4.8/5 (83)
(83) A security analyst wants to identify which vulnerabilities a potential attacker might initially exploit if the network is compromised. Which of the following would provide the BEST results?
(Multiple Choice)
4.7/5 (96)
(96) A security analyst is investigating a system compromise. The analyst verifies the system was up to date on OS patches at the time of the compromise. Which of the following describes the type of vulnerability that was MOST likely exploited?
(Multiple Choice)
4.7/5 (75)
(75) A threat feed notes malicious actors have been infiltrating companies and exfiltrating data to a specific set of domains. Management at an organization wants to know if it is a victim. Which of the following should the security analyst recommend to identify this behavior without alerting any potential malicious actors?
(Multiple Choice)
4.8/5 (70)
(70) A finance department employee has received a message that appears to have been sent from the Chief Financial Officer (CFO), asking the employee to perform a wire transfer. Analysis of the email shows the message came from an external source and is fraudulent. Which of the following would work BEST to improve the likelihood of employees quickly recognizing fraudulent emails?
(Multiple Choice)
4.9/5 (80)
(80) A Chief Information Security Officer (CISO) is concerned developers have too much visibility into customer data. Which of the following controls should be implemented to BEST address these concerns?
(Multiple Choice)
4.9/5 (63)
(63) A network attack that is exploiting a vulnerability in the SNMP is detected. Which of the following should the cybersecurity analyst do FIRST?
(Multiple Choice)
4.8/5 (75)
(75) A cybersecurity analyst is supporting an incident response effort via threat intelligence. Which of the following is the analyst MOST likely executing?
(Multiple Choice)
4.8/5 (66)
(66) A security analyst is conducting a post-incident log analysis to determine which indicators can be used to detect further occurrences of a data exfiltration incident. The analyst determines backups were not performed during this time and reviews the following: 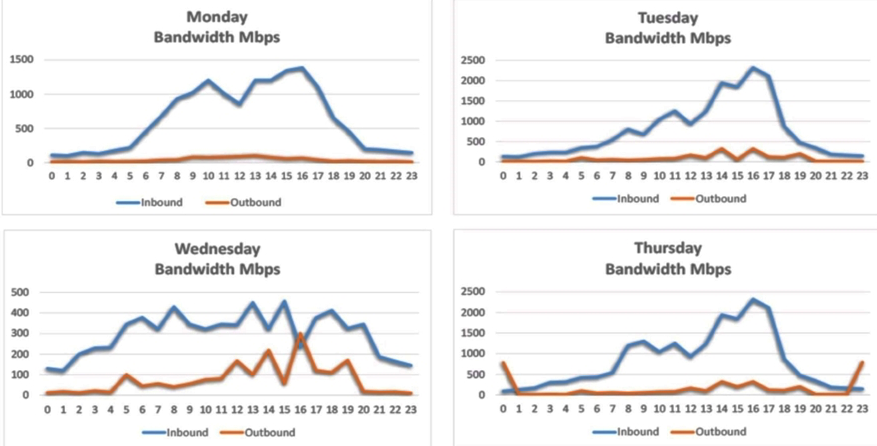 Which of the following should the analyst review to find out how the data was exfiltrated?
 (Multiple Choice)
4.9/5 (73)
(73) A cybersecurity analyst needs to rearchitect the network using a firewall and a VPN server to achieve the highest level of security. To BEST complete this task, the analyst should place the:
(Multiple Choice)
4.9/5 (70)
(70) A security analyst is evaluating two vulnerability management tools for possible use in an organization. The analyst set up each of the tools according to the respective vendor's instructions and generated a report of vulnerabilities that ran against the same target server. Tool A reported the following: 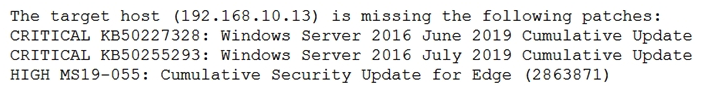 Tool B reported the following:
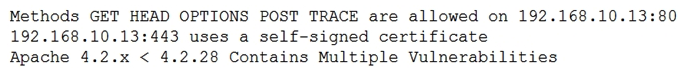 Which of the following BEST describes the method used by each tool? (Choose two.)
Tool B reported the following: Which of the following BEST describes the method used by each tool? (Choose two.) (Multiple Choice)
4.8/5 (90)
(90) Which of the following types of policies is used to regulate data storage on the network?
(Multiple Choice)
4.8/5 (91)
(91) An information security analyst is compiling data from a recent penetration test and reviews the following output: 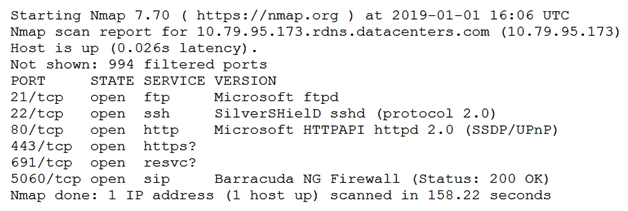 The analyst wants to obtain more information about the web-based services that are running on the target. Which of the following commands would MOST likely provide the needed information?
 (Multiple Choice)
4.7/5 (76)
(76) A company was recently awarded several large government contracts and wants to determine its current risk from one specific APT. Which of the following threat modeling methodologies would be the MOST appropriate to use during this analysis?
(Multiple Choice)
4.7/5 (85)
(85) During an investigation, a security analyst determines suspicious activity occurred during the night shift over the weekend. Further investigation reveals the activity was initiated from an internal IP going to an external website. Which of the following would be the MOST appropriate recommendation to prevent the activity from happening in the future?
(Multiple Choice)
4.9/5 (79)
(79) A developer wrote a script to make names and other PII data unidentifiable before loading a database export into the testing system. Which of the following describes the type of control that is being used?
(Multiple Choice)
4.7/5 (94)
(94) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)