



 Chat with AI
Exam 5: CompTIA Cloud Essentials+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A team of security analysts has been alerted to potential malware activity. The initial examination indicates one of the affected workstations is beaconing on TCP port 80 to five IP addresses and attempting to spread across the network over port 445. Which of the following should be the team's NEXT step during the detection phase of this response process?
(Multiple Choice)
4.9/5  (88)
(88) A Chief Security Officer (CSO) is working on the communication requirements for an organization's incident response plan. In addition to technical response activities, which of the following is the main reason why communication must be addressed in an effective incident response program?
(Multiple Choice)
4.8/5 (82)
(82) A security analyst received an alert from the SIEM indicating numerous login attempts from users outside their usual geographic zones, all of which were initiated through the web-based mail server. The logs indicate all domain accounts experienced two login attempts during the same time frame. Which of the following is the MOST likely cause of this issue?
(Multiple Choice)
4.8/5 (87)
(87) For machine learning to be applied effectively toward security analysis automation, it requires __________.
(Multiple Choice)
4.7/5 (82)
(82) A large amount of confidential data was leaked during a recent security breach. As part of a forensic investigation, the security team needs to identify the various types of traffic that were captured between two compromised devices. Which of the following should be used to identify the traffic?
(Multiple Choice)
4.9/5 (91)
(91) While analyzing logs from a WAF, a cybersecurity analyst finds the following: "GET /form.php?id=463225%2b%2575%256e%2569%256f%256e%2b%2573%2574%2box3133333731,1223,1224&name=&state=IL" Which of the following BEST describes what the analyst has found?
(Multiple Choice)
4.8/5 (74)
(74) Which of the following software assessment methods would be BEST for gathering data related to an application's availability during peak times?
(Multiple Choice)
4.8/5 (86)
(86) An analyst is searching a log for potential credit card leaks. The log stores all data encoded in hexadecimal. Which of the following commands will allow the security analyst to confirm the incident?
(Multiple Choice)
4.8/5 (73)
(73) A compliance officer of a large organization has reviewed the firm's vendor management program but has discovered there are no controls defined to evaluate third-party risk or hardware source authenticity. The compliance officer wants to gain some level of assurance on a recurring basis regarding the implementation of controls by third parties. Which of the following would BEST satisfy the objectives defined by the compliance officer? (Choose two.)
(Multiple Choice)
4.9/5 (71)
(71) A large organization wants to move account registration services to the cloud to benefit from faster processing and elasticity. Which of the following should be done FIRST to determine the potential risk to the organization?
(Multiple Choice)
4.8/5 (75)
(75) As part of a review of incident response plans, which of the following is MOST important for an organization to understand when establishing the breach notification period?
(Multiple Choice)
4.8/5 (89)
(89) An analyst is performing penetration testing and vulnerability assessment activities against a new vehicle automation platform. Which of the following is MOST likely an attack vector that is being utilized as part of the testing and assessment?
(Multiple Choice)
4.9/5 (59)
(59) A security analyst recently discovered two unauthorized hosts on the campus's wireless network segment from a man-in-the-middle attack. The security analyst also verified that privileges were not escalated, and the two devices did not gain access to other network devices. Which of the following would BEST mitigate and improve the security posture of the wireless network for this type of attack?
(Multiple Choice)
5.0/5 (68)
(68) Which of the following policies would state an employee should not disable security safeguards, such as host firewalls and antivirus, on company systems?
(Multiple Choice)
4.9/5 (84)
(84) A security analyst received a series of antivirus alerts from a workstation segment, and users reported ransomware messages. During lessons-learned activities, the analyst determines the antivirus was able to alert to abnormal behavior but did not stop this newest variant of ransomware. Which of the following actions should be taken to BEST mitigate the effects of this type of threat in the future?
(Multiple Choice)
4.9/5 (70)
(70) A financial institution's business unit plans to deploy a new technology in a manner that violates existing information security standards. Which of the following actions should the Chief Information Security Officer (CISO) take to manage any type of violation?
(Multiple Choice)
4.9/5 (78)
(78) After a breach involving the exfiltration of a large amount of sensitive data, a security analyst is reviewing the following firewall logs to determine how the breach occurred: 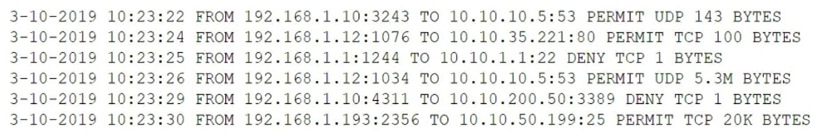 Which of the following IP addresses does the analyst need to investigate further?
 (Multiple Choice)
4.9/5 (87)
(87) A company's marketing emails are either being found in a spam folder or not being delivered at all. The security analyst investigates the issue and discovers the emails in question are being sent on behalf of the company by a third party, mail.marketing.com. Below is the existing SPF record: v=spf1 a mx -all Which of the following updates to the SPF record will work BEST to prevent the emails from being marked as spam or blocked?
(Multiple Choice)
4.7/5 (78)
(78) An information security analyst discovered a virtual machine server was compromised by an attacker. Which of the following should be the FIRST step to confirm and respond to the incident?
(Multiple Choice)
4.8/5 (80)
(80) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)