



 Chat with AI
Exam 5: CompTIA Cloud Essentials+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


A security analyst on the threat-hunting team has developed a list of unneeded, benign services that are currently running as part of the standard OS deployment for workstations. The analyst will provide this list to the operations team to create a policy that will automatically disable the services for all workstations in the organization. Which of the following BEST describes the security analyst's goal?
(Multiple Choice)
4.9/5  (84)
(84) A security manager has asked an analyst to provide feedback on the results of a penetration test. After reviewing the results, the manager requests information regarding the possible exploitation of vulnerabilities. Which of the following information data points would be MOST useful for the analyst to provide to the security manager, who would then communicate the risk factors to senior management? (Choose two.)
(Multiple Choice)
5.0/5 (87)
(87) A security analyst has been alerted to several emails that show evidence an employee is planning malicious activities that involve employee PII on the network before leaving the organization. The security analyst's BEST response would be to coordinate with the legal department and:
(Multiple Choice)
4.9/5 (84)
(84) A cybersecurity analyst is reading a daily intelligence digest of new vulnerabilities. The type of vulnerability that should be disseminated FIRST is one that:
(Multiple Choice)
4.8/5 (75)
(75) A development team signed a contract that requires access to an on-premises physical server. Access must be restricted to authorized users only and cannot be connected to the Internet. Which of the following solutions would meet this requirement?
(Multiple Choice)
4.8/5 (94)
(94) Which of the following software security best practices would prevent an attacker from being able to run arbitrary SQL commands within a web application? (Choose two.)
(Multiple Choice)
4.8/5 (78)
(78) A security analyst is investigating a malware infection that occurred on a Windows system. The system was not connected to a network and had no wireless capability. Company policy prohibits using portable media or mobile storage. The security analyst is trying to determine which user caused the malware to get onto the system. Which of the following registry keys would MOST likely have this information?
(Multiple Choice)
4.9/5 (88)
(88) A development team is testing a new application release. The team needs to import existing client PHI data records from the production environment to the test environment to test accuracy and functionality. Which of the following would BEST protect the sensitivity of this data while still allowing the team to perform the testing?
(Multiple Choice)
4.9/5 (87)
(87) A bad actor bypasses authentication and reveals all records in a database through an SQL injection. Implementation of which of the following would work BEST to prevent similar attacks in the future?
(Multiple Choice)
4.9/5 (98)
(98) A monthly job to install approved vendor software updates and hot fixes recently stopped working. The security team performed a vulnerability scan, which identified several hosts as having some critical OS vulnerabilities, as referenced in the common vulnerabilities and exposures (CVE) database. Which of the following should the security team do NEXT to resolve the critical findings in the most effective manner? (Choose two.)
(Multiple Choice)
4.8/5 (90)
(90) An information security analyst observes anomalous behavior on the SCADA devices in a power plant. This behavior results in the industrial generators overheating and destabilizing the power supply. Which of the following would BEST identify potential indicators of compromise?
(Multiple Choice)
4.9/5 (77)
(77) A security analyst is investigating a compromised Linux server. The analyst issues the ps command and receives the following output: 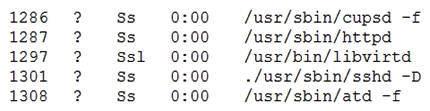 Which of the following commands should the administrator run NEXT to further analyze the compromised system?
 (Multiple Choice)
4.9/5 (79)
(79) The security team at a large corporation is helping the payment-processing team to prepare for a regulatory compliance audit and meet the following objectives: Reduce the number of potential findings by the auditors. Limit the scope of the audit to only devices used by the payment-processing team for activities directly impacted by the regulations. Prevent the external-facing web infrastructure used by other teams from coming into scope. Limit the amount of exposure the company will face if the systems used by the payment-processing team are compromised. Which of the following would be the MOST effective way for the security team to meet these objectives?
(Multiple Choice)
4.8/5 (91)
(91) Which of the following are components of the intelligence cycle? (Choose two.)
(Multiple Choice)
4.9/5 (82)
(82) When attempting to do a stealth scan against a system that does not respond to ping, which of the following Nmap commands BEST accomplishes that goal?
(Multiple Choice)
4.8/5 (87)
(87) A cybersecurity analyst is contributing to a team hunt on an organization's endpoints. Which of the following should the analyst do FIRST?
(Multiple Choice)
4.8/5 (80)
(80) While planning segmentation for an ICS environment, a security engineer determines IT resources will need access to devices within the ICS environment without compromising security. To provide the MOST secure access model in this scenario, the jumpbox should be __________.
(Multiple Choice)
4.8/5 (82)
(82) Given the Nmap request below: 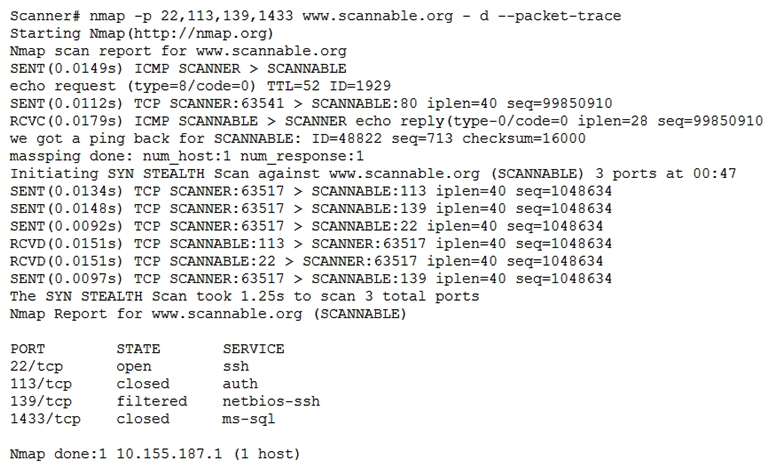 Which of the following actions will an attacker be able to initiate directly against this host?
 (Multiple Choice)
4.9/5 (83)
(83) A security analyst gathered forensics from a recent intrusion in preparation for legal proceedings. The analyst used EnCase to gather the digital forensics, cloned the hard drive, and took the hard drive home for further analysis. Which of the following did the security analyst violate?
(Multiple Choice)
4.9/5 (75)
(75) An audit has revealed an organization is utilizing a large number of servers that are running unsupported operating systems. As part of the management response phase of the audit, which of the following would BEST demonstrate senior management is appropriately aware of and addressing the issue?
(Multiple Choice)
4.8/5 (92)
(92) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)