



 Chat with AI
Exam 5: CompTIA Cloud Essentials+

Exam 1: CompTIA A+ Certification Exam: Core 1471 Questions
Exam 2: CompTIA A+ Certification Exam: Core 2409 Questions
Exam 3: CompTIA Advanced Security Practitioner (CASP+) CAS-003442 Questions
Exam 4: CompTIA Advanced Security Practitioner (CASP+) CAS-004107 Questions
Exam 5: CompTIA Cloud Essentials+165 Questions
Exam 6: CompTIA CySA+ Certification Exam (CS0-002)294 Questions
Exam 7: CompTIA Cloud+ (CV0-002)48 Questions
Exam 8: CompTIA Cloud+67 Questions
Exam 9: CompTIA IT Fundamentals387 Questions
Exam 10: CompTIA Network+829 Questions
Exam 11: CompTIA Project+540 Questions
Exam 12: CompTIA PenTest+ Certification Exam165 Questions
Exam 13: CompTIA Server+66 Questions
Exam 14: CompTIA Server+ Certification Exam779 Questions
Exam 15: CompTIA Security+1 k+ Questions
Exam 16: CompTIA Security+ 2021129 Questions
Exam 17: CompTIA CTT+ Essentials378 Questions
Exam 18: CompTIA Linux+252 Questions
Select questions type


An executive assistant wants to onboard a new cloud-based product to help with business analytics and dashboarding. Which of the following would be the BEST integration option for this service?
(Multiple Choice)
4.8/5  (84)
(84) An analyst performs a routine scan of a host using Nmap and receives the following output: 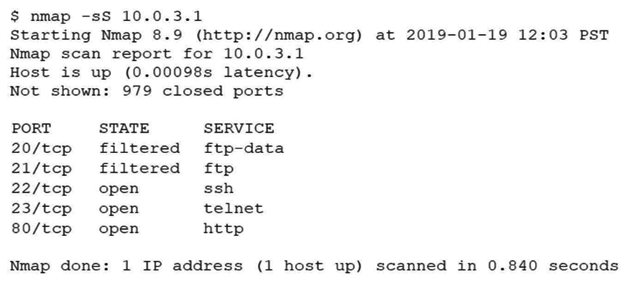 Which of the following should the analyst investigate FIRST?
 (Multiple Choice)
4.9/5 (80)
(80) Which of the following would a security engineer recommend to BEST protect sensitive system data from being accessed on mobile devices?
(Multiple Choice)
4.8/5 (92)
(92) A cyber-incident response analyst is investigating a suspected cryptocurrency miner on a company's server. Which of the following is the FIRST step the analyst should take?
(Multiple Choice)
4.9/5 (82)
(82) An analyst is participating in the solution analysis process for a cloud-hosted SIEM platform to centralize log monitoring and alerting capabilities in the SOC. Which of the following is the BEST approach for supply chain assessment when selecting a vendor?
(Multiple Choice)
4.9/5 (77)
(77) A Chief Information Security Officer (CISO) wants to upgrade an organization's security posture by improving proactive activities associated with attacks from internal and external threats. Which of the following is the MOST proactive tool or technique that feeds incident response capabilities?
(Multiple Choice)
4.7/5 (78)
(78) Which of the following BEST articulates the benefit of leveraging SCAP in an organization's cybersecurity analysis toolset?
(Multiple Choice)
4.8/5 (76)
(76) During a review of vulnerability scan results, an analyst determines the results may be flawed because a control-baseline system, which is used to evaluate a scanning tool's effectiveness, was reported as not vulnerable. Consequently, the analyst verifies the scope of the scan included the control-baseline host, which was available on the network during the scan. The use of a control-baseline endpoint in this scenario assists the analyst in confirming:
(Multiple Choice)
4.8/5 (70)
(70) Which of the following sources would a security analyst rely on to provide relevant and timely threat information concerning the financial services industry?
(Multiple Choice)
4.8/5 (70)
(70) An information security analyst on a threat-hunting team is working with administrators to create a hypothesis related to an internally developed web application. The working hypothesis is as follows: Due to the nature of the industry, the application hosts sensitive data associated with many clients and is a significant target. The platform is most likely vulnerable to poor patching and inadequate server hardening, which expose vulnerable services. The application is likely to be targeted with SQL injection attacks due to the large number of reporting capabilities within the application. As a result, the systems administrator upgrades outdated service applications and validates the endpoint configuration against an industry benchmark. The analyst suggests developers receive additional training on implementing identity and access management, and also implements a WAF to protect against SQL injection attacks. Which of the following BEST represents the technique in use?
(Multiple Choice)
4.8/5 (79)
(79) A pharmaceutical company's marketing team wants to send out notifications about new products to alert users of recalls and newly discovered adverse drug reactions. The team plans to use the names and mailing addresses that users have provided. Which of the following data privacy standards does this violate?
(Multiple Choice)
4.9/5 (86)
(86) An analyst is working with a network engineer to resolve a vulnerability that was found in a piece of legacy hardware, which is critical to the operation of the organization's production line. The legacy hardware does not have third-party support, and the OEM manufacturer of the controller is no longer in operation. The analyst documents the activities and verifies these actions prevent remote exploitation of the vulnerability. Which of the following would be the MOST appropriate to remediate the controller?
(Multiple Choice)
4.8/5 (71)
(71) A security analyst is reviewing a web application. If an unauthenticated user tries to access a page in the application, the user is redirected to the login page. After successful authentication, the user is then redirected back to the original page. Some users have reported receiving phishing emails with a link that takes them to the application login page but then redirects to a fake login page after successful authentication. Which of the following will remediate this software vulnerability?
(Multiple Choice)
4.9/5 (90)
(90) A security analyst is scanning the network to determine if a critical security patch was applied to all systems in an enterprise. The organization has a very low tolerance for risk when it comes to resource availability. Which of the following is the BEST approach for configuring and scheduling the scan?
(Multiple Choice)
4.9/5 (63)
(63) Which of the following would MOST likely be included in the incident response procedure after a security breach of customer PII?
(Multiple Choice)
4.9/5 (98)
(98) Which of the following sets of attributes BEST illustrates the characteristics of an insider threat from a security perspective?
(Multiple Choice)
4.9/5 (83)
(83) A security analyst is reviewing the following log entries to identify anomalous activity: 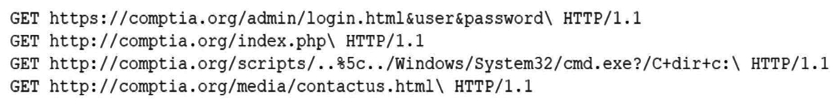 Which of the following attack types is occurring?
 (Multiple Choice)
4.7/5 (74)
(74) A company is moving from the use of web servers hosted in an internal datacenter to a containerized cloud platform. An analyst has been asked to identify indicators of compromise in the containerized environment. Which of the following would BEST indicate a running container has been compromised?
(Multiple Choice)
4.8/5 (80)
(80) An analyst is reviewing the following code output of a vulnerability scan: 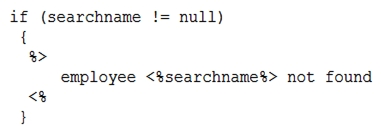 Which of the following types of vulnerabilities does this MOST likely represent?
 (Multiple Choice)
4.8/5 (88)
(88) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)