Multiple Choice
A security analyst recently used Arachni to perform a vulnerability assessment of a newly developed web application. The analyst is concerned about the following output: 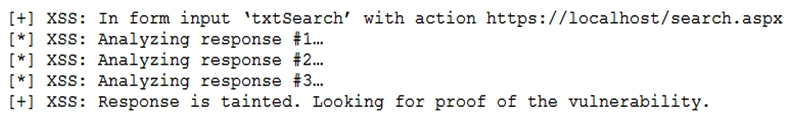 Which of the following is the MOST likely reason for this vulnerability?
A) The developer set input validation protection on the specific field of search.aspx.
B) The developer did not set proper cross-site scripting protections in the header.
C) The developer did not implement default protections in the web application build.
D) The developer did not set proper cross-site request forgery protections.
Correct Answer:

Verified
Correct Answer:
Verified
Q102: A cybersecurity analyst is investigating a potential
Q103: A security analyst discovers accounts in sensitive
Q104: Bootloader malware was recently discovered on several
Q105: During a cyber incident, which of the
Q106: Because some clients have reported unauthorized activity
Q108: A security analyst suspects a malware infection
Q109: It is important to parameterize queries to
Q110: A security analyst discovers a vulnerability on
Q111: An organization wants to move non-essential services
Q112: A security analyst is reviewing the following