



 Chat with AI
Exam 5: ECCouncil Computer Hacking Forensic Investigator

Exam 1: EC-Council Certified Incident Handler80 Questions
Exam 2: Certified Network Defender579 Questions
Exam 3: EC-Council Information Security Manager (E|ISM)131 Questions
Exam 4: EC-Council Certified CISO27 Questions
Exam 5: ECCouncil Computer Hacking Forensic Investigator317 Questions
Exam 6: EC-Council Certified Security Analyst24 Questions
Select questions type


During the reconnaissance phase of a penetration test, you discovered that the client has deployed a firewall that only checks the TCP header information. Which of the following techniques would you use to bypass the firewall?
(Multiple Choice)
4.9/5  (79)
(79) Sam is auditing a web application for SQL injection vulnerabilities. During the testing, Sam discovered that the web application is vulnerable to SQL injection. He starts fuzzing the search field in the web application with UNION based SQL queries, however, he realized that the underlying WAF is blocking the requests. To avoid this, Sam is trying the following query: UNION/**/SELECT/**/'/**/OR/**/1/**/=/**/1 Which of the following evasion techniques is Sam using?
(Multiple Choice)
4.8/5 (73)
(73) Which of the following is the least-likely physical characteristic to be used in biometric control that supports a large company?
(Multiple Choice)
4.7/5 (78)
(78) ABC Technologies, a large financial company, hired a penetration tester to do physical penetration testing. On the first day of his assignment, the penetration tester goes to the company posing as a repairman and starts checking trash bins to collect the sensitive information. What is the penetration tester trying to do?
(Multiple Choice)
5.0/5 (82)
(82) Todd is working on an assignment involving auditing of a web service. The scanning phase reveals the web service is using an Oracle database server at the backend. He wants to check the TNS Listener configuration file for configuration errors. Which of the following directories contains the TNS Listener configuration file, by default:
(Multiple Choice)
4.7/5 (65)
(65) Sam was asked to conduct penetration tests on one of the client's internal networks. As part of the testing process, Sam performed enumeration to gain information about computers belonging to a domain, list of shares on the individual hosts in the network, policies and passwords. Identify the enumeration technique.
(Multiple Choice)
4.8/5 (78)
(78) Which of the following is a common Service Oriented Architecture (SOA) vulnerability?
(Multiple Choice)
4.8/5 (85)
(85) Which of the following parameters describe LM Hash (see exhibit): Exhibit: 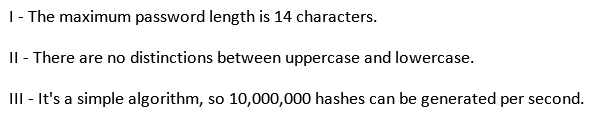
(Multiple Choice)
4.7/5 (80)
(80) Which of the following is used to indicate a single-line comment in structured query language (SQL)?
(Multiple Choice)
4.8/5 (73)
(73) Which of the following processes evaluates the adherence of an organization to its stated security policy?
(Multiple Choice)
4.8/5 (95)
(95) What are the three types of compliance that the Open Source Security Testing Methodology Manual (OSSTMM) recognizes?
(Multiple Choice)
4.9/5 (82)
(82) Michael, a Licensed Penetration Tester, wants to create an exact replica of an original website, so he can browse and spend more time analyzing it. Which of the following tools will Michael use to perform this task?
(Multiple Choice)
4.8/5 (86)
(86) The Open Web Application Security Project (OWASP) is the worldwide not-for-profit charitable organization focused on improving the security of software. What item is the primary concern on OWASP's Top Ten Project Most Critical Web Application Security Risks?
(Multiple Choice)
4.9/5 (71)
(71) Which protocol and port number might be needed in order to send log messages to a log analysis tool that resides behind a firewall?
(Multiple Choice)
5.0/5 (86)
(86) You have just completed a database security audit and writing the draft pen testing report. Which of the following will you include in the recommendation section to enhance the security of the database server?
(Multiple Choice)
4.9/5 (84)
(84) During a penetration test, the tester conducts an ACK scan using NMAP against the external interface of the DMZ firewall. NMAP reports that port 80 is unfiltered. Based on this response, which type of packet inspection is the firewall conducting?
(Multiple Choice)
4.8/5 (79)
(79) Robert is a network admin in XYZ Inc. He deployed a Linux server in his enterprise network and wanted to share some critical and sensitive files that are present in the Linux server with his subordinates. He wants to set the file access permissions using chmod command in such a way that his subordinates can only read/view the files but cannot edit or delete the files. Which of the following chmod commands can Robert use in order to achieve his objective?
(Multiple Choice)
4.8/5 (81)
(81) An organization recently faced a cyberattack where an attacker captured legitimate user credentials and gained access to the critical information systems. He also led other malicious hackers in gaining access to the information systems. To defend and prevent such attacks in future, the organization has decided to route all the incoming and outgoing network traffic through a centralized access proxy apart from validating user credentials. Which of the following defensive mechanisms the organization is trying to strengthen?
(Multiple Choice)
4.8/5 (79)
(79) When using Wireshark to acquire packet capture on a network, which device would enable the capture of all traffic on the wire?
(Multiple Choice)
4.9/5 (65)
(65) After trying multiple exploits, you've gained root access to a Centos 6 server. To ensure you maintain access, what would you do first?
(Multiple Choice)
4.8/5 (78)
(78) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)