



 Chat with AI
Exam 5: ECCouncil Computer Hacking Forensic Investigator

Exam 1: EC-Council Certified Incident Handler80 Questions
Exam 2: Certified Network Defender579 Questions
Exam 3: EC-Council Information Security Manager (E|ISM)131 Questions
Exam 4: EC-Council Certified CISO27 Questions
Exam 5: ECCouncil Computer Hacking Forensic Investigator317 Questions
Exam 6: EC-Council Certified Security Analyst24 Questions
Select questions type


If a tester is attempting to ping a target that exists but receives no response or a response that states the destination is unreachable, ICMP may be disabled and the network may be using TCP. Which other option could the tester use to get a response from a host using TCP?
(Multiple Choice)
4.8/5  (73)
(73) You have several plain-text firewall logs that you must review to evaluate network traffic. You know that in order to do fast, efficient searches of the logs you must use regular expressions. Which command-line utility are you most likely to use?
(Multiple Choice)
4.8/5 (85)
(85) Which of the following scanning tools is specifically designed to find potential exploits in Microsoft Windows products?
(Multiple Choice)
4.8/5 (69)
(69) Which results will be returned with the following Google search query? site:target.com -site:Marketing.target.com accounting
(Multiple Choice)
4.8/5 (69)
(69) Which type of security document is written with specific step-by-step details?
(Multiple Choice)
4.9/5 (88)
(88) Which security strategy requires using several, varying methods to protect IT systems against attacks?
(Multiple Choice)
4.8/5 (75)
(75) Stuart is a database penetration tester working with Regional Server Technologies. He was asked by the company to identify the vulnerabilities in its SQL database. Stuart wanted to perform a SQL penetration by passing some SQL commands through a web application for execution and succeeded with a command using a wildcard attribute indicator. Which of the following strings is a wildcard attribute indicator?
(Multiple Choice)
4.8/5 (63)
(63) Allen and Greg, after investing in their startup company called Zamtac Ltd., developed a new web application for their company. Before hosting the application, they want to test the robustness and immunity of the developed web application against attacks like buffer overflow, DOS, XSS, and SQL injection. What is the type of the web application security test Allen and Greg should perform?
(Multiple Choice)
4.8/5 (79)
(79) A month ago, Jason, a software developer at a reputed IT firm was surfing through his company's website. He was visiting random pages of the company's website and came to find confidential information about the company was posted on one of the web pages. Jason forgot to report the issue. Jason contacted John, another member of the Security Team, and discussed the issue. John visited the page but found nothing wrong. What should John do to see past versions and pages of a website that Jason saw one month back?
(Multiple Choice)
5.0/5 (86)
(86) SecGlobal Corporation hired Michael, a penetration tester. Management asked Michael to perform cloud penetration testing on the company's cloud infrastructure. As a part of his task, he started checking all the agreements with cloud service provider and came to a conclusion that it is not possible to perform penetration testing on the cloud services that are being used by the organization due to the level of responsibilities between company and the Cloud Service Provider (CSP). Identify the type of cloud service deployed by the organization?
(Multiple Choice)
4.9/5 (83)
(83) A certified ethical hacker (CEH) completed a penetration test of the main headquarters of a company almost two months ago, but has yet to get paid. The customer is suffering from financial problems, and the CEH is worried that the company will go out of business and end up not paying. What actions should the CEH take?
(Multiple Choice)
4.8/5 (81)
(81) How can a policy help improve an employee's security awareness?
(Multiple Choice)
4.9/5 (87)
(87) Which of the following is an example of two factor authentication?
(Multiple Choice)
4.8/5 (89)
(89) Which of the following tasks is done after submitting the final pen testing report?
(Multiple Choice)
4.9/5 (72)
(72) Adam is working as a senior penetration tester at Eon Tech Services Ltd. The company asked him to perform penetration testing on their database. The company informs Adam they use Microsoft SQL Server. As a part of the penetration testing, Adam wants to know the complete information about the company's database. He uses the Nmap tool to get the information. Which of the following Nmap commands will Adam use to get the information?
(Multiple Choice)
4.9/5 (92)
(92) While conducting a penetration test, the tester determines that there is a firewall between the tester's machine and the target machine. The firewall is only monitoring TCP handshaking of packets at the session layer of the OSI model. Which type of firewall is the tester trying to traverse?
(Multiple Choice)
4.8/5 (73)
(73) Which tool can be used to silently copy files from USB devices?
(Multiple Choice)
4.9/5 (80)
(80) You are enumerating a target system. Which of the following PortQry commands will give a result similar to the screenshot below: 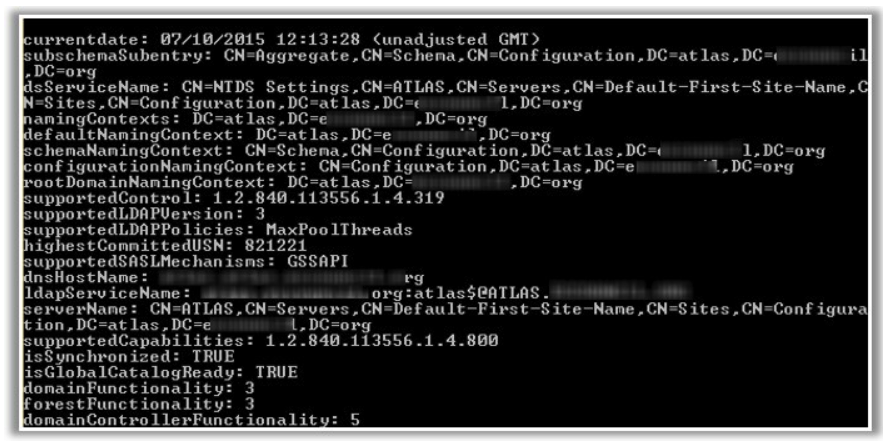
(Multiple Choice)
4.9/5 (68)
(68) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)