



 Chat with AI
Exam 6: EC-Council Certified Security Analyst

Exam 1: EC-Council Certified Incident Handler80 Questions
Exam 2: Certified Network Defender579 Questions
Exam 3: EC-Council Information Security Manager (E|ISM)131 Questions
Exam 4: EC-Council Certified CISO27 Questions
Exam 5: ECCouncil Computer Hacking Forensic Investigator317 Questions
Exam 6: EC-Council Certified Security Analyst24 Questions
Select questions type


A penetration tester at Trinity Ltd. is performing IoT device testing. As part of this process, he is checking the IoT devices for open ports using port scanners such as Nmap. After identifying the open ports, he started using automated tools to check each open port for any exploitable vulnerabilities. Identify the IoT security issues the penetration tester is trying to uncover?

Free
(Multiple Choice)
4.8/5  (92)
(92) Correct Answer: Verified
D
Karen is a Network engineer at ITSec, a reputed MNC based in Philadelphia, USA. She wants to retrieve the DNS records from the publicly available servers. She searched using Google for the providers DNS Information and found the following sites: http://www.dnsstuff.com https://dnsquery.org Through these sites she got the DNS records information as she wished. What information is contained in DNS records?
Free
(Multiple Choice)
4.8/5 (78)
(78) Correct Answer:Verified
VerifiedC
An organization hosted a website to provide services to its customers. A visitor of this website has reported a complaint to the organization that they are getting an error message with code 502 when they are trying to access the website. This issue was forwarded to the IT department in the organization. The IT department identified the reason behind the error and started resolving the issue by checking whether the server is overloaded, whether the name resolution is working properly, whether the firewall is configured properly, etc. Identify the error message corresponding to code 502 that the visitors obtained when they tried to access the organization's website?
Free
(Multiple Choice)
4.8/5 (73)
(73) Correct Answer:Verified
VerifiedD
Michael, a penetration tester of Rolatac Pvt. Ltd., has completed his initial penetration testing and now he needs to create a penetration testing report for company's client, management, and top officials for their reference. For this, he created a report providing a detailed summary of the complete penetration testing process of the project that he has undergone, its outcomes, and recommendations for future testing and exploitation. In the above scenario, which type of penetration testing report has Michael prepared?
(Multiple Choice)
4.8/5 (75)
(75) Which of the following reports should you as an IT auditor use to check on compliance with a service level agreement's requirement for uptime?
(Multiple Choice)
4.9/5 (91)
(91) Recently, Jacob was assigned a project to test the perimeter security of one of a client. As part of the project, Jacob wants to test whether or not a particular port on the firewall is open or closed. He used the hping utility with the following syntax: #hping -S -c 1 -p <port> <IP Address> -t <TTL> What response will indicate the particular port is allowed in the firewall?
(Multiple Choice)
4.8/5 (77)
(77) You are working on a pen testing assignment. Your client has asked for a document that shows them the detailed progress of the pen testing. Which document is the client asking for?
(Multiple Choice)
4.7/5 (77)
(77) James, a research scholar, received an email informing that someone is trying to access his Google account from an unknown device. When he opened his email message, it looked like a standard Google notification instructing him to click the link below to take further steps. This link was redirected to a malicious webpage where he was tricked to provide Google account credentials. James observed that the URL began with www.translate.google.com giving a legitimate appearance. In the above scenario, identify the type of attack being performed on James' email account?
(Multiple Choice)
4.8/5 (88)
(88) Veronica, a penetration tester at a top MNC company, is trying to breach the company's database as a part of SQLi penetration testing. She began to use the SQLi techniques to test the database security level. She inserted new database commands into the SQL statement and appended a SQL Server EXECUTE command to the vulnerable SQL statements. Which of the following SQLi techniques was used to attack the database?
(Multiple Choice)
4.7/5 (66)
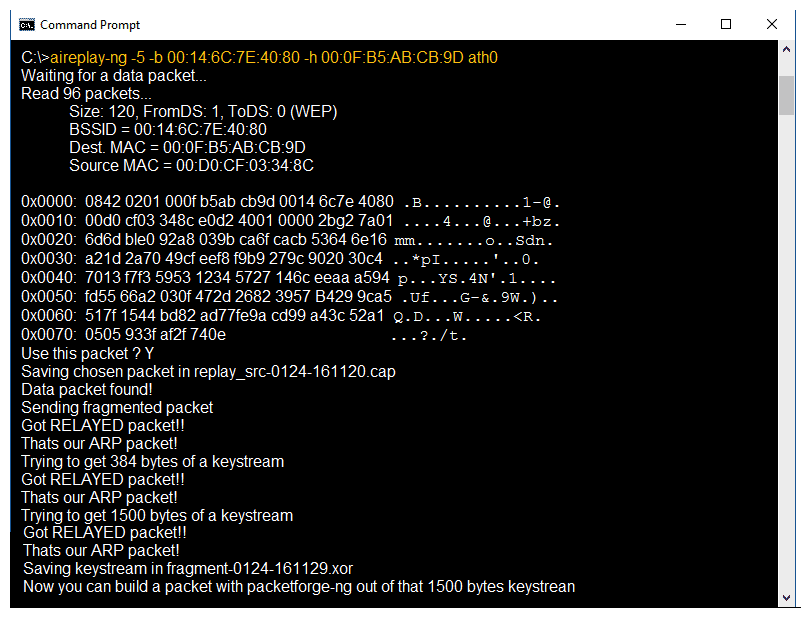
(66) 
Tom is a networking manager in XYZ Inc. He and his team were assigned the task to store and update the confidential files present on a remote server using Network File System (NFS) client-server application protocol. Since the files are confidential, Tom was asked to perform this operation in a secured manner by limiting the access only to his team. As per the instructions provided to him, to use NFS securely, he employed the process of limiting the superuser access privileges only to his team by using authentication based on the team personnel identity. Identify the method employed by Tom for securing access controls in NFS?
(Multiple Choice)
4.8/5 (84)
(84) A user unknowingly installed a fake malicious banking app in his Android mobile. This app includes a configuration file that consists of phone numbers of the bank. When the user makes a call to the bank, he is automatically redirected to the number being used by the attacker. The attacker impersonates as a banking official. Also, the app allows the attacker to call the user, then the app displays fake caller ID on the user's mobile resembling call from a legitimate bank. Identify the attack being performed on the Android mobile user?
(Multiple Choice)
4.9/5 (80)
(80) Jason is a penetration tester, and after completing the initial penetration test, he wanted to create a final penetration test report that consists of all activities performed throughout the penetration testing process. Before creating the final penetration testing report, which of the following reports should Jason prepare in order to verify if any crucial information is missed from the report?
(Multiple Choice)
4.8/5 (75)
(75) Richard, a penetration tester was asked to assess a web application. During the assessment, he discovered a file upload field where users can upload their profile pictures. While scanning the page for vulnerabilities, Richard found a file upload exploit on the website. Richard wants to test the web application by uploading a malicious PHP shell, but the web page denied the file upload. Trying to get around the security, Richard added the ' jpg ' extension to the end of the file. The new file name ended with '.php. jpg '. He then used the Burp suite tool and removed the ' jpg '' extension from the request while uploading the file. This enabled him to successfully upload the PHP shell. Which of the following techniques has Richard implemented to upload the PHP shell?
(Multiple Choice)
4.9/5 (91)
(91) HDC Networks Ltd. is a leading security services company. Matthew works as a penetrating tester with this firm. He was asked to gather information about the target company. Matthew begins with social engineering by following the steps:
(Multiple Choice)
4.8/5 (70)
(70) Gibson, a security analyst at MileTech Solutions, is performing cloud penetration testing. As part of this process, he needs to check for any governance and compliance issues against cloud services. Which of the following documents helps Gibson in checking whether the CSP is regularly audited and certified for compliance issues?
(Multiple Choice)
4.9/5 (79)
(79) Rebecca, a security analyst, was auditing the network in her organization. During the scan, she found a service running on a remote host, which helped her to enumerate information related to user accounts, network interfaces, network routing and TCP connections. Which among the following services allowed Rebecca to enumerate the information?
(Multiple Choice)
4.9/5 (92)
(92) Henderson has completed the pen testing tasks. He is now compiling the final report for the client. Henderson needs to include the result of scanning that revealed a SQL injection vulnerability and different SQL queries that he used to bypass web application authentication. In which section of the pen testing report, should Henderson include this information?
(Multiple Choice)
4.9/5 (79)
(79) Stanley, a pen tester needs to perform various tests to detect SQL injection vulnerabilities. He has to make a list of all input fields whose values could be used in crafting a SQL query. This includes the hidden fields of POST requests and then test them separately, attempting to interfere with the query and cause an error to generate as a result. In which of the following tests is the source code of the application tested in a non-runtime environment to detect the SQL injection vulnerabilities?
(Multiple Choice)
4.9/5 (76)
(76) Steven is performing a wireless network audit. As part of the engagement, he is trying to crack a WPA-PSK key. Steven has captured enough packets to run aircrack-ng and discover the key, but aircrack-ng did not yield any result, as there were no authentication packets in the capture. Which of the following commands should Steven use to generate authentication packets?
(Multiple Choice)
4.8/5 (82)
(82) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)