



 Chat with AI
Exam 5: ECCouncil Computer Hacking Forensic Investigator

Exam 1: EC-Council Certified Incident Handler80 Questions
Exam 2: Certified Network Defender579 Questions
Exam 3: EC-Council Information Security Manager (E|ISM)131 Questions
Exam 4: EC-Council Certified CISO27 Questions
Exam 5: ECCouncil Computer Hacking Forensic Investigator317 Questions
Exam 6: EC-Council Certified Security Analyst24 Questions
Select questions type


Which command line switch would be used in NMAP to perform operating system detection?
(Multiple Choice)
4.9/5  (85)
(85) What is the outcome of the comm"nc -l -p 2222 | nc 10.1.0.43 1234"?
(Multiple Choice)
4.9/5 (80)
(80) While auditing a web application for vulnerabilities, Donald uses Burp proxy and modifies the get requests as below: http://www.example.com/GET/process.php./../../../../../../../../etc/password What is Donald trying to achieve?
(Multiple Choice)
4.7/5 (70)
(70) Nick is a penetration tester in Stanbiz Ltd. As a part of his duty, he was analyzing the network traffic by using various filters in the Wireshark tool. While sniffing the network traffic, he used "tcp.port==1433" Wireshark filter for acquiring a specific database related information since port number 1433 is the default port of that specific target database. Which of the following databases Nick is targeting in his test?
(Multiple Choice)
4.7/5 (76)
(76) An attacker sniffs encrypted traffic from the network and is subsequently able to decrypt it. The attacker can now use which cryptanalytic technique to attempt to discover the encryption key?
(Multiple Choice)
4.9/5 (85)
(85) Which of the following acts provides federal protections for personal health information held by covered entities and gives patients an array of rights with respect to that information?
(Multiple Choice)
4.8/5 (83)
(83) In delivering penetration testing report, which of the following steps should NOT be followed?
(Multiple Choice)
4.8/5 (77)
(77) Russel, a penetration tester after performing the penetration testing, wants to create a report so that he can provide details of the testing process and findings of the vulnerabilities to the management. Russel employs the commonly available vulnerability scoring framework called Common Vulnerability Scoring System (CVSS) v3.0 ratings for grading the severity and risk level of identified vulnerabilities in the report. For a specific SMB-based vulnerability, Russel assigned a score of 8.7. What is the level of risk or level of severity of the SMB vulnerability as per CVSS v3.0 for the assigned score?
(Multiple Choice)
4.8/5 (67)
(67) Which of the following techniques does a vulnerability scanner use in order to detect a vulnerability on a target service?
(Multiple Choice)
4.9/5 (82)
(82) Frank is a senior security analyst at Roger Data Systems Inc. The company asked him to perform a database penetration test on its client network to determine whether the database is vulnerable to attacks or not. The client did not reveal any information about the database they are using. As a pen tester Frank knows that each database runs on its own default port. So he started database port scanning using the Nmap tool and tried different commands using default port numbers and succeeded with the following command. nmap -sU -p 1521 <client ip-address> Identify the database used by the company?
(Multiple Choice)
4.9/5 (72)
(72) Which of the following parameters enables NMAP's operating system detection feature?
(Multiple Choice)
4.8/5 (83)
(83) The penetration testers are required to follow predefined standard frameworks in making penetration testing reporting formats. Which of the following standards does NOT follow the commonly used methodologies in penetration testing?
(Multiple Choice)
4.8/5 (93)
(93) Which of the following is a symmetric cryptographic standard?
(Multiple Choice)
4.7/5 (65)
(65) How do employers protect assets with security policies pertaining to employee surveillance activities?
(Multiple Choice)
4.7/5 (70)
(70) Which solution can be used to emulate computer services, such as mail and ftp, and to capture information related to logins or actions?
(Multiple Choice)
4.9/5 (78)
(78) A developer for a company is tasked with creating a program that will allow customers to update their billing and shipping information. The billing address field used is limited to 50 characters. What pseudo code would the developer use to avoid a buffer overflow attack on the billing address field?
(Multiple Choice)
4.8/5 (69)
(69) Which of the following identifies the three modes in which Snort can be configured to run?
(Multiple Choice)
4.8/5 (78)
(78) Jack, a network engineer, is working on an IPv6 implementation for one of his clients. He deployed IPv6 on IPv4 networks using a mechanism where a node can choose from IPv6 or IPv4 based on the DNS value. This makes the network resources work simpler. What kind of technique did Jack use?
(Multiple Choice)
4.9/5 (76)
(76) This phase will increase the odds of success in later phases of the penetration test. It is also the very first step in Information Gathering, and it will tell you what the "landscape" looks like. What is the most important phase of ethical hacking in which you need to spend a considerable amount of time?
(Multiple Choice)
4.8/5 (86)
(86) Smith, a pen tester, has been hired to analyze the security posture of an organization and is trying to find the operating systems used in the network using Wireshark. What can be inferred about selected packet in the Wireshark screenshot below? 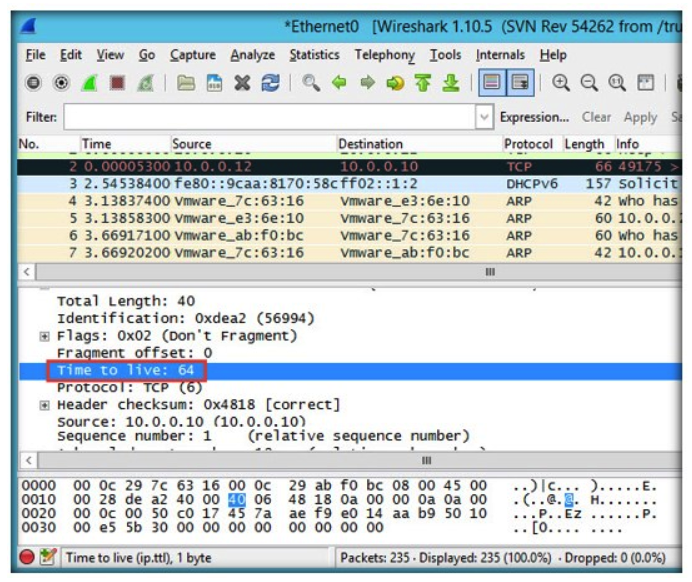
(Multiple Choice)
4.8/5 (85)
(85) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)