



 Chat with AI
Exam 5: Certified Information Privacy Technologist (CIPT)

Exam 1: Certified Information Privacy Manager92 Questions
Exam 2: Certified Information Privacy Professional/Asia (CIPP/A)54 Questions
Exam 3: Certified Information Privacy Professional/Europe (CIPP/E)152 Questions
Exam 4: Certified Information Privacy Professional/United States (CIPP/US)157 Questions
Exam 5: Certified Information Privacy Technologist (CIPT)125 Questions
Select questions type


To comply with the Sarbanes-Oxley Act (SOX), public companies in the United States are required to annually report on the effectiveness of the auditing controls of their financial reporting systems. These controls must be implemented to prevent unauthorized use, disclosure, modification, and damage or loss of financial data. Why do these controls ensure both the privacy and security of data?
(Multiple Choice)
4.9/5  (64)
(64) A privacy engineer reviews a newly developed on-line registration page on a company's website. The purpose of the page is to enable corporate customers to submit a returns / refund request for physical goods. The page displays the following data capture fields: company name, account reference, company address, contact name, email address, contact phone number, product name, quantity, issue description and company bank account details. After her review, the privacy engineer recommends setting certain capture fields as "non-mandatory". Setting which of the following fields as "non-mandatory" would be the best example of the principle of data minimization?
(Multiple Choice)
4.9/5 (87)
(87) SCENARIO Wesley Energy has finally made its move, acquiring the venerable oil and gas exploration firm Lancelot from its long-time owner David Wilson. As a member of the transition team, you have come to realize that Wilson's quirky nature affected even Lancelot's data practices, which are maddeningly inconsistent. "The old man hired and fired IT people like he was changing his necktie," one of Wilson's seasoned lieutenants tells you, as you identify the traces of initiatives left half complete. For instance, while some proprietary data and personal information on clients and employees is encrypted, other sensitive information, including health information from surveillance testing of employees for toxic exposures, remains unencrypted, particularly when included within longer records with less-sensitive data. You also find that data is scattered across applications, servers and facilities in a manner that at first glance seems almost random. Among your preliminary findings of the condition of data at Lancelot are the following: Cloud technology is supplied by vendors around the world, including firms that you have not heard of. You are told by a former Lancelot employee that these vendors operate with divergent security requirements and protocols. The company's proprietary recovery process for shale oil is stored on servers among a variety of less-sensitive information that can be accessed not only by scientists, but by personnel of all types at most company locations. DES is the strongest encryption algorithm currently used for any file. Several company facilities lack physical security controls, beyond visitor check-in, which familiar vendors often bypass. Fixing all of this will take work, but first you need to grasp the scope of the mess and formulate a plan of action to address it. Which procedure should be employed to identify the types and locations of data held by Wesley Energy?
(Multiple Choice)
4.8/5 (84)
(84) SCENARIO Clean-Q is a company that offers house-hold and office cleaning services. The company receives requests from consumers via their website and telephone, to book cleaning services. Based on the type and size of service, Clean-Q then contracts individuals that are registered on its resource database - currently managed in-house by Clean-Q IT Support. Because of Clean-Q's business model, resources are contracted as needed instead of permanently employed. The table below indicates some of the personal information Clean-Q requires as part of its business operations: 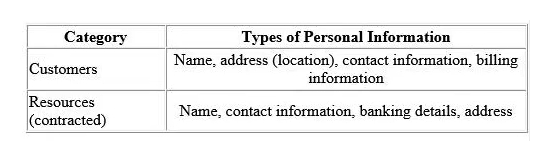 Clean-Q has an internal employee base of about 30 people. A recent privacy compliance exercise has been conducted to align employee data management and human resource functions with applicable data protection regulation. Therefore, the Clean-Q permanent employee base is not included as part of this scenario. With an increase in construction work and housing developments, Clean-Q has had an influx of requests for cleaning services. The demand has overwhelmed Clean-Q's traditional supply and demand system that has caused some overlapping bookings. In a business strategy session held by senior management recently, Clear-Q invited vendors to present potential solutions to their current operational issues. These vendors included Application developers and cloud solution providers, presenting their proposed solutions and platforms. The Managing Director opted to initiate the process to integrate Clean-Q's operations with a cloud solution (LeadOps) that will provide the following solution one single online platform: A web interface that Clean-Q accesses for the purposes of resource and customer management. This would entail uploading resource and customer information. A customer facing web interface that enables customers to register, manage and submit cleaning service requests online. A resource facing web interface that enables resources to apply and manage their assigned jobs. An online payment facility for customers to pay for services. If Clean-Q were to utilize LeadOps' services, what is a contract clause that may be included in the agreement entered into with LeadOps?
 (Multiple Choice)
4.9/5 (79)
(79) Which of the following is an example of the privacy risks associated with the Internet of Things (loT)?
(Multiple Choice)
4.9/5 (83)
(83) SCENARIO Carol was a U.S.-based glassmaker who sold her work at art festivals. She kept things simple by only accepting cash and personal checks. As business grew, Carol couldn't keep up with demand, and traveling to festivals became burdensome. Carol opened a small boutique and hired Sam to run it while she worked in the studio. Sam was a natural salesperson, and business doubled. Carol told Sam, "I don't know what you are doing, but keep doing it!" But months later, the gift shop was in chaos. Carol realized that Sam needed help so she hired Jane, who had business expertise and could handle the back-office tasks. Sam would continue to focus on sales. Carol gave Jane a few weeks to get acquainted with the artisan craft business, and then scheduled a meeting for the three of them to discuss Jane's first impressions. At the meeting, Carol could not wait to hear Jane's thoughts, but she was unprepared for what Jane had to say. "Carol, I know that he doesn't realize it, but some of Sam's efforts to increase sales have put you in a vulnerable position. You are not protecting customers' personal information like you should." Sam said, "I am protecting our information. I keep it in the safe with our bank deposit. It's only a list of customers' names, addresses and phone numbers that I get from their checks before I deposit them. I contact them when you finish a piece that I think they would like. That's the only information I have! The only other thing I do is post photos and information about your work on the photo sharing site that I use with family and friends. I provide my email address and people send me their information if they want to see more of your work. Posting online really helps sales, Carol. In fact, the only complaint I hear is about having to come into the shop to make a purchase." Carol replied, "Jane, that doesn't sound so bad. Could you just fix things and help us to post even more online?" 'I can," said Jane. "But it's not quite that simple. I need to set up a new program to make sure that we follow the best practices in data management. And I am concerned for our customers. They should be able to manage how we use their personal information. We also should develop a social media strategy." Sam and Jane worked hard during the following year. One of the decisions they made was to contract with an outside vendor to manage online sales. At the end of the year, Carol shared some exciting news. "Sam and Jane, you have done such a great job that one of the biggest names in the glass business wants to buy us out! And Jane, they want to talk to you about merging all of our customer and vendor information with theirs beforehand." Which regulator has jurisdiction over the shop's data management practices?
(Multiple Choice)
4.7/5 (81)
(81) SCENARIO Please use the following to answer the next question: Looking back at your first two years as the Director of Personal Information Protection and Compliance for the St. Anne's Regional Medical Center in Thorn Bay, Ontario, Canada, you see a parade of accomplishments, from developing state-of-the-art simulation based training for employees on privacy protection to establishing an interactive medical records system that is accessible by patients as well as by the medical personnel. Now, however, a question you have put off looms large: how do we manage all the data-not only records produced recently, but those still on-hand from years ago? A data flow diagram generated last year shows multiple servers, databases, and work stations, many of which hold files that have not yet been incorporated into the new records system. While most of this data is encrypted, its persistence may pose security and compliance concerns. The situation is further complicated by several long-term studies being conducted by the medical staff using patient information. Having recently reviewed the major Canadian privacy regulations, you want to make certain that the medical center is observing them. You recall a recent visit to the Records Storage Section in the basement of the old hospital next to the modern facility, where you noticed paper records sitting in crates labeled by years, medical condition or alphabetically by patient name, while others were in undifferentiated bundles on shelves and on the floor. On the back shelves of the section sat data tapes and old hard drives that were often unlabeled but appeared to be years old. On your way out of the records storage section, you noticed a man leaving whom you did not recognize. He carried a batch of folders under his arm, apparently records he had removed from storage. You quickly realize that you need a plan of action on the maintenance, secure storage and disposal of data. Which cryptographic standard would be most appropriate for protecting patient credit card information in the records system at St. Anne's Regional Medical Center?
(Multiple Choice)
4.7/5 (92)
(92) Revocation and reissuing of compromised credentials is impossible for which of the following authentication techniques?
(Multiple Choice)
4.8/5 (68)
(68) SCENARIO WebTracker Limited is a cloud-based online marketing service located in London. Last year, WebTracker migrated its IT infrastructure to the cloud provider AmaZure, which provides SQL Databases and Artificial Intelligence services to WebTracker. The roles and responsibilities between the two companies have been formalized in a standard contract, which includes allocating the role of data controller to WebTracker. The CEO of WebTracker, Mr. Bond, would like to assess the effectiveness of AmaZure's privacy controls, and he recently decided to hire you as an independent auditor. The scope of the engagement is limited only to the marketing services provided by WebTracker, you will not be evaluating any internal data processing activity, such as HR or Payroll. This ad-hoc audit was triggered due to a future partnership between WebTracker and SmartHome - a partnership that will not require any data sharing. SmartHome is based in the USA, and most recently has dedicated substantial resources to developing smart refrigerators that can suggest the recommended daily calorie intake based on DNA information. This and other personal data is collected by WebTracker. To get an idea of the scope of work involved, you have decided to start reviewing the company's documentation and interviewing key staff to understand potential privacy risks. The results of this initial work include the following notes: There are several typos in the current privacy notice of WebTracker, and you were not able to find the privacy notice for SmartHome. You were unable to identify all the sub-processors working for SmartHome. No subcontractor is indicated in the cloud agreement with AmaZure, which is responsible for the support and maintenance of the cloud infrastructure. There are data flows representing personal data being collected from the internal employees of WebTracker, including an interface from the HR system. Part of the DNA data collected by WebTracker was from employees, as this was a prototype approved by the CEO of WebTracker. All the WebTracker and SmartHome customers are based in USA and Canada. Which of the following issues is most likely to require an investigation by the Chief Privacy Officer (CPO) of WebTracker?
(Multiple Choice)
4.8/5 (100)
(100) SCENARIO Clean-Q is a company that offers house-hold and office cleaning services. The company receives requests from consumers via their website and telephone, to book cleaning services. Based on the type and size of service, Clean-Q then contracts individuals that are registered on its resource database - currently managed in-house by Clean-Q IT Support. Because of Clean-Q's business model, resources are contracted as needed instead of permanently employed. The table below indicates some of the personal information Clean-Q requires as part of its business operations: 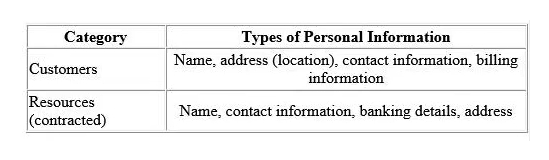 Clean-Q has an internal employee base of about 30 people. A recent privacy compliance exercise has been conducted to align employee data management and human resource functions with applicable data protection regulation. Therefore, the Clean-Q permanent employee base is not included as part of this scenario. With an increase in construction work and housing developments, Clean-Q has had an influx of requests for cleaning services. The demand has overwhelmed Clean-Q's traditional supply and demand system that has caused some overlapping bookings. Ina business strategy session held by senior management recently, Clear-Q invited vendors to present potential solutions to their current operational issues. These vendors included Application developers and Cloud-Q's solution providers, presenting their proposed solutions and platforms. The Managing Director opted to initiate the process to integrate Clean-Q's operations with a cloud solution (LeadOps) that will provide the following solution one single online platform: A web interface that Clean-Q accesses for the purposes of resource and customer management. This would entail uploading resource and customer information. A customer facing web interface that enables customers to register, manage and submit cleaning service requests online. A resource facing web interface that enables resources to apply and manage their assigned jobs. An online payment facility for customers to pay for services. Which question would you most likely ask to gain more insight about LeadOps and provide practical privacy recommendations?
 (Multiple Choice)
4.9/5 (71)
(71) Which of the following does NOT illustrate the 'respect to user privacy' principle?
(Multiple Choice)
4.8/5 (68)
(68) SCENARIO Looking back at your first two years as the Director of Personal Information Protection and Compliance for the Berry Country Regional Medical Center in Thorn Bay, Ontario, Canada, you see a parade of accomplishments, from developing state-of-the-art simulation based training for employees on privacy protection to establishing an interactive medical records system that is accessible by patients as well as by the medical personnel. Now, however, a question you have put off looms large: how do we manage all the data-not only records produced recently, but those still on hand from years ago? A data flow diagram generated last year shows multiple servers, databases, and work stations, many of which hold files that have not yet been incorporated into the new records system. While most of this data is encrypted, its persistence may pose security and compliance concerns. The situation is further complicated by several long-term studies being conducted by the medical staff using patient information. Having recently reviewed the major Canadian privacy regulations, you want to make certain that the medical center is observing them. You also recall a recent visit to the Records Storage Section, often termed "The Dungeon" in the basement of the old hospital next to the modern facility, where you noticed a multitude of paper records. Some of these were in crates marked by years, medical condition or alphabetically by patient name, while others were in undifferentiated bundles on shelves and on the floor. The back shelves of the section housed data tapes and old hard drives that were often unlabeled but appeared to be years old. On your way out of the dungeon, you noticed just ahead of you a small man in a lab coat who you did not recognize. He carried a batch of folders under his arm, apparently records he had removed from storage. Which regulation most likely applies to the data stored by Berry Country Regional Medical Center?
(Multiple Choice)
5.0/5 (75)
(75) What is the main reason the Do Not Track (DNT) header is not acknowledged by more companies?
(Multiple Choice)
4.8/5 (90)
(90) In the realm of artificial intelligence, how has deep learning enabled greater implementation of machine learning?
(Multiple Choice)
4.9/5 (75)
(75) A key principle of an effective privacy policy is that it should be?
(Multiple Choice)
4.9/5 (90)
(90) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)