



 Chat with AI
Exam 5: Certified Information Privacy Technologist (CIPT)

Exam 1: Certified Information Privacy Manager92 Questions
Exam 2: Certified Information Privacy Professional/Asia (CIPP/A)54 Questions
Exam 3: Certified Information Privacy Professional/Europe (CIPP/E)152 Questions
Exam 4: Certified Information Privacy Professional/United States (CIPP/US)157 Questions
Exam 5: Certified Information Privacy Technologist (CIPT)125 Questions
Select questions type


SCENARIO Clean-Q is a company that offers house-hold and office cleaning services. The company receives requests from consumers via their website and telephone, to book cleaning services. Based on the type and size of service, Clean-Q then contracts individuals that are registered on its resource database - currently managed in-house by Clean-Q IT Support. Because of Clean-Q's business model, resources are contracted as needed instead of permanently employed. The table below indicates some of the personal information Clean-Q requires as part of its business operations: 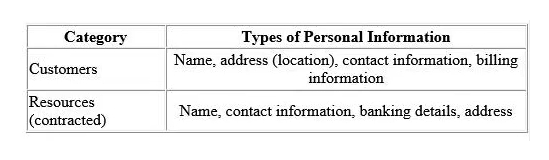 Clean-Q has an internal employee base of about 30 people. A recent privacy compliance exercise has been conducted to align employee data management and human resource functions with applicable data protection regulation. Therefore, the Clean-Q permanent employee base is not included as part of this scenario. With an increase in construction work and housing developments, Clean-Q has had an influx of requests for cleaning services. The demand has overwhelmed Clean-Q's traditional supply and demand system that has caused some overlapping bookings. In a business strategy session held by senior management recently, Clear-Q invited vendors to present potential solutions to their current operational issues. These vendors included Application developers and cloud solution providers, presenting their proposed solutions and platforms. The Managing Director opted to initiate the process to integrate Clean-Q's operations with a cloud solution (LeadOps) that will provide the following solution one single online platform: A web interface that Clean-Q accesses for the purposes of resource and customer management. This would entail uploading resource and customer information. A customer facing web interface that enables customers to register, manage and submit cleaning service requests online. A resource facing web interface that enables resources to apply and manage their assigned jobs. An online payment facility for customers to pay for services. Considering that LeadOps will host/process personal information on behalf of Clean-Q remotely, what is an appropriate next step for Clean-Q senior management to assess LeadOps' appropriateness?
 (Multiple Choice)
4.8/5  (79)
(79) Which of the following is NOT a workplace surveillance best practice?
(Multiple Choice)
4.8/5 (76)
(76) An organization based in California, USA is implementing a new online helpdesk solution for recording customer call information. The organization considers the capture of personal data on the online helpdesk solution to be in the interest of the company in best servicing customer calls. Before implementation, a privacy technologist should conduct which of the following?
(Multiple Choice)
4.9/5 (79)
(79) A sensitive biometrics authentication system is particularly susceptible to?
(Multiple Choice)
4.8/5 (87)
(87) What is the main benefit of using dummy data during software testing?
(Multiple Choice)
4.8/5 (88)
(88) SCENARIO Clean-Q is a company that offers house-hold and office cleaning services. The company receives requests from consumers via their website and telephone, to book cleaning services. Based on the type and size of service, Clean-Q then contracts individuals that are registered on its resource database - currently managed in-house by Clean-Q IT Support. Because of Clean-Q's business model, resources are contracted as needed instead of permanently employed. The table below indicates some of the personal information Clean-Q requires as part of its business operations: 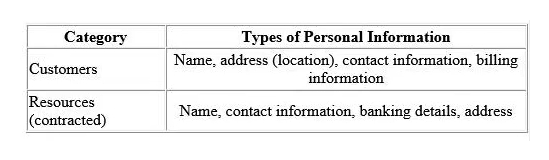 Clean-Q has an internal employee base of about 30 people. A recent privacy compliance exercise has been conducted to align employee data management and human resource functions with applicable data protection regulation. Therefore, the Clean-Q permanent employee base is not included as part of this scenario. With an increase in construction work and housing developments, Clean-Q has had an influx of requests for cleaning services. The demand has overwhelmed Clean-Q's traditional supply and demand system that has caused some overlapping bookings. In a business strategy session held by senior management recently, Clear-Q invited vendors to present potential solutions to their current operational issues. These vendors included Application developers and cloud solution providers, presenting their proposed solutions and platforms. The Managing Director opted to initiate the process to integrate Clean-Q's operations with a cloud solution (LeadOps) that will provide the following solution one single online platform: A web interface that Clean-Q accesses for the purposes of resource and customer management. This would entail uploading resource and customer information. A customer facing web interface that enables customers to register, manage and submit cleaning service requests online. A resource facing web interface that enables resources to apply and manage their assigned jobs. An online payment facility for customers to pay for services. What is a key consideration for assessing external service providers like LeadOps, which will conduct personal information processing operations on Clean-Q's behalf?
 (Multiple Choice)
4.8/5 (81)
(81) What has been identified as a significant privacy concern with chatbots?
(Multiple Choice)
4.8/5 (80)
(80) After committing to a Privacy by Design program, which activity should take place first ?
(Multiple Choice)
5.0/5 (83)
(83) What is the distinguishing feature of asymmetric encryption?
(Multiple Choice)
4.9/5 (71)
(71) SCENARIO Looking back at your first two years as the Director of Personal Information Protection and Compliance for the Berry Country Regional Medical Center in Thorn Bay, Ontario, Canada, you see a parade of accomplishments, from developing state-of-the-art simulation based training for employees on privacy protection to establishing an interactive medical records system that is accessible by patients as well as by the medical personnel. Now, however, a question you have put off looms large: how do we manage all the data-not only records produced recently, but those still on hand from years ago? A data flow diagram generated last year shows multiple servers, databases, and work stations, many of which hold files that have not yet been incorporated into the new records system. While most of this data is encrypted, its persistence may pose security and compliance concerns. The situation is further complicated by several long-term studies being conducted by the medical staff using patient information. Having recently reviewed the major Canadian privacy regulations, you want to make certain that the medical center is observing them. You also recall a recent visit to the Records Storage Section, often termed "The Dungeon" in the basement of the old hospital next to the modern facility, where you noticed a multitude of paper records. Some of these were in crates marked by years, medical condition or alphabetically by patient name, while others were in undifferentiated bundles on shelves and on the floor. The back shelves of the section housed data tapes and old hard drives that were often unlabeled but appeared to be years old. On your way out of the dungeon, you noticed just ahead of you a small man in a lab coat who you did not recognize. He carried a batch of folders under his arm, apparently records he had removed from storage. Which data lifecycle phase needs the most attention at this Ontario medical center?
(Multiple Choice)
4.8/5 (89)
(89) SCENARIO Please use the following to answer the next question: Chuck, a compliance auditor for a consulting firm focusing on healthcare clients, was required to travel to the client's office to perform an onsite review of the client's operations. He rented a car from Finley Motors upon arrival at the airport as so he could commute to and from the client's office. The car rental agreement was electronically signed by Chuck and included his name, address, driver's license, make/model of the car, billing rate, and additional details describing the rental transaction. On the second night, Chuck was caught by a red light camera not stopping at an intersection on his way to dinner. Chuck returned the car back to the car rental agency at the end week without mentioning the infraction and Finley Motors emailed a copy of the final receipt to the address on file. Local law enforcement later reviewed the red light camera footage. As Finley Motors is the registered owner of the car, a notice was sent to them indicating the infraction and fine incurred. This notice included the license plate number, occurrence date and time, a photograph of the driver, and a web portal link to a video clip of the violation for further review. Finley Motors, however, was not responsible for the violation as they were not driving the car at the time and transferred the incident to AMP Payment Resources for further review. AMP Payment Resources identified Chuck as the driver based on the rental agreement he signed when picking up the car and then contacted Chuck directly through a written letter regarding the infraction to collect the fine. After reviewing the incident through the AMP Payment Resources' web portal, Chuck paid the fine using his personal credit card. Two weeks later, Finley Motors sent Chuck an email promotion offering 10% off a future rental. How can Finley Motors reduce the risk associated with transferring Chuck's personal information to AMP Payment Resources?
(Multiple Choice)
4.7/5 (82)
(82) SCENARIO Looking back at your first two years as the Director of Personal Information Protection and Compliance for the Berry Country Regional Medical Center in Thorn Bay, Ontario, Canada, you see a parade of accomplishments, from developing state-of-the-art simulation based training for employees on privacy protection to establishing an interactive medical records system that is accessible by patients as well as by the medical personnel. Now, however, a question you have put off looms large: how do we manage all the data-not only records produced recently, but those still on hand from years ago? A data flow diagram generated last year shows multiple servers, databases, and work stations, many of which hold files that have not yet been incorporated into the new records system. While most of this data is encrypted, its persistence may pose security and compliance concerns. The situation is further complicated by several long-term studies being conducted by the medical staff using patient information. Having recently reviewed the major Canadian privacy regulations, you want to make certain that the medical center is observing them. You also recall a recent visit to the Records Storage Section, often termed "The Dungeon" in the basement of the old hospital next to the modern facility, where you noticed a multitude of paper records. Some of these were in crates marked by years, medical condition or alphabetically by patient name, while others were in undifferentiated bundles on shelves and on the floor. The back shelves of the section housed data tapes and old hard drives that were often unlabeled but appeared to be years old. On your way out of the dungeon, you noticed just ahead of you a small man in a lab coat who you did not recognize. He carried a batch of folders under his arm, apparently records he had removed from storage. Which cryptographic standard would be most appropriate for protecting patient credit card information in the records system?
(Multiple Choice)
5.0/5 (64)
(64) Properly configured databases and well-written website codes are the best protection against what online threat?
(Multiple Choice)
4.8/5 (84)
(84) Which is NOT a suitable method for assuring the quality of data collected by a third-party company?
(Multiple Choice)
4.9/5 (92)
(92) What can be used to determine the type of data in storage without exposing its contents?
(Multiple Choice)
4.8/5 (83)
(83) During a transport layer security (TLS) session, what happens immediately after the web browser creates a random PreMasterSecret?
(Multiple Choice)
4.9/5 (92)
(92) Which of the following most embodies the principle of Data Protection by Default?
(Multiple Choice)
4.9/5 (79)
(79) All of the following can be indications of a ransomware attack EXCEPT?
(Multiple Choice)
4.8/5 (76)
(76) 
Filters
- Essay(0)
- Multiple Choice(0)
- Short Answer(0)
- True False(0)
- Matching(0)